





CVE-2019-10068: Kentico CMS Insecure Deserialization Remote Code Execution
漏洞标题 CVE-2019-10068: Kentico CMS Insecure Deserialization Remote Code Execution 漏洞描述 Kentico CMS is susceptible to remote code execution via a .NET deserialization vulnerab...

docker内网搭建dns使用域名访问替代ip:port的操作_docker
这篇文章主要介绍了docker内网搭建dns使用域名访问替代ip:port的操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 比如我内网有个jenkins,我如果要访问它我得牢牢记住它...
CVE-2018-13379: Fortinet FortiOS – Credentials Disclosure
漏洞标题 CVE-2018-13379: Fortinet FortiOS - Credentials Disclosure 漏洞描述 Fortinet FortiOS 6.0.0 to 6.0.4, 5.6.3 to 5.6.7 and 5.4.6 to 5.4.12 and FortiProxy 2.0.0, 1.2.0 to 1.2.8...
CVE-2024-24763: JumpServer < 3.10.0 - Open Redirect
漏洞标题 CVE-2024-24763: JumpServer < 3.10.0 - Open Redirect 漏洞描述 JumpServer is an open source bastion host and an operation and maintenance security audit system. Prior to ...
CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape
漏洞标题 CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow...
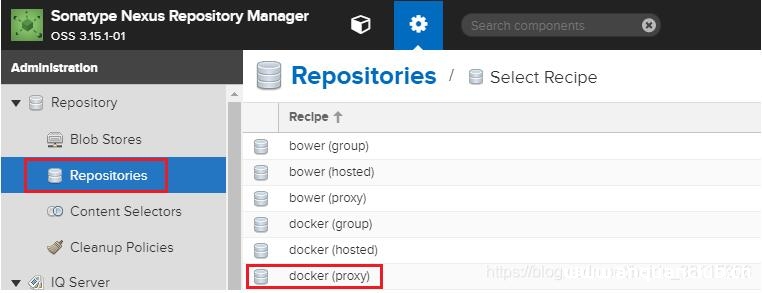
利用nexus作为私库进行代理docker,进行上传和下载镜像操作_docker
这篇文章主要介绍了利用nexus作为私库进行代理docker,进行上传和下载镜像操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 一、nexus的配置 1.创建docker proxy 用于从外...
Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805)
漏洞标题 Apache Struts2(S2-062)远程代码执行漏洞(CVE-2021-31805) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Apache Struts< 2.5.30存在OGNL表达式注入漏...
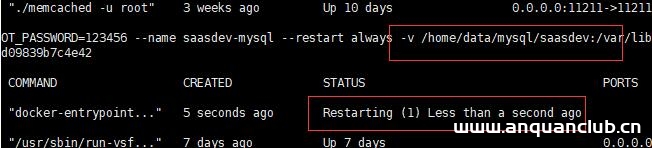
docker run -v 挂载数据卷异常,容器状态一直是restarting的解决_docker
这篇文章主要介绍了docker run -v 挂载数据卷异常,容器状态一直是restarting的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 出现的问题: docker run 加上 -v 参...
CVE-2022-40359: Kae’s File Manager <=1.4.7 - Cross-Site Scripting
漏洞标题 CVE-2022-40359: Kae's File Manager <=1.4.7 - Cross-Site Scripting 漏洞描述 Kae's File Manager through 1.4.7 contains a cross-site scripting vulnerability via ...

intellij idea 使用Tomcat部署的项目位置在哪_Tomcat
intellij idea 使用Tomcat部署的项目在哪里,为什么不在Tomcat的webapps目录下面,本文通过图文实例相结合给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友参考下吧...
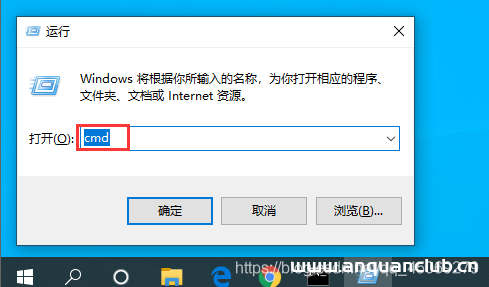
如何解决点击 tomcat9.exe闪退的问题_Tomcat
这篇文章主要介绍了如何解决点击 tomcat9.exe闪退的问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 有读者联系问,怎么tomcat启动都会出现问...
CVE-2023-27847: PrestaShop xipblog – SQL Injection
漏洞标题 CVE-2023-27847: PrestaShop xipblog - SQL Injection 漏洞描述 In the blog module (xipblog), an anonymous user can perform SQL injection. Even though the module has been patc...
CVE-2024-4956: Nexus Repository Manager 文件读取漏洞
漏洞标题 CVE-2024-4956: Nexus Repository Manager 文件读取漏洞 漏洞描述 Path Traversal in Sonatype Nexus Repository 3 allows an unauthenticated attacker to read system files. Fixed ...
CVE-2025-49002: DataEase 远程代码执行漏洞
漏洞标题 CVE-2025-49002: DataEase 远程代码执行漏洞 漏洞描述 CVE-2025-49002 是由于H2数据库模块没有严格过滤用户输入的JDBC连接参数,可使用大小写绕过补丁。攻击者可利用这些漏洞实现未授...
CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion
漏洞标题 CVE-2020-15050: Suprema BioStar <2.8.2 - Local File Inclusion 漏洞描述 Suprema BioStar before 2.8.2 Video Extension allows remote attackers can read arbitrary files fro...

