




再分享6个可无限激活阿里云盘邀请码,不信你不能激活阿里云盘_云其它
这篇文章主要分享6个可无限激活的阿里云盘邀请码,不信你不能激活阿里云盘,需要的朋友可以参考下 阿里云盘距离上次更新已过去不少时间了,据网友反应已经有部分前期参加“个人种子”活动的用户...

CVE-2023-33629: H3C Magic R300-2100M – Remote Code Execution
漏洞标题 CVE-2023-33629: H3C Magic R300-2100M - Remote Code Execution 漏洞描述 H3C Magic R300 version R300-2100MV100R004 was discovered to contain a stack overflow via the Deltrigg...
CVE-2022-37042: Zimbra Collaboration Suite 8.8.15/9.0 – Remote Code Execution
漏洞标题 CVE-2022-37042: Zimbra Collaboration Suite 8.8.15/9.0 - Remote Code Execution 漏洞描述 Zimbra Collaboration Suite (ZCS) 8.8.15 and 9.0 has mboximport functionality that re...
CVE-2023-37645: EyouCms v1.6.3 – Information Disclosure
漏洞标题 CVE-2023-37645: EyouCms v1.6.3 - Information Disclosure 漏洞描述 EyouCms v1.6.3 was discovered to contain an information disclosure vulnerability via the component /custom...
CVE-2018-1207: Dell iDRAC7/8 Devices – Remote Code Injection
漏洞标题 CVE-2018-1207: Dell iDRAC7/8 Devices - Remote Code Injection 漏洞描述 Dell EMC iDRAC7/iDRAC8, versions prior to 2.52.52.52, contain a CGI injection vulnerability which cou...
CVE-2023-6246: glibc’s syslog – Local Privilege Escalation
漏洞标题 CVE-2023-6246: glibc's syslog - Local Privilege Escalation 漏洞描述 A heap-based buffer overflow was found in the __vsyslog_internal function of the glibc library. Th...
CVE-2025-53364: Parse Server – GraphQL Schema Information Disclosure
漏洞标题 CVE-2025-53364: Parse Server - GraphQL Schema Information Disclosure 漏洞描述 The Parse Server GraphQL API previously allowed public access to the GraphQL schema without r...
CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668)
漏洞标题 CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway – Remote Code Injection
漏洞标题 CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway - Remote Code Injection 漏洞描述 Citrix ADC and NetScaler Gateway are susceptible to remote code injection. An attac...
CVE-2024-13159: Ivanti EPM – Credential Coercion Vulnerability in GetHashForWildcardRecursive
漏洞标题 CVE-2024-13159: Ivanti EPM - Credential Coercion Vulnerability in GetHashForWildcardRecursive 漏洞描述 A vulnerability in Ivanti Endpoint Manager (EPM) allows an unauthent...
CVE-2023-36306: Adiscon LogAnalyzer v.4.1.13 – Cross-Site Scripting
漏洞标题 CVE-2023-36306: Adiscon LogAnalyzer v.4.1.13 - Cross-Site Scripting 漏洞描述 A Cross Site Scripting (XSS) vulnerability in Adiscon Aiscon LogAnalyzer through 4.1.13 allows...
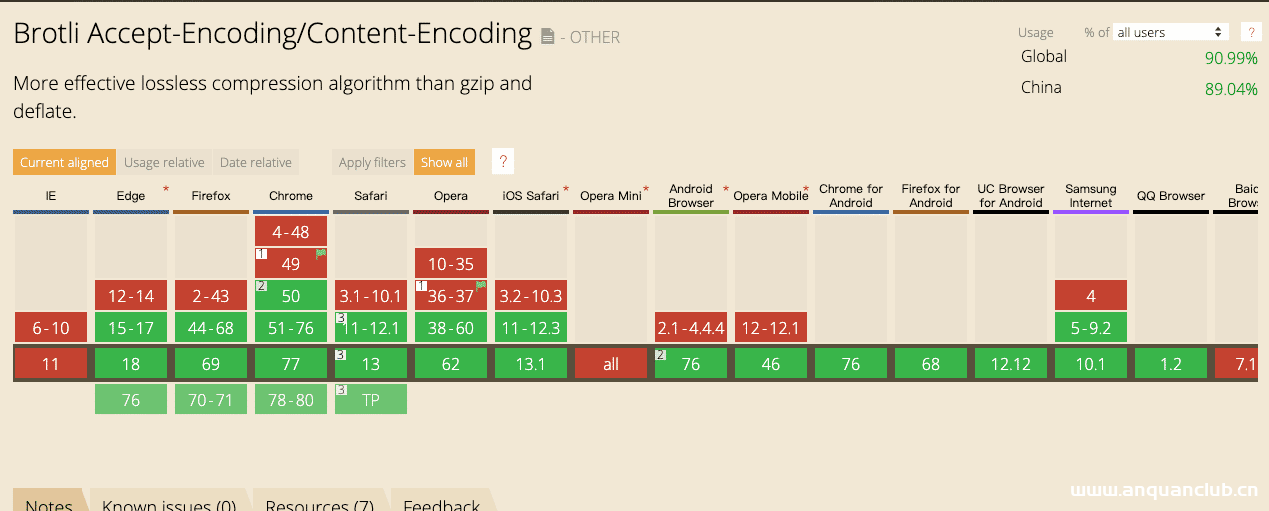
Nginx开启Brotli压缩算法实现过程详解_nginx
这篇文章主要介绍了Nginx开启Brotli压缩算法实现过程详解,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 前言 在web应用中,为了节省流量...
CVE-2025-41243: Spring Cloud Gateway Server Webflux – Broken Access Control
漏洞标题 CVE-2025-41243: Spring Cloud Gateway Server Webflux - Broken Access Control 漏洞描述 Spring Cloud Gateway Server Webflux contains a vulnerability caused by unsecured and e...
CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass
漏洞标题 CVE-2023-2734: MStore API <= 3.9.1 - Authentication Bypass 漏洞描述 The MStore API plugin for WordPress is vulnerable to authentication bypass in versions up to, and in...
CVE-2024-1561: Gradio 4.3-4.12 – Local File Read
漏洞标题 CVE-2024-1561: Gradio 4.3-4.12 - Local File Read 漏洞描述 Local file read by calling arbitrary methods of Components class between Gradio versions 4.3-4.12 PoC代码
CVE-2019-12990: Citrix SD-WAN Center – Local File Inclusion
漏洞标题 CVE-2019-12990: Citrix SD-WAN Center - Local File Inclusion 漏洞描述 Citrix SD-WAN Center is susceptible to local file inclusion via the applianceSettingsFileTransfer func...

