





CVE-2008-5281: Titan FTP Server 6.05 DELE Command – Heap Overflow
漏洞标题 CVE-2008-5281: Titan FTP Server 6.05 DELE Command - Heap Overflow 漏洞描述 Titan FTP Server version 6.05 build 550 contains a heap overflow vulnerability when processing l...
CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837)
漏洞标题 CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837) 漏洞描述 该漏洞可以通过请求api的路径接口来进行SQL注入,进而可能导致敏感信息泄露,该注入可暴露后...
CVE-2023-43261: Milesight Routers – Information Disclosure
漏洞标题 CVE-2023-43261: Milesight Routers - Information Disclosure 漏洞描述 A critical security vulnerability has been identified in Milesight Industrial Cellular Routers, comprom...
CVE-2017-18362: Kaseya VSA 2017 ConnectWise ManagedITSync – Remote Code Execution
漏洞标题 CVE-2017-18362: Kaseya VSA 2017 ConnectWise ManagedITSync - Remote Code Execution 漏洞描述 ConnectWise ManagedITSync integration through 2017 for Kaseya VSA is vulnerable ...
CVE-2024-4455: YITH WooCommerce Ajax Search <= 2.4.0 - Cross-Site Scripting
漏洞标题 CVE-2024-4455: YITH WooCommerce Ajax Search <= 2.4.0 - Cross-Site Scripting 漏洞描述 The YITH WooCommerce Ajax Search plugin for WordPress is vulnerable to Stored Cross...
CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
CVE-2023-4596: WordPress Plugin Forminator 1.24.6 – Arbitrary File Upload
漏洞标题 CVE-2023-4596: WordPress Plugin Forminator 1.24.6 - Arbitrary File Upload 漏洞描述 The Forminator plugin for WordPress is vulnerable to arbitrary file uploads due to file ...
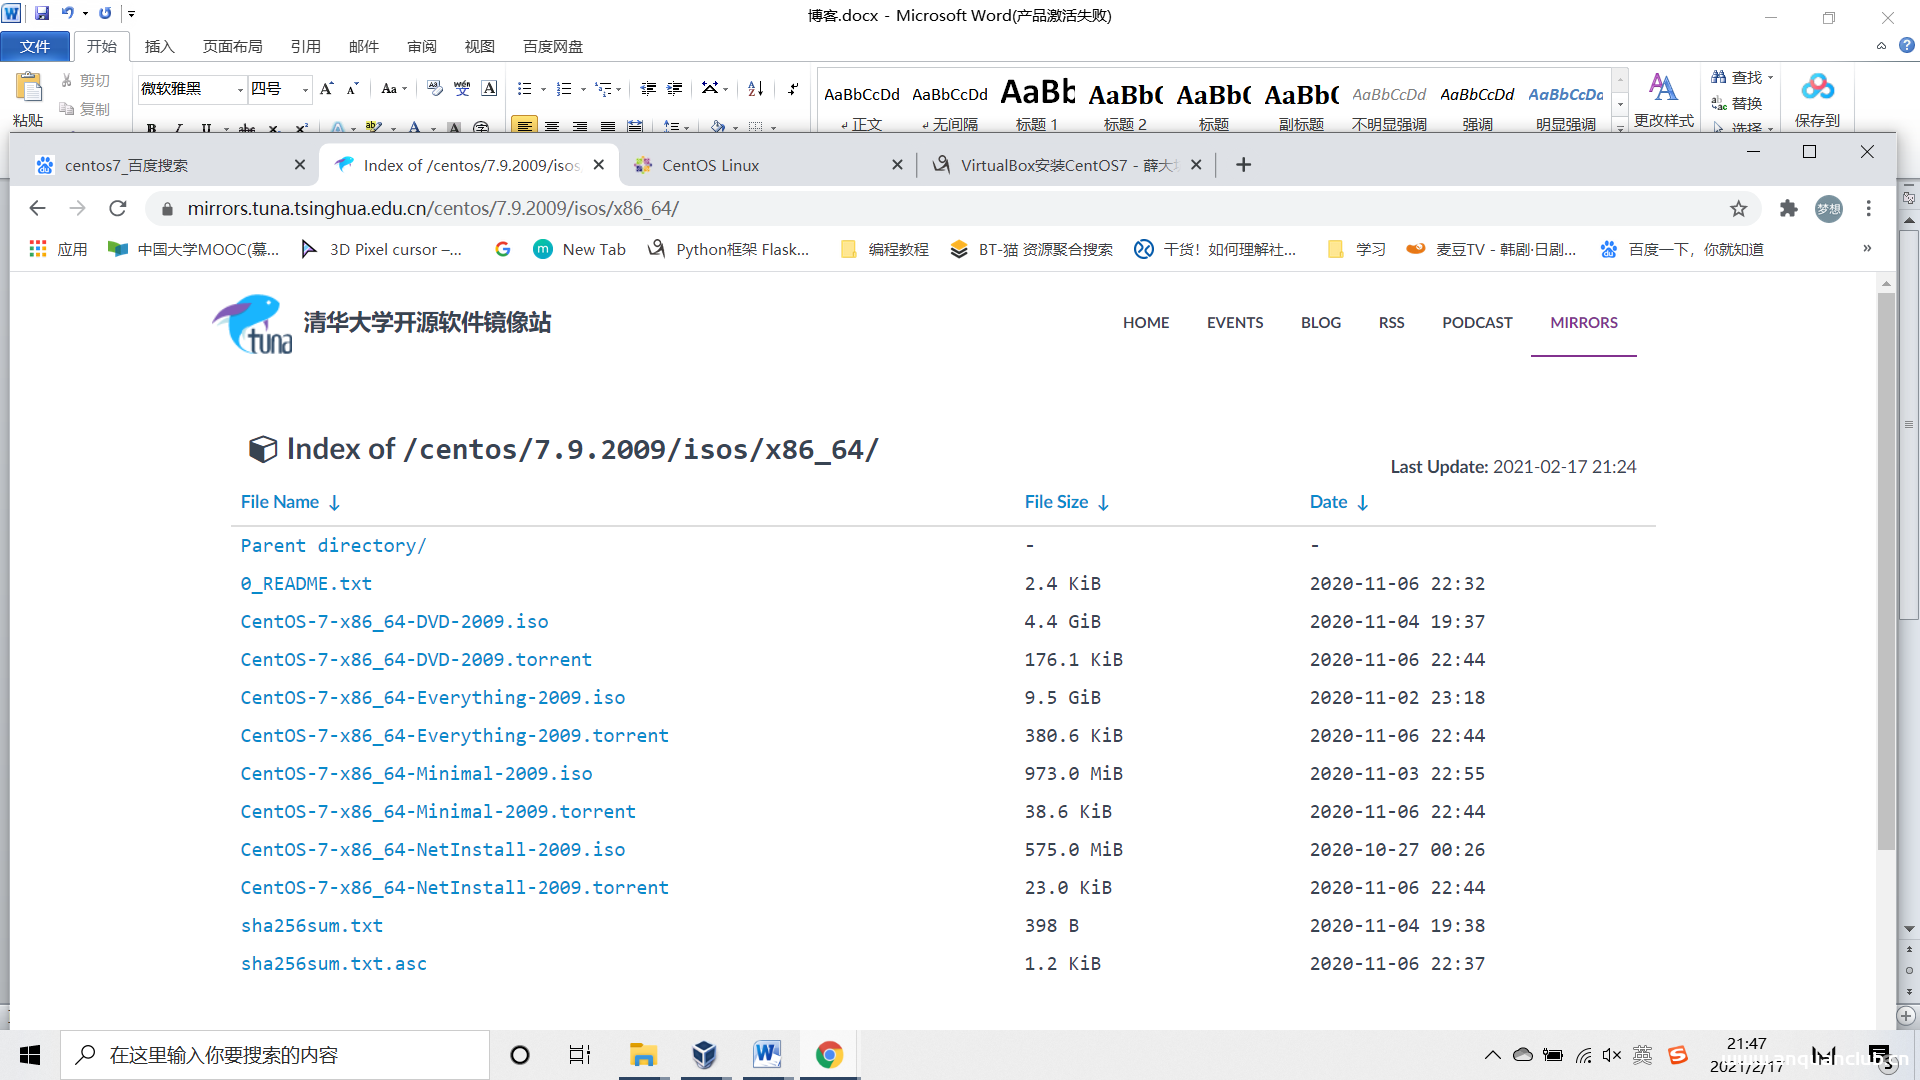
Virtualbox 安装centos7虚拟机的图文教程详解_VirtualBox
这篇文章主要介绍了Virtualbox 安装centos7虚拟机,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一,下载centos7 下载地址:http://mirrors.tun...
CVE-2021-42670: Engineers Online Portal 1.0 容易受到三种类型的SQL注入攻击
漏洞标题 CVE-2021-42670: Engineers Online Portal 1.0 容易受到三种类型的SQL注入攻击 漏洞描述 Engineers Online Portal 1.0 应用程序中的 id 参数my_classmates.php似乎容易受到三种类型的 ...
CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
CVE-2023-32315-2: Openfire身份认证绕过漏洞
漏洞标题 CVE-2023-32315-2: Openfire身份认证绕过漏洞 漏洞描述 Openfire is an XMPP server licensed under the Open Source Apache License. Openfire's administrative console, a web...
CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
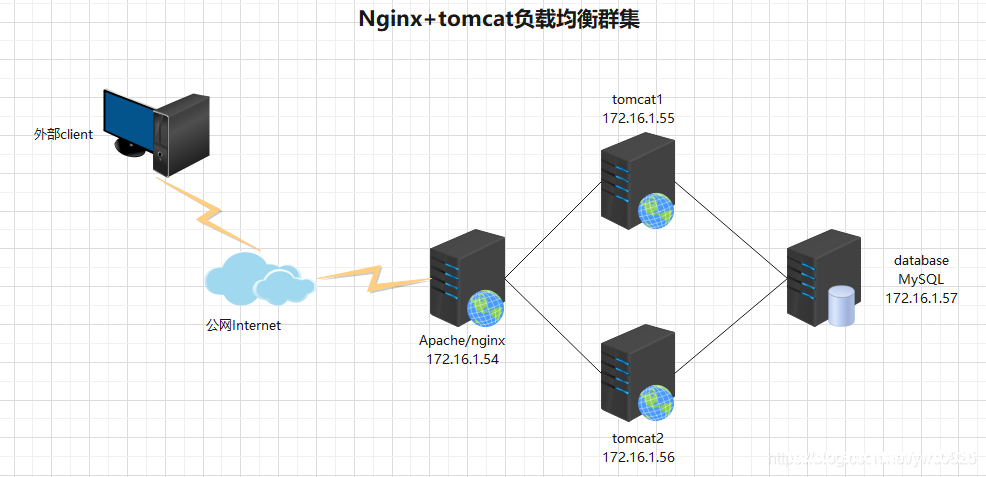
Nginx+tomcat负载均衡集群的实现方法_nginx
这篇文章主要介绍了Nginx+tomcat负载均衡集群,的实现方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 实验环境如下 这里需要准备4台服务器(...
Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195)
漏洞标题 Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195) 漏洞描述 Apache OFBiz是一个开源企业资源规划(ERP)系统。它提供了一套企业应用程序,集成并自动化企业的许多业务流程...
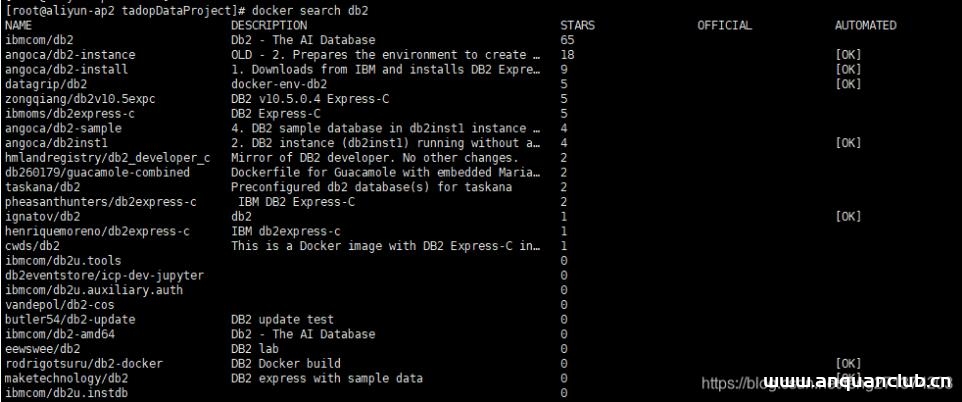
docker-compose安装db2数据库操作_docker
这篇文章主要介绍了docker-compose安装db2数据库操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 db2数据库在宿主机直接安装比较麻烦,而且涉及用户和权限也不方便,所...
CVE-2025-6403: Code-Projects School Fees Payment System 1.0 – SQL Injection
漏洞标题 CVE-2025-6403: Code-Projects School Fees Payment System 1.0 - SQL Injection 漏洞描述 A vulnerability was found in code-projects School Fees Payment System 1.0. It has been...

