





CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
CirCarLifeScada停车场自动化管理系统values.xml-信息泄漏(CVE-2018-16670)
漏洞标题 CirCarLifeScada停车场自动化管理系统values.xml-信息泄漏(CVE-2018-16670) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
CVE-2023-1835: Ninja Forms < 3.6.22 - Cross-Site Scripting
漏洞标题 CVE-2023-1835: Ninja Forms < 3.6.22 - Cross-Site Scripting 漏洞描述 Ninja Forms before 3.6.22 is susceptible to cross-site scripting via the page parameter due to insuf...
CVE-2023-23752: Joomla! Webservice – Password Disclosure
漏洞标题 CVE-2023-23752: Joomla! Webservice - Password Disclosure 漏洞描述 An issue was discovered in Joomla! 4.0.0 through 4.2.7. An improper access check allows unauthorized acce...
CVE-2024-8859: Mlflow < 2.17.0 - Local File Inclusion
漏洞标题 CVE-2024-8859: Mlflow < 2.17.0 - Local File Inclusion 漏洞描述 Mlflow before 2.17.0 is susceptible to local file inclusion due to path traversal in GitHub repository ml...
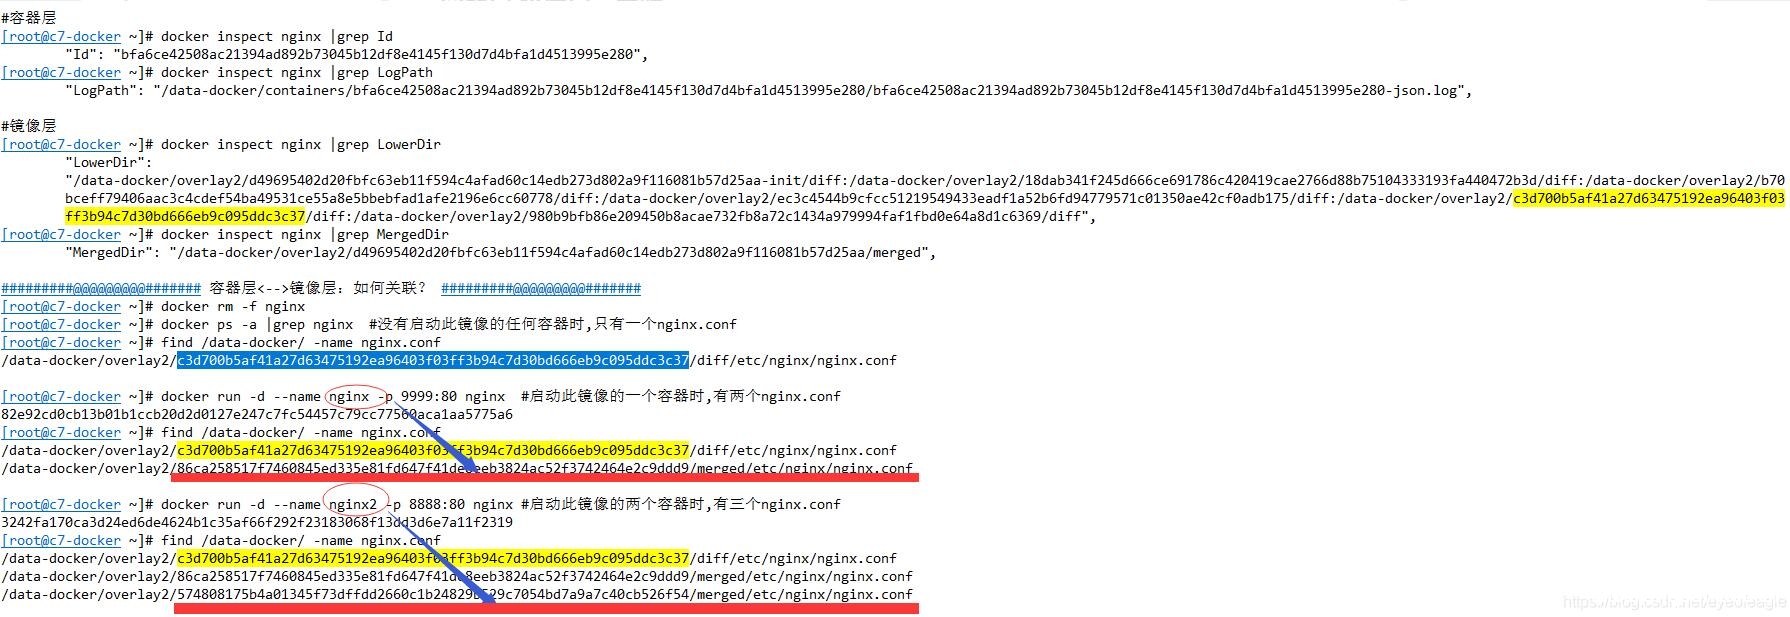
docker 文件存放路径, 修改端口映射操作方式_docker
这篇文章主要介绍了docker 文件存放路径, 修改端口映射操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 如何获取容器的启动命令 容器早已创建好,如何得知它的启动参数(...

Nginx的rewrite模块详解_nginx
这篇文章主要介绍了Nginx的rewrite模块详解,有感兴趣的同学可以研究下 rewrite模块即ngx_http_rewrite_module模块,主要功能是改写请求URI,是Nginx默认安装的模块。rewrite模块会根据PCRE正则...
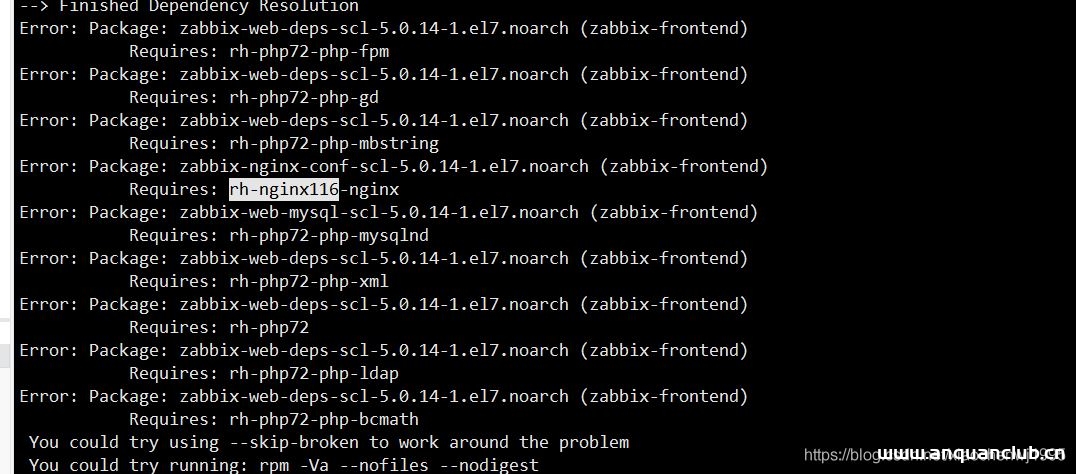
centos7.9安装zabbix5.0.14及配置过程_zabbix
这篇文章主要介绍了centos7.9安装zabbix5.0.14的详细过程,本文给大家介绍了基础环境配置方法及安装zabbix相关组件的过程讲解,需要的朋友可以参考下 目录一、基础环境配置二、安装数据库三、安...
CVE-2022-41040: Microsoft Exchange SSRF
漏洞标题 CVE-2022-41040: Microsoft Exchange SSRF 漏洞描述 r0 是 nmap 脚本 r1 是 github 未经验证得 PoC fofa: app="Microsoft-Exchange" PoC代码
CVE-2018-17207: WordPress Duplicator Plugin < 1.2.42 - Arbitrary Code Execution
漏洞标题 CVE-2018-17207: WordPress Duplicator Plugin < 1.2.42 - Arbitrary Code Execution 漏洞描述 An issue was discovered in Snap Creek Duplicator before 1.2.42. By accessing le...
CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530)
漏洞标题 Apache Struts2(S2-061)远程代码执行漏洞(CVE-2020-17530) 漏洞描述 Apache Struts2框架是一个用于开发Java EE网络应用程序的Web框架。Struts2 会对某些标签属性(比如 id,其他属性有...
CVE-2025-49001: Dataease JWT 认证绕过漏洞
漏洞标题 CVE-2025-49001: Dataease JWT 认证绕过漏洞 漏洞描述 CVE-2025-49001 是由于JWT校验机制错误导致攻击者可伪造JWT令牌绕过身份验证流程 fofa: body="/js/index-0.0.0-dataease.js...
CVE-2025-30208: Vite – Arbitrary File Read
漏洞标题 CVE-2025-30208: Vite - Arbitrary File Read 漏洞描述 Vite, a provider of frontend development tooling, has a vulnerability in versions prior to 6.2.3, 6.1.2, 6.0.12, 5.4.15...
CVE-2025-41393: Ricoh Web Image Monitor – Reflected XSS
漏洞标题 CVE-2025-41393: Ricoh Web Image Monitor - Reflected XSS 漏洞描述 A reflected cross-site scripting vulnerability exists in the laser printers and MFPs (multifunction printe...
CVE-2020-11455: LimeSurvey 4.1.11 – Local File Inclusion
漏洞标题 CVE-2020-11455: LimeSurvey 4.1.11 - Local File Inclusion 漏洞描述 LimeSurvey before 4.1.12+200324 is vulnerable to local file inclusion because it contains a path traversa...

