




解决docker 容器设置中文语言包出现的问题_docker
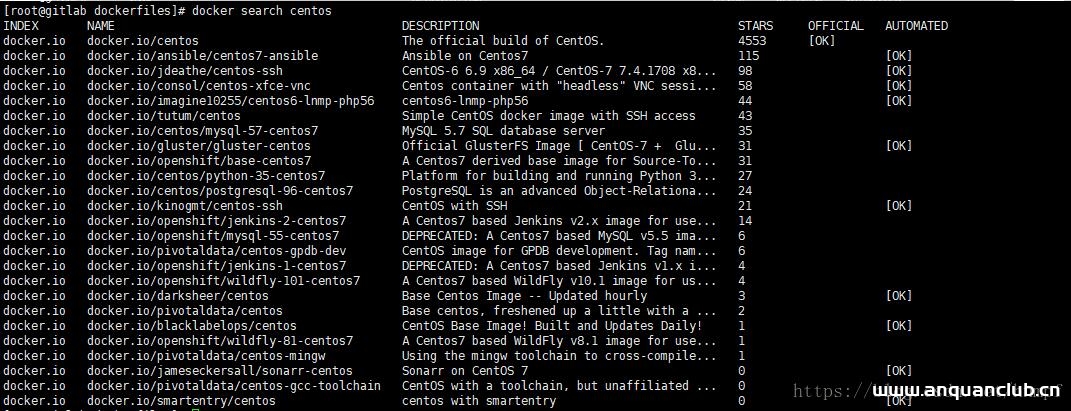
这篇文章主要介绍了解决docker 容器设置中文语言包出现的问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 如果在Docker 中采用 docker search centos 采用 docker pull ...
Docker 拉取镜像及标签操作 pull | tag_docker
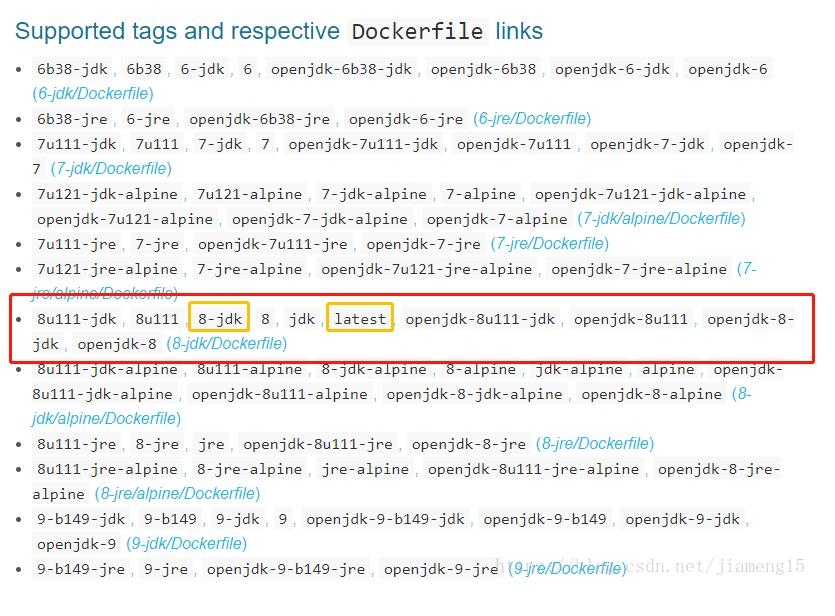
这篇文章主要介绍了Docker 拉取镜像及标签操作 pull | tag,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 重翻Fabric项目的源码,发现Docker部分内容,有很多不尽理解的地...
linux系统文件共享samba配置教程_Linux
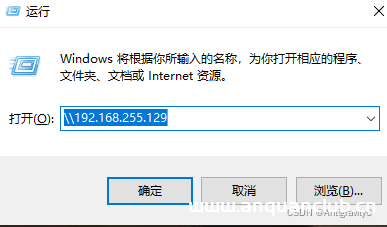
目录卸载及安装 samba新建共享路径及权限设置编辑samba 配置文件重启samba服务windows 打开共享文件夹卸载及安装 samba sudo apt-get purge samba samba-* sudo apt-get update sudo apt-get in...
docker windows10 共享目录挂载失败的解决方案_docker
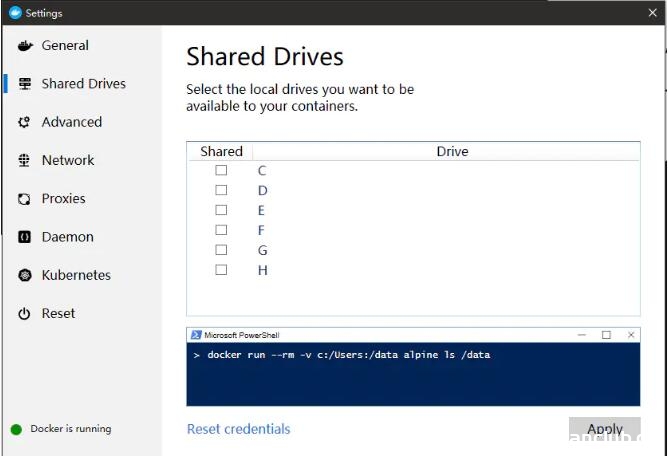
这篇文章主要介绍了docker windows10 共享目录挂载失败的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 起因 在执行docker脚本的时候,出现不能创建容器的错误。 ...

Docker和镜像的操作方法_docker
这篇文章主要介绍了Docker和镜像的操作方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 查找镜像 我们可以从 Docker Hub 网站来搜索镜像,Doc...

CVE-2024-30188: Apache DolphinScheduler >= 3.1.0, < 3.2.2 Resource File Read And Write
漏洞标题 CVE-2024-30188: Apache DolphinScheduler >= 3.1.0, < 3.2.2 Resource File Read And Write 漏洞描述 File read and write vulnerability in Apache DolphinScheduler, authent...
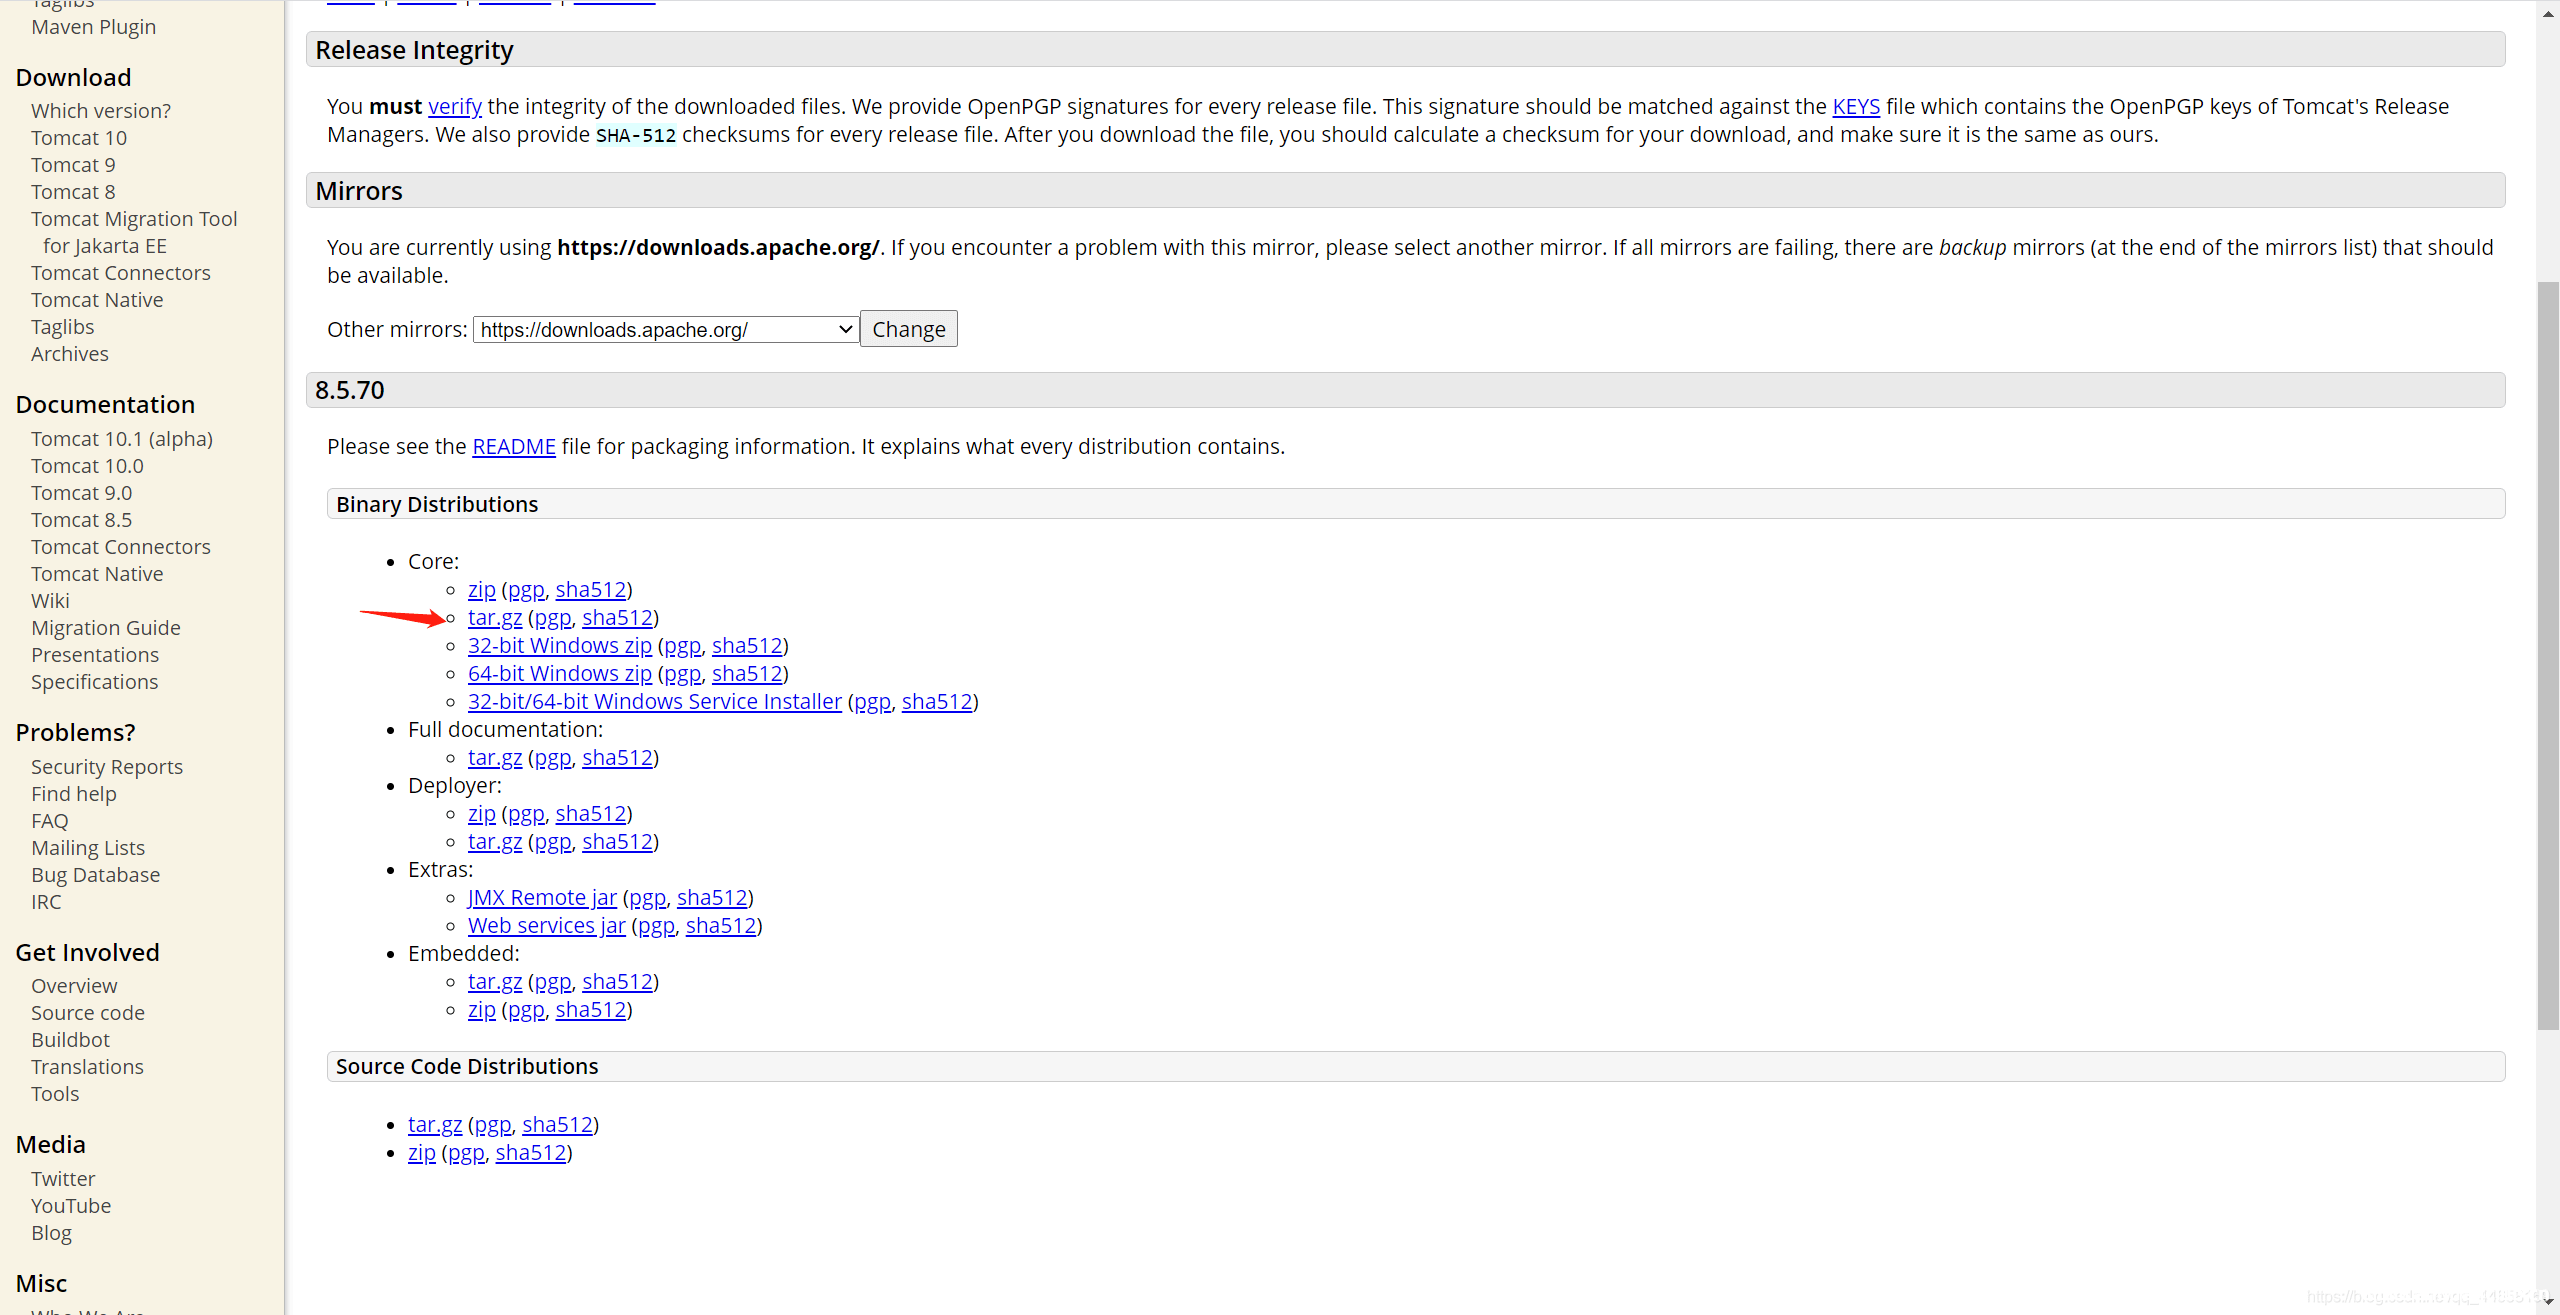
最新Linux下安装tomcat8图解过程_Linux
这篇文章主要介绍了最新的Linux下安装tomcat8图解过程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 下载地址 http://tomcat.apache.org/downl...
CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection
漏洞标题 CVE-2022-0867: WordPress ARPrice <3.6.1 - SQL Injection 漏洞描述 WordPress ARPrice plugin prior to 3.6.1 contains a SQL injection vulnerability. It fails to properly sa...
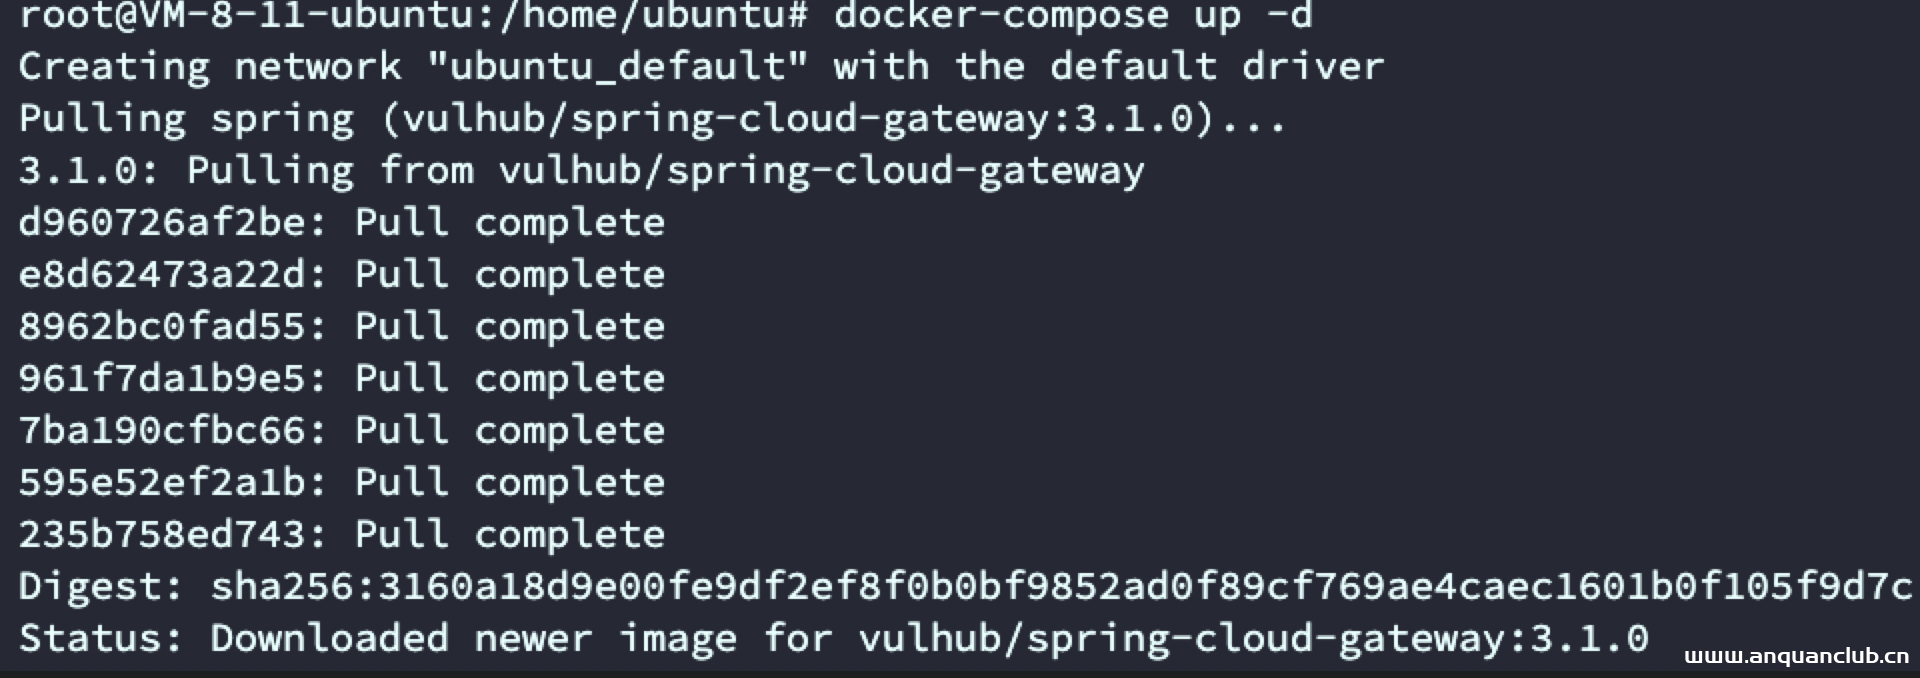
Spring_Cloud_Gateway_Actuator_API_SpEL表达式注入命令执行(CVE-2022-22947)
虽然现在发有点像炒冷饭?不过前几天太忙了 没时间看 既然复现了就记录一下吧 一、环境搭建 http://github.com/vulhub/vulhub/tree/master/spring/CVE-2022-22947 docker-compose up -d 二、漏...
CVE-2023-40931: Nagios XI v5.11.0 – SQL Injection
漏洞标题 CVE-2023-40931: Nagios XI v5.11.0 - SQL Injection 漏洞描述 A SQL injection vulnerability in Nagios XI from version 5.11.0 up to and including 5.11.1 allows authenticated a...
业界首个!腾讯云原生一站式微服务管理框架Femas开源
3月16日,腾讯云宣布正式开源业界首个云原生标准的一站式微服务管理框架—— Femas 。作为腾讯云微服务平台 TSF 的开源版本,Femas将在云原生组件“北极星”(PolarisMesh)子项目下对外开源,...
CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2025-1661: HUSKY – Products Filter Professional for WooCommerce <= 1.3.6.5 - Unauthenticated Local File Inclusion 漏洞描述 The HUSKY – Products Filter Professiona...
CVE-2023-25573: Metersphere – Arbitrary File Read
漏洞标题 CVE-2023-25573: Metersphere - Arbitrary File Read 漏洞描述 Metersphere is an open source continuous testing platform. In affected versions an improper access control vulne...
CVE-2025-4427: Ivanti Endpoint Manager Mobile – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-4427: Ivanti Endpoint Manager Mobile - Unauthenticated Remote Code Execution 漏洞描述 An authentication bypass in Ivanti Endpoint Manager Mobile allowing attacker...
CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape
漏洞标题 CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow...

