





如何使用Docker部署Go Web应用的实现_docker
这篇文章主要介绍了如何使用Docker部署Go Web应用的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 目录为什...
docker下的 redis 之持久化存储详解_docker
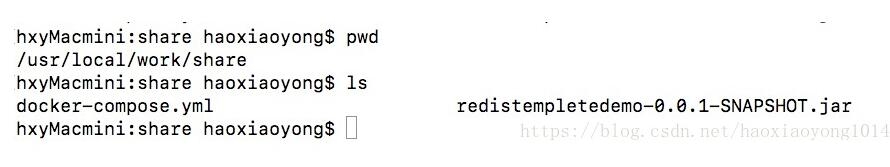
这篇文章主要介绍了docker下的 redis 之持久化存储详解,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 本章节开始 我们在docker下 进行 spring Boot项目操作redis 准备工作...

CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
CVE-2021-40444-Microsoft MSHTML远程命令执行
2021年9月8日,微软官方发布了MSHTML组件的风险通告(漏洞编号:CVE-2021-40444),未经身份验证的攻击者可以利用该漏洞在目标系统上远程执行代码。微软官方表示已经监测到该漏洞存在在野利用。...
CVE-2023-38040: Revive Adserver 5.4.1 – Cross-Site Scripting
漏洞标题 CVE-2023-38040: Revive Adserver 5.4.1 - Cross-Site Scripting 漏洞描述 A reflected XSS vulnerability exists in Revive Adserver 5.4.1 and earlier versions. PoC代码

详解docker部署SpringBoot及替换jar包的方法_docker
这篇文章主要介绍了详解docker部署SpringBoot及替换jar包的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录工程目录Dockerfile文件文件...
Arcserve Unified Data Protection CVE-2024-0801 拒绝服务漏洞
漏洞标题 Arcserve Unified Data Protection CVE-2024-0801 拒绝服务漏洞 漏洞描述 Arcserve Unified Data Protection存在拒绝服务漏洞,此漏洞是由于EdgeServiceConsoleImpl接口对用户的请求验...
CVE-2015-4414: WordPress SE HTML5 Album Audio Player 1.1.0 – Directory Traversal
漏洞标题 CVE-2015-4414: WordPress SE HTML5 Album Audio Player 1.1.0 - Directory Traversal 漏洞描述 WordPress SE HTML5 Album Audio Player 1.1.0 contains a directory traversal vulner...
CVE-2023-43662: ShokoServer System – Local File Inclusion (LFI)
漏洞标题 CVE-2023-43662: ShokoServer System - Local File Inclusion (LFI) 漏洞描述 ShokoServer is a media server which specializes in organizing anime. In affected versions the `/ap...
docker pull拉取超时的解决方案_docker
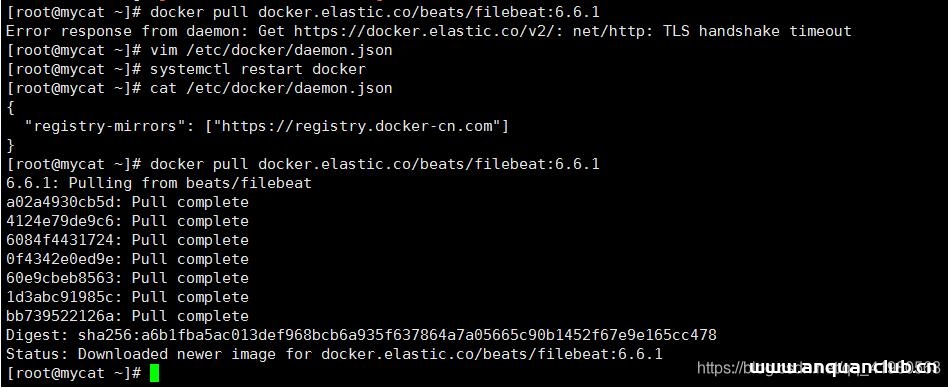
这篇文章主要介绍了docker pull拉取超时的解决方案,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 最近docker pull镜像的时候非常不稳定,速度慢不说还经常超时失败 Pullin...
CVE-2021-22175: GitLab CI Lint API – Server-Side Request Forgery
漏洞标题 CVE-2021-22175: GitLab CI Lint API - Server-Side Request Forgery 漏洞描述 GitLab 10.5 and later contain a server-side request forgery caused by insecure handling of webhoo...
CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion
漏洞标题 CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion 漏洞描述 phpMyAdmin before 4.8.5 is susceptible to local file inclusion. When the AllowArbitraryServer configura...
CVE-2019-19824: TOTOLINK Realtek SD Routers – Remote Command Injection
漏洞标题 CVE-2019-19824: TOTOLINK Realtek SD Routers - Remote Command Injection 漏洞描述 TOTOLINK Realtek SDK based routers may allow an authenticated attacker to execute arbitrary...
CVE-2019-14750: osTicket < 1.12.1 - Cross-Site Scripting
漏洞标题 CVE-2019-14750: osTicket < 1.12.1 - Cross-Site Scripting 漏洞描述 An issue was discovered in osTicket before 1.10.7 and 1.12.x before 1.12.1. Stored XSS exists in setup...
CVE-2023-3077: MStore API < 3.9.8 - SQL Injection
漏洞标题 CVE-2023-3077: MStore API < 3.9.8 - SQL Injection 漏洞描述 The MStore API WordPress plugin before 3.9.8 is vulnerable to Blind SQL injection via the product_id paramete...
CVE-2024-21887: Ivanti Connect Secure (9.x, 22.x) and Ivanti Policy Secure (9.x, 22.x) – Command Injection
漏洞标题 CVE-2024-21887: Ivanti Connect Secure (9.x, 22.x) and Ivanti Policy Secure (9.x, 22.x) - Command Injection 漏洞描述 A command injection vulnerability in web components of ...

