




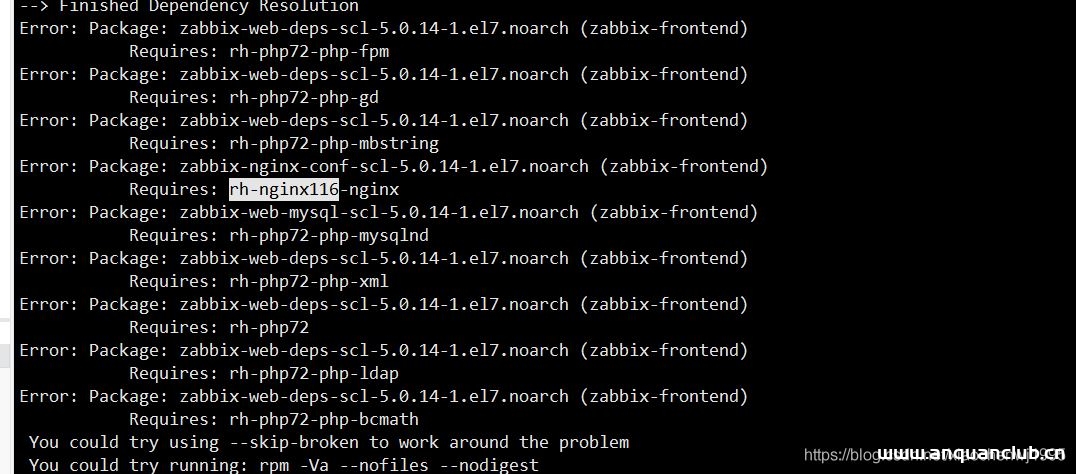
centos7.9安装zabbix5.0.14及配置过程_zabbix
这篇文章主要介绍了centos7.9安装zabbix5.0.14的详细过程,本文给大家介绍了基础环境配置方法及安装zabbix相关组件的过程讲解,需要的朋友可以参考下 目录一、基础环境配置二、安装数据库三、安...

CVE-2025-44177: White Star Software ProTop – Directory Traversal
漏洞标题 CVE-2025-44177: White Star Software ProTop - Directory Traversal 漏洞描述 A directory traversal vulnerability was discovered in White Star Software Protop version 4.4.2-20...
还在让浏览器保存密码?小心遭恶意软件窃取
12月28日,韩国最大杀毒软件公司安博士Ahnlab发布了一份研究报告,警告有一款名为RedLine Stealer的恶意软件正在窃取Web浏览器存储的密码。 Ahnlab是韩国首家从事开发杀毒软件的企业,于19...
CVE-2023-4169: Ruijie RG-EW1200G Router – Password Reset
漏洞标题 CVE-2023-4169: Ruijie RG-EW1200G Router - Password Reset 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 1.0(1)B1P5. It has been declared as critical. Affected by ...
CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection
漏洞标题 CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection 漏洞描述 Improper Neutralization of Special Elements used in an SQL Command ('SQL Injecti...
CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape
漏洞标题 CVE-2025-46818: Redis Lua Sandbox < 8.2.2 - Cross-User Escape 漏洞描述 Redis is an open source, in-memory database that persists on disk. Versions 8.2.1 and below allow...
CVE-2018-3167: Oracle E-Business Suite – Blind SSRF
漏洞标题 CVE-2018-3167: Oracle E-Business Suite - Blind SSRF 漏洞描述 Oracle E-Business Suite, Application Management Pack component (User Monitoring subcomponent), is susceptible ...
CVE-2023-28432: MinIO Cluster Deployment – Information Disclosure
漏洞标题 CVE-2023-28432: MinIO Cluster Deployment - Information Disclosure 漏洞描述 MinIO is susceptible to information disclosure. In a cluster deployment starting with RELEASE.20...
(CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞
漏洞标题 (CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞 漏洞描述 (CVE-2025-5961) WPvivid备份与迁移插件任意文件上传漏洞 PoC代码 暂无
CVE-2015-9406: mTheme Unus < 2.3 - Directory Traversal
漏洞标题 CVE-2015-9406: mTheme Unus < 2.3 - Directory Traversal 漏洞描述 The mTheme-Unus theme for WordPress, prior to version 2.3, contained a directory traversal flaw that let...
CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 – Remote Code Execution
漏洞标题 CVE-2022-48323: Sunflower Simple and Personal 1.0.1.43315 - Remote Code Execution 漏洞描述 Sunlogin Sunflower Simplified (aka Sunflower Simple and Personal) 1.0.1.43315 is...
CVE-2020-11034: GLPI <9.4.6 - Open Redirect
漏洞标题 CVE-2020-11034: GLPI <9.4.6 - Open Redirect 漏洞描述 GLPI prior 9.4.6 contains an open redirect vulnerability based on a regexp. PoC代码
CVE-2022-3477: WordPress tagDiv Composer < 3.5 - Authentication Bypass
漏洞标题 CVE-2022-3477: WordPress tagDiv Composer < 3.5 - Authentication Bypass 漏洞描述 The tagDiv Composer WordPress plugin before 3.5, required by the Newspaper WordPress the...
CVE-2022-2174: microweber 1.2.18 – Cross-site Scripting
漏洞标题 CVE-2022-2174: microweber 1.2.18 - Cross-site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository microweber/microweber prior to 1.2.18. PoC代码

