




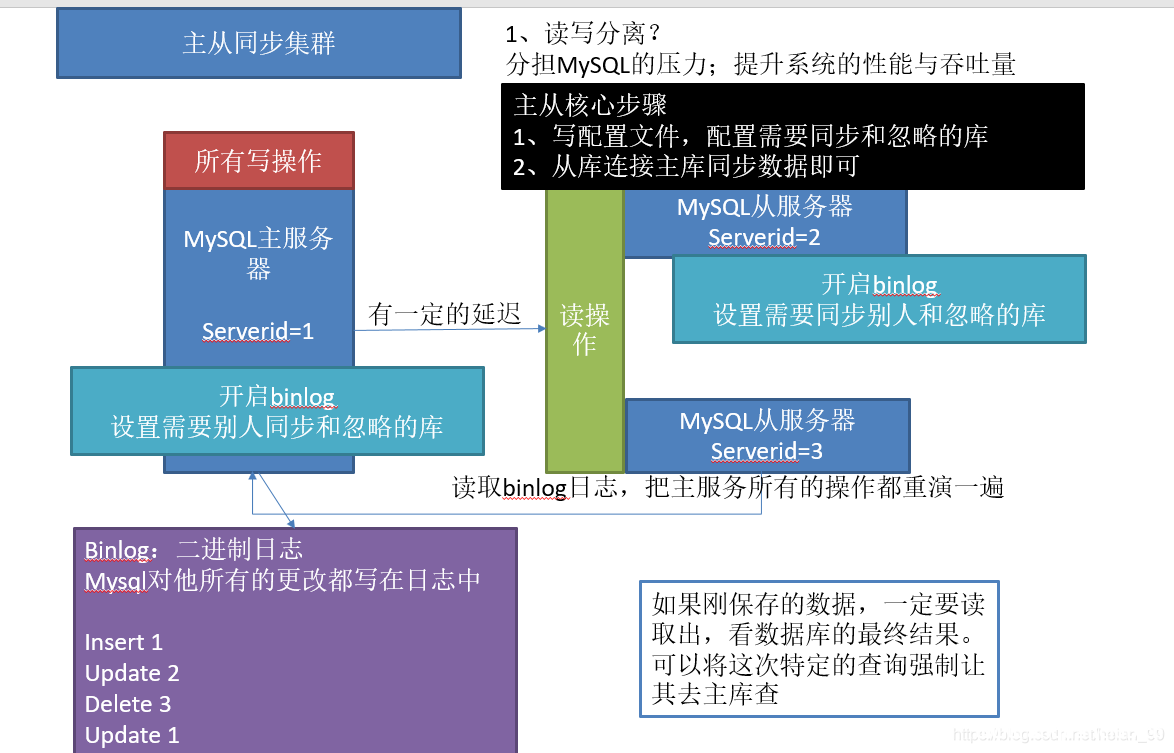
docker实现mysql主从复制的示例代码_docker
Docker它不香吗?即省去了安装Mysql所需要的步骤,有多个容器之间相互资源独立,IP互不冲突,具有一定的参考价值,感兴趣的可以了解一下 目录一、概述1、原理2、实现三、创建Slave实例四、主从配...

CVE-2023-43662: ShokoServer System – Local File Inclusion (LFI)
漏洞标题 CVE-2023-43662: ShokoServer System - Local File Inclusion (LFI) 漏洞描述 ShokoServer is a media server which specializes in organizing anime. In affected versions the `/ap...
CVE-2022-38295: Cuppa CMS v1.0 – Cross Site Scripting
漏洞标题 CVE-2022-38295: Cuppa CMS v1.0 - Cross Site Scripting 漏洞描述 Cuppa CMS v1.0 was discovered to contain a cross-site scripting vulnerability at /table_manager/view/cu_user...

Mac M1 Nginx 配置多站点的实现_nginx
这篇文章主要介绍了Mac M1 Nginx 配置多站点的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 说明: 通...
CVE-2023-27641: L-Soft LISTSERV 16.5 – Cross-Site Scripting
漏洞标题 CVE-2023-27641: L-Soft LISTSERV 16.5 - Cross-Site Scripting 漏洞描述 The REPORT (after z but before a) parameter in wa.exe in L-Soft LISTSERV 16.5 before 17 allows an atta...
CVE-2021-22175: GitLab CI Lint API – Server-Side Request Forgery
漏洞标题 CVE-2021-22175: GitLab CI Lint API - Server-Side Request Forgery 漏洞描述 GitLab 10.5 and later contain a server-side request forgery caused by insecure handling of webhoo...
CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion
漏洞标题 CVE-2019-6799: phpMyAdmin <4.8.5 - Local File Inclusion 漏洞描述 phpMyAdmin before 4.8.5 is susceptible to local file inclusion. When the AllowArbitraryServer configura...
CVE-2019-14750: osTicket < 1.12.1 - Cross-Site Scripting
漏洞标题 CVE-2019-14750: osTicket < 1.12.1 - Cross-Site Scripting 漏洞描述 An issue was discovered in osTicket before 1.10.7 and 1.12.x before 1.12.1. Stored XSS exists in setup...
CVE-2023-3077: MStore API < 3.9.8 - SQL Injection
漏洞标题 CVE-2023-3077: MStore API < 3.9.8 - SQL Injection 漏洞描述 The MStore API WordPress plugin before 3.9.8 is vulnerable to Blind SQL injection via the product_id paramete...
CVE-2023-34752: bloofoxCMS v0.5.2.1 – SQL Injection
漏洞标题 CVE-2023-34752: bloofoxCMS v0.5.2.1 - SQL Injection 漏洞描述 bloofox v0.5.2.1 was discovered to contain a SQL injection vulnerability via the lid parameter at admin/index....
Adobe ColdFusion /filemanager/iedit.cfc 未授权访问漏洞 (CVE-2023-26360)
漏洞标题 Adobe ColdFusion /filemanager/iedit.cfc 未授权访问漏洞 (CVE-2023-26360) 漏洞描述 Adobe ColdFusion是一种用于构建动态Web应用程序的服务器端编程语言和开发平台。ColdFusion的...
CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion
漏洞标题 CVE-2020-35749: WordPress Simple Job Board <2.9.4 - Local File Inclusion 漏洞描述 WordPress Simple Job Board prior to version 2.9.4 is vulnerable to arbitrary file retr...
CVE-2024-10783: WordPress Plugin MainWP Child – Authentication Bypass
漏洞标题 CVE-2024-10783: WordPress Plugin MainWP Child - Authentication Bypass 漏洞描述 The plugin is vulnerable to an authentication bypass that allows an unauthenticated user to ...
CVE-2022-47003: Mura CMS <10.0.580 - Authentication Bypass
漏洞标题 CVE-2022-47003: Mura CMS <10.0.580 - Authentication Bypass 漏洞描述 Mura CMS before 10.0.580 is susceptible to authentication bypass in the Remember Me function. An att...
supervisor下的Dockerfile的多服务镜像封装操作_docker
这篇文章主要介绍了supervisor下的Dockerfile的多服务镜像封装操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 编写Dockerfile文件 配置yum源 cd /tmp/docker vim Docke...

