





CVE-2018-19458: PHP Proxy 3.0.3 – Local File Inclusion
漏洞标题 CVE-2018-19458: PHP Proxy 3.0.3 - Local File Inclusion 漏洞描述 PHP Proxy 3.0.3 is susceptible to local file inclusion vulnerabilities that allow unauthenticated users to ...
CVE-2021-24838: WordPress AnyComment <0.3.5 - Open Redirect
漏洞标题 CVE-2021-24838: WordPress AnyComment <0.3.5 - Open Redirect 漏洞描述 WordPress AnyComment plugin before 0.3.5 contains an open redirect vulnerability via an API endpoin...
CVE-2006-2173: FileZilla FTP Server 2.2.22 – Buffer Overflow
漏洞标题 CVE-2006-2173: FileZilla FTP Server 2.2.22 - Buffer Overflow 漏洞描述 FileZilla FTP Server version 2.2.22 contains a buffer overflow vulnerability that allows remote authe...
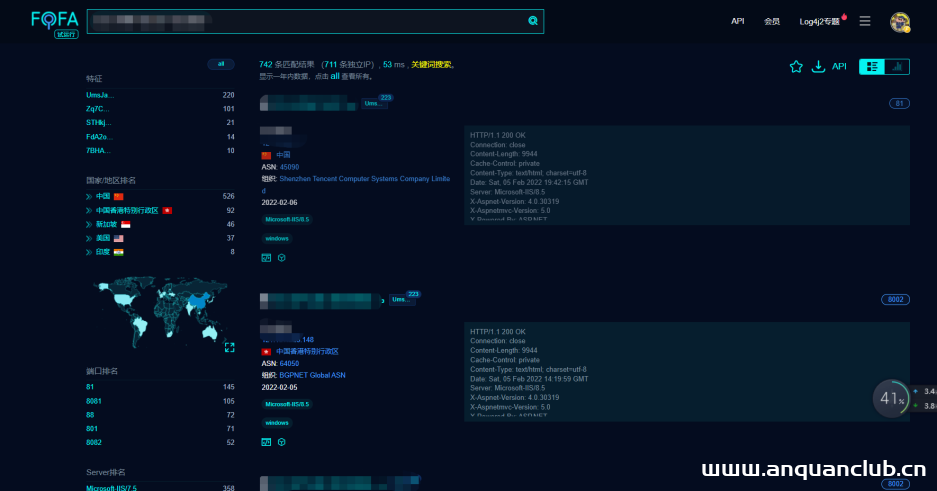
某棋牌渗透测试
前言 由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,文章作者不为此承担任何责任。 一、信息收集 这里通过fofa进行收集,语法为:body=某棋牌 &am...
CVE-2020-20601: ThinkCMF X2.2.2 – Remote Code Execution
漏洞标题 CVE-2020-20601: ThinkCMF X2.2.2 - Remote Code Execution 漏洞描述 ThinkCMF X2.2.2 and below contain a remote code execution caused by processing crafted packets, letting at...
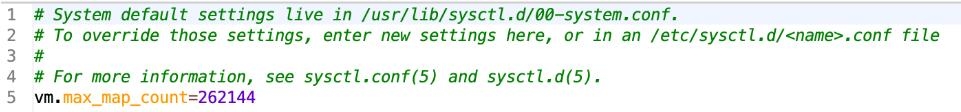
docker镜像访问本地elasticsearch端口操作_docker
这篇文章主要介绍了docker镜像访问本地elasticsearch端口操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 使用docker stack部署的镜像服务,进入镜像之后,理论上,应该...

bugbounty技巧聚合20220106
漏洞报告 【8x8】XSS漏洞 http://hackerone.com/reports/1440161 【Mattermost 】 能够诱使受害者在特定会话中使用伪造的电子邮件地址,然后取回帐户 http://hackerone.com/reports/1357013 【T...
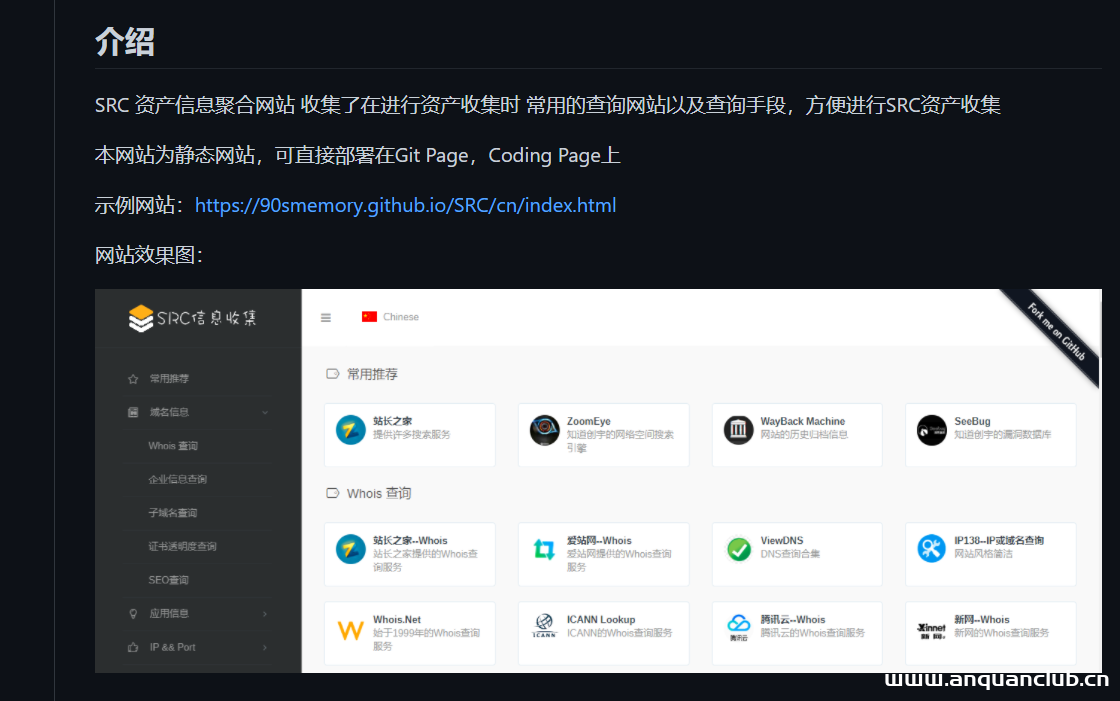
本地自用信息收集网站(源码)
git clone http://github.com/90smemory/SRC.git 文字来源于- 火线 Zone-云安全社区,安全小天地只做文章分享,如有侵权,请联系站长删除
CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
CVE-2024-2879: WordPress Plugin LayerSlider 7.9.11-7.10.0 – SQL Injection
漏洞标题 CVE-2024-2879: WordPress Plugin LayerSlider 7.9.11-7.10.0 - SQL Injection 漏洞描述 The LayerSlider plugin for WordPress is vulnerable to SQL Injection via the ls_get_popup...
Spring Boot使用Docker分层打包的设置方法_docker
Spring Boot 现在支持分层打包技术了, 我们也来用一用, 加速Docker打包, 构建的时候速度也会非常快.本文重点给大家介绍Spring Boot使用Docker分层打包的设置方法,感兴趣的朋友一起看看吧 Sprin...
CVE-2025-24963: Vitest Browser Mode – Local File Read
漏洞标题 CVE-2025-24963: Vitest Browser Mode - Local File Read 漏洞描述 Vitest is a testing framework powered by Vite. The `__screenshot-error` handler on the browser mode HTTP ser...
CVE-2025-1097: Ingress-Nginx Controller – Configuration Injection via Unsanitized `auth-tls-match-cn` Annotation
漏洞标题 CVE-2025-1097: Ingress-Nginx Controller - Configuration Injection via Unsanitized `auth-tls-match-cn` Annotation 漏洞描述 A security issue was discovered in ingress-nginx ...
CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF)
漏洞标题 CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF) 漏洞描述 imgproxy <=3.14.0 is vulnerable to Server-Side Request Forgery (SSRF) due to a lack ...
CVE-2025-9985: Featured Image from URL (FIFU) <= 5.2.7 - Unauthenticated Information Exposure via Log File
漏洞标题 CVE-2025-9985: Featured Image from URL (FIFU) <= 5.2.7 - Unauthenticated Information Exposure via Log File 漏洞描述 The Featured Image from URL (FIFU) plugin for WordPr...
Nginx+ModSecurity安全模块部署的实现_nginx
本文主要介绍了Nginx+ModSecurity安全模块部署的实现,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录一、下载二、部署1.Nginx部署2.ModSecurity部署...

