





CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
CVE-2023-4284: WordPress Post Timeline Plugin < 2.2.6 - Cross-Site Scripting
漏洞标题 CVE-2023-4284: WordPress Post Timeline Plugin < 2.2.6 - Cross-Site Scripting 漏洞描述 The Post Timeline WordPress plugin before version 2.2.6 contains a reflected cross...
CVE-2022-3142: NEX-Forms Plugin < 7.9.7 - SQL Injection
漏洞标题 CVE-2022-3142: NEX-Forms Plugin < 7.9.7 - SQL Injection 漏洞描述 The NEX-Forms WordPress plugin before 7.9.7 does not properly sanitise and escape user input before usi...
CVE-2015-6920: WordPress sourceAFRICA <=0.1.3 - Cross-Site Scripting
漏洞标题 CVE-2015-6920: WordPress sourceAFRICA <=0.1.3 - Cross-Site Scripting 漏洞描述 WordPress sourceAFRICA plugin version 0.1.3 contains a cross-site scripting vulnerability....
CVE-2025-4302: Stop User Enumeration WordPress plugin – Authentication Bypass
漏洞标题 CVE-2025-4302: Stop User Enumeration WordPress plugin - Authentication Bypass 漏洞描述 Stop User Enumeration WordPress plugin < 1.7.3 contains an authentication bypass ...
CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution
漏洞标题 CVE-2025-48703: CWP (Control Web Panel) < 0.9.8.1205 - Remote Code Execution 漏洞描述 CWP (Control Web Panel) < 0.9.8.1205 contains a remote code execution caused by...
CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting
漏洞标题 CVE-2021-25065: Smash Balloon Social Post Feed < 4.1.1 - Authenticated Reflected Cross-Site Scripting 漏洞描述 The plugin was affected by a reflected XSS in custom-face...
CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
CVE-2016-4977: Spring Security OAuth2 Remote Command Execution
漏洞标题 CVE-2016-4977: Spring Security OAuth2 Remote Command Execution 漏洞描述 Spring Security OAuth versions 2.0.0 to 2.0.9 and 1.0.0 to 1.0.5 contain a remote command execution...
CVE-2021-40149: Reolink E1 Zoom Camera <=3.0.0.716 - Private Key Disclosure
漏洞标题 CVE-2021-40149: Reolink E1 Zoom Camera <=3.0.0.716 - Private Key Disclosure 漏洞描述 Reolink E1 Zoom Camera versions 3.0.0.716 and below suffer from a private key (RSA)...
CVE-2020-27735: Wing FTP 6.4.4 – Cross-Site Scripting
漏洞标题 CVE-2020-27735: Wing FTP 6.4.4 - Cross-Site Scripting 漏洞描述 Wing FTP 6.4.4 is vulnerable to cross-site scripting via its web interface because an arbitrary IFRAME eleme...
CVE-2023-43325: MooSocial 3.1.8 – Cross-Site Scripting
漏洞标题 CVE-2023-43325: MooSocial 3.1.8 - Cross-Site Scripting 漏洞描述 A reflected cross-site scripting (XSS) vulnerability exisits in the data[redirect_url] parameter on user lo...
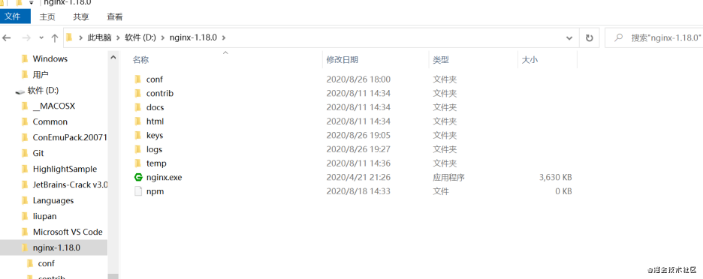
本地通过nginx配置反向代理的全过程记录_nginx
这篇文章主要给大家介绍了关于本地通过nginx配置反向代理的全过程,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 ...
CVE-2021-25082: WordPress Popup Builder < 4.0.7 - Remote Code Execution
漏洞标题 CVE-2021-25082: WordPress Popup Builder < 4.0.7 - Remote Code Execution 漏洞描述 Popup Builder WordPress plugin before 4.0.7 contains a local file inclusion caused by u...
CVE-2023-37580: Zimbra Collaboration Suite (ZCS) v.8.8.15 – Cross-Site Scripting
漏洞标题 CVE-2023-37580: Zimbra Collaboration Suite (ZCS) v.8.8.15 - Cross-Site Scripting 漏洞描述 Zimbra Collaboration (ZCS) 8 before 8.8.15 Patch 41 allows XSS in the Zimbra Clas...
CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 – SQL Injection
漏洞标题 CVE-2023-30150: PrestaShop leocustomajax 1.0 & 1.0.0 - SQL Injection 漏洞描述 PrestaShop leocustomajax 1.0 and 1.0.0 are vulnerable to SQL Injection via modules/leocus...

