




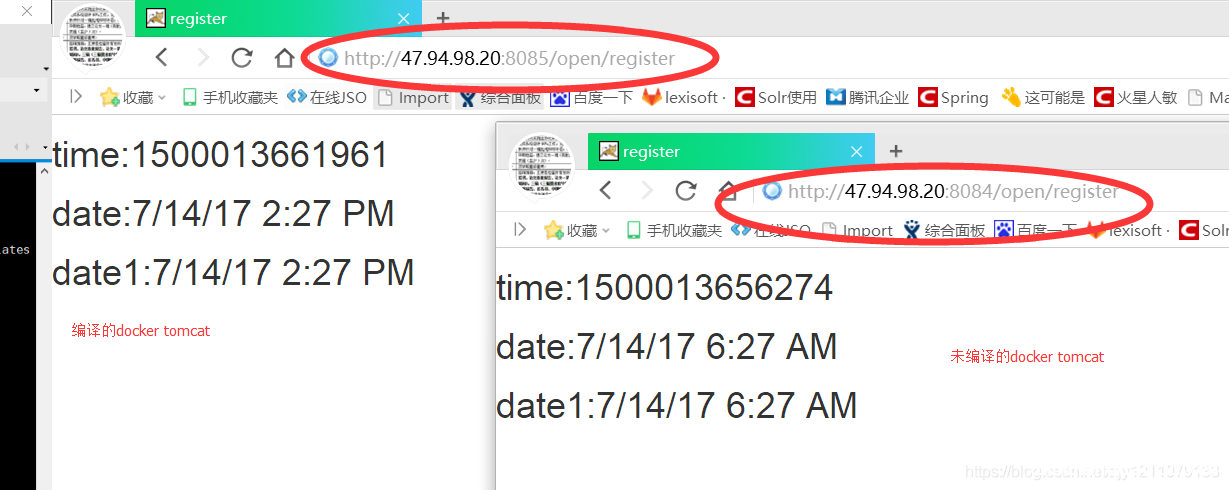
docker时区问题和迁移数据问题_docker
这篇文章主要介绍了docker时区问题和迁移数据问题,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 最新解决办法: ...
VMware Workstation Pro 16搭建CentOS8虚拟机集群的图文教程_VMware
这篇文章主要介绍了VMware Workstation Pro 16搭建CentOS8虚拟机集群,本文通过图文并茂的形式给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录准备...

CVE-2017-17562: Embedthis GoAhead <3.6.5 - Remote Code Execution
漏洞标题 CVE-2017-17562: Embedthis GoAhead <3.6.5 - Remote Code Execution 漏洞描述 description: Embedthis GoAhead before 3.6.5 allows remote code execution if CGI is enabled and...
CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837)
漏洞标题 CVE-2024-36837: CRMEB开源电商系统 /api/products SQL注入漏洞(CVE-2024-36837) 漏洞描述 该漏洞可以通过请求api的路径接口来进行SQL注入,进而可能导致敏感信息泄露,该注入可暴露后...
CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation
漏洞标题 CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation 漏洞描述 The plugin is vulnerable to privilege escalation due...
CVE-2023-39677: PrestaShop MyPrestaModules – PhpInfo Disclosure
漏洞标题 CVE-2023-39677: PrestaShop MyPrestaModules - PhpInfo Disclosure 漏洞描述 PrestaShop modules by MyPrestaModules expose PHPInfo PoC代码
CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...
CVE-2024-55956: Cleo Harmony < 5.8.0.24 - File Upload Vulnerability
漏洞标题 CVE-2024-55956: Cleo Harmony < 5.8.0.24 - File Upload Vulnerability 漏洞描述 In Cleo Harmony before 5.8.0.24, VLTrader before 5.8.0.24, and LexiCom before 5.8.0.24, an ...
CVE-2017-18362: Kaseya VSA 2017 ConnectWise ManagedITSync – Remote Code Execution
漏洞标题 CVE-2017-18362: Kaseya VSA 2017 ConnectWise ManagedITSync - Remote Code Execution 漏洞描述 ConnectWise ManagedITSync integration through 2017 for Kaseya VSA is vulnerable ...
CVE-2023-1020: Steveas WP Live Chat Shoutbox <= 1.4.2 - SQL Injection
漏洞标题 CVE-2023-1020: Steveas WP Live Chat Shoutbox <= 1.4.2 - SQL Injection 漏洞描述 The Steveas WP Live Chat Shoutbox WordPress plugin through 1.4.2 does not sanitise and es...
Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
CVE-2025-31486: Vite server.fs.deny Bypass – Local File Inclusion
漏洞标题 CVE-2025-31486: Vite server.fs.deny Bypass - Local File Inclusion 漏洞描述 Vite is a frontend tooling framework for javascript. The contents of arbitrary files can be retu...
CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure
漏洞标题 CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure 漏洞描述 WordPress EasyCart plugin before 2.0.6 contains an information disclosure vulnerability. An a...
CVE-2011-2523: VSFTPD 2.3.4 – Backdoor Command Execution
漏洞标题 CVE-2011-2523: VSFTPD 2.3.4 - Backdoor Command Execution 漏洞描述 VSFTPD v2.3.4 had a serious backdoor vulnerability allowing attackers to execute arbitrary commands on th...
CVE-2024-38472: Apache HTTPd Windows UNC – Server-Side Request Forgery
漏洞标题 CVE-2024-38472: Apache HTTPd Windows UNC - Server-Side Request Forgery 漏洞描述 SSRF in Apache HTTP Server on Windows allows to potentially leak NTML hashes to a malicious...
CVE-2013-2251: Apache Struts 2 – DefaultActionMapper Prefixes OGNL Code Execution (S2-016)
漏洞标题 CVE-2013-2251: Apache Struts 2 - DefaultActionMapper Prefixes OGNL Code Execution (S2-016) 漏洞描述 In Struts 2 before 2.3.15.1 the information following "action:&quo...

