





CVE-2009-2100: Joomla! JoomlaPraise Projectfork 2.0.10 – Local File Inclusion
漏洞标题 CVE-2009-2100: Joomla! JoomlaPraise Projectfork 2.0.10 - Local File Inclusion 漏洞描述 Joomla! JoomlaPraise Projectfork (com_projectfork) 2.0.10 allows remote attackers to...
CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal
漏洞标题 CVE-2023-6266: WordPress Backup Migration <= 1.3.6 - Path Traversal 漏洞描述 WordPress Backup Migration plugin versions up to 1.3.6 contain a path traversal and file va...
CVE-2018-19127: PHPCMS 2008 – Remote Code Execution via Template Injection
漏洞标题 CVE-2018-19127: PHPCMS 2008 - Remote Code Execution via Template Injection 漏洞描述 PHPCMS 2008 suffers from an unauthenticated RCE via template injection in type.php, whe...
CVE-2004-0437: Titan FTP Server 3.01 – DoS via LIST Command Disconnection
漏洞标题 CVE-2004-0437: Titan FTP Server 3.01 - DoS via LIST Command Disconnection 漏洞描述 Titan FTP Server version 3.01 build 163 (and possibly other older versions) contains a v...
CVE-2021-26598: ImpressCMS <1.4.3 - Incorrect Authorization
漏洞标题 CVE-2021-26598: ImpressCMS <1.4.3 - Incorrect Authorization 漏洞描述 ImpressCMS before 1.4.3 is susceptible to incorrect authorization via include/findusers.php. An att...
CVE-2024-34351: Next.js – Server Side Request Forgery (SSRF)
漏洞标题 CVE-2024-34351: Next.js - Server Side Request Forgery (SSRF) 漏洞描述 Next.Js, inferior to version 14.1.1, have its image optimization built-in component prone to SSRF. Po...
CVE-2018-1000129: Jolokia 1.3.7 – Cross-Site Scripting
漏洞标题 CVE-2018-1000129: Jolokia 1.3.7 - Cross-Site Scripting 漏洞描述 Jolokia 1.3.7 is vulnerable to cross-site scripting in the HTTP servlet and allows an attacker to execute m...
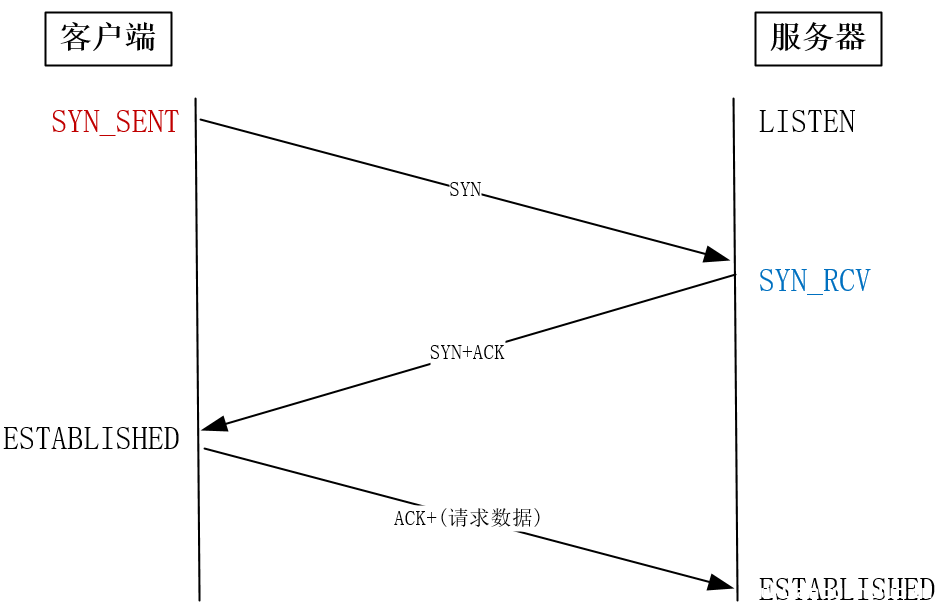
TCP性能调优实现原理及过程解析_服务器其它
这篇文章主要介绍了TCP性能调优实现原理及过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 三次握手阶段 客户端SYN包的重试次数 s...
CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection
漏洞标题 CVE-2020-10199: Nexus Repository before 3.21.2 allows JavaEL Injection 漏洞描述 漏洞触发需要任意账户权限 body="Nexus Repository Manager" app="Nexus-Reposito...
CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS
漏洞标题 CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS 漏洞描述 FileZilla Server versions prior to 0.9.31 contain a buffer overflow vulnerability relate...
CVE-2021-20123: Draytek VigorConnect 1.6.0-B – Local File Inclusion
漏洞标题 CVE-2021-20123: Draytek VigorConnect 1.6.0-B - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download func...
CVE-2025-0868: DocsGPT – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-0868: DocsGPT - Unauthenticated Remote Code Execution 漏洞描述 A vulnerability, that could result in Remote Code Execution (RCE), has been found in DocsGPT. Due t...
CVE-2023-34124: SonicWall GMS and Analytics Web Services – Shell Injection
漏洞标题 CVE-2023-34124: SonicWall GMS and Analytics Web Services - Shell Injection 漏洞描述 The authentication mechanism in SonicWall GMS and Analytics Web Services had insufficie...
CVE-2021-39152: XStream <1.4.18 - Server-Side Request Forgery
漏洞标题 CVE-2021-39152: XStream <1.4.18 - Server-Side Request Forgery 漏洞描述 XStream before 1.4.18 is susceptible to server-side request forgery. An attacker can request data...
CVE-2022-34047: WAVLINK WN530HG4 – Improper Access Control
漏洞标题 CVE-2022-34047: WAVLINK WN530HG4 - Improper Access Control 漏洞描述 WAVLINK WN530HG4 M30HG4.V5030.191116 is susceptible to improper access control. An attacker can obtain ...
(CVE-2021-39141) XStream 反序列化漏洞
漏洞标题 (CVE-2021-39141) XStream 反序列化漏洞 漏洞描述 (CVE-2021-39141) XStream 反序列化漏洞 PoC代码 暂无

