





CVE-2022-0281: Microweber Information Disclosure
漏洞标题 CVE-2022-0281: Microweber Information Disclosure 漏洞描述 Microweber contains a vulnerability that allows exposure of sensitive information to an unauthorized actor in Pac...
CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 – Unauthenticated Remote Command Execution
漏洞标题 CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 - Unauthenticated Remote Command Execution 漏洞描述 Zoho ManageEngine ADSelfService Plus version 6113 and prior ...
CVE-2022-25356: Alt-n/MDaemon Security Gateway <=8.5.0 - XML Injection
漏洞标题 CVE-2022-25356: Alt-n/MDaemon Security Gateway <=8.5.0 - XML Injection 漏洞描述 Alt-n/MDaemon Security Gateway through 8.5.0 is susceptible to XML injection via Securit...
CVE-2022-42475: Fortinet SSL-VPN – Heap-Based Buffer Overflow
漏洞标题 CVE-2022-42475: Fortinet SSL-VPN - Heap-Based Buffer Overflow 漏洞描述 A heap-based buffer overflow vulnerability [CWE-122] in FortiOS SSL-VPN (versions 7.2.0 through 7.2....
CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
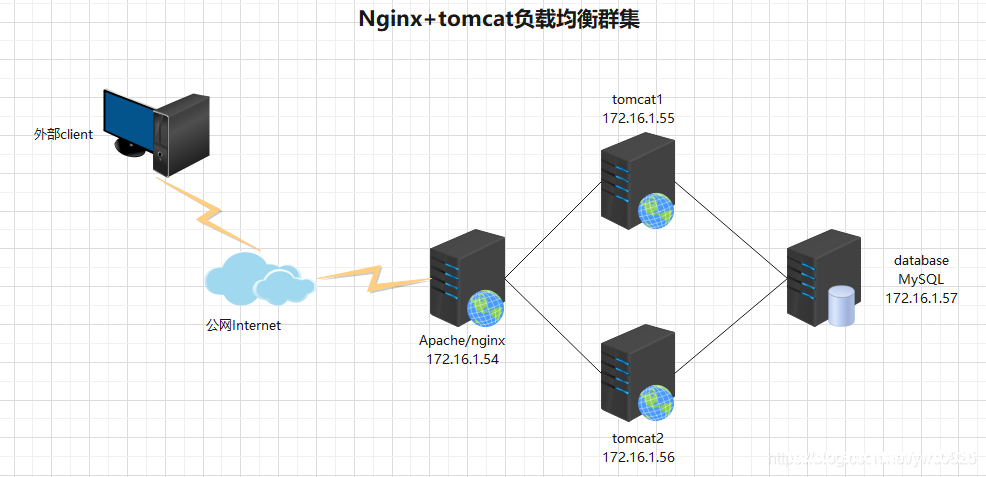
Nginx+tomcat负载均衡集群的实现方法_nginx
这篇文章主要介绍了Nginx+tomcat负载均衡集群,的实现方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 实验环境如下 这里需要准备4台服务器(...
Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195)
漏洞标题 Apache OFBiz /viewdatafile 代码执行漏洞(CVE-2024-45195) 漏洞描述 Apache OFBiz是一个开源企业资源规划(ERP)系统。它提供了一套企业应用程序,集成并自动化企业的许多业务流程...
CVE-2023-1880: Phpmyfaq v3.1.11 – Cross-Site Scripting
漏洞标题 CVE-2023-1880: Phpmyfaq v3.1.11 - Cross-Site Scripting 漏洞描述 Phpmyfaq v3.1.11 is vulnerable to reflected XSS in send2friend because the 'artlang' parameter is...
CVE-2021-25298: Nagios XI 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25298: Nagios XI 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command inject...
CVE-2018-6605: Joomla Ext zhbaidumap sql inject
漏洞标题 CVE-2018-6605: Joomla Ext zhbaidumap sql inject 漏洞描述 Joomla Ext zhbaidumap sql inject fofa: app="Joomla" shodan: http.html:"Joomla" PoC代码
Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556)
漏洞标题 Apache Struts2(S2-001)远程代码执行漏洞(CVE-2007-4556) 漏洞描述 在Struts2 WebWork 2.1+ 和 Struts 2 的“altSyntax”功能允许将 OGNL表达式插入到文本字符串中并进行递归处理。这...
Atlassian Jira 信息泄露(CVE-2019-3401)
漏洞标题 Atlassian Jira 信息泄露(CVE-2019-3401) 漏洞描述 Jira 7.13.3之前版本和8.1.1之前版本8.0.0中的ManageFilters.jspa资源允许远程攻击者通过不正确的授权检查枚举用户名。 PoC代码 暂...

Docker默认网段修改实现方法解析_docker
这篇文章主要介绍了Docker默认网段修改实现方法解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 背景 公司的服务器全部都是购买的阿里...
CVE-2025-32430: XWiki Platform – Cross-Site Scripting
漏洞标题 CVE-2025-32430: XWiki Platform - Cross-Site Scripting 漏洞描述 XWiki Platform versions >= 4.2-milestone-3 and < 16.4.8, >= 16.5.0-rc-1 and < 16.10.6, and >=...
CVE-2022-2130: Microweber < 1.2.17 - Cross-Site Scripting
漏洞标题 CVE-2022-2130: Microweber < 1.2.17 - Cross-Site Scripting 漏洞描述 Cross-site Scripting (XSS) vulnerability in the /demo/editor_tools/module endpoint via the 'type...
CVE-2022-0963: Microweber <1.2.12 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-0963: Microweber <1.2.12 - Stored Cross-Site Scripting 漏洞描述 Microweber prior to 1.2.12 contains a stored cross-site scripting vulnerability. It allows unre...

