





CVE-2025-55169: WeGIA – Directory Traversal
漏洞标题 CVE-2025-55169: WeGIA - Directory Traversal 漏洞描述 WeGIA is an open source web manager with a focus on the Portuguese language and charitable institutions. Prior to vers...
CVE-2023-27639: PrestaShop TshirteCommerce – Directory Traversal
漏洞标题 CVE-2023-27639: PrestaShop TshirteCommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
CVE-2023-27639: PrestaShop TshirteCommerce – Directory Traversal
漏洞标题 CVE-2023-27639: PrestaShop TshirteCommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
CVE-2023-6634: LearnPress < 4.2.5.8 - Remote Code Execution
漏洞标题 CVE-2023-6634: LearnPress < 4.2.5.8 - Remote Code Execution 漏洞描述 The LearnPress plugin for WordPress is vulnerable to Command Injection in all versions up to, and i...
CVE-2024-48455: Netis Wifi Router – Information Disclosure
漏洞标题 CVE-2024-48455: Netis Wifi Router - Information Disclosure 漏洞描述 An issue in Netis Wifi6 Router NX10 2.0.1.3643 and 2.0.1.3582 and Netis Wifi 11AC Router NC65 3.0.0.374...
CVE-2023-46347: PrestaShop Step by Step products Pack – SQL Injection
漏洞标题 CVE-2023-46347: PrestaShop Step by Step products Pack - SQL Injection 漏洞描述 In the module “Step by Step products Pack” (ndk_steppingpack) up to 1.5.6 from NDK Design ...
CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure
漏洞标题 CVE-2014-4942: WordPress EasyCart <2.0.6 - Information Disclosure 漏洞描述 WordPress EasyCart plugin before 2.0.6 contains an information disclosure vulnerability. An a...
CVE-2018-7314: Joomla SQL Inject
漏洞标题 CVE-2018-7314: Joomla SQL Inject 漏洞描述 Joomla SQL Inject fofa: app="Joomla" shodan: http.html:"Joomla" PoC代码
CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
CVE-2025-51586: PrestaShop – Information Disclosure
漏洞标题 CVE-2025-51586: PrestaShop - Information Disclosure 漏洞描述 User enumeration vulnerability in the AdminLogin controller in PrestaShop 1.7 through 8.2.2 allows remote atta...
CVE-2020-8512: IceWarp WebMail Server <=11.4.4.1 - Cross-Site Scripting
漏洞标题 CVE-2020-8512: IceWarp WebMail Server <=11.4.4.1 - Cross-Site Scripting 漏洞描述 IceWarp Webmail Server through 11.4.4.1 contains a cross-site scripting vulnerability i...
CVE-2021-25008: The Code Snippets WordPress Plugin < 2.14.3 - Cross-Site Scripting
漏洞标题 CVE-2021-25008: The Code Snippets WordPress Plugin < 2.14.3 - Cross-Site Scripting 漏洞描述 The Wordpress plugin Code Snippets before 2.14.3 does not escape the snippet...
CVE-2022-28508: MantisBT < 2.25.2 - Cross-Site Scripting
漏洞标题 CVE-2022-28508: MantisBT < 2.25.2 - Cross-Site Scripting 漏洞描述 MantisBT before 2.25.2 contains a cross-site scripting vulnerability in browser_search_plugin.php. The...
CVE-2024-33575: User Meta WP Plugin < 3.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-33575: User Meta WP Plugin < 3.1 - Sensitive Information Exposure 漏洞描述 The User Meta is vulnerable to Sensitive Information Exposure in all versions up to,...
CVE-2021-21287: MinIO Browser API – Server-Side Request Forgery
漏洞标题 CVE-2021-21287: MinIO Browser API - Server-Side Request Forgery 漏洞描述 MinIO Browser API before version RELEASE.2021-01-30T00-20-58Z contains a server-side request forge...
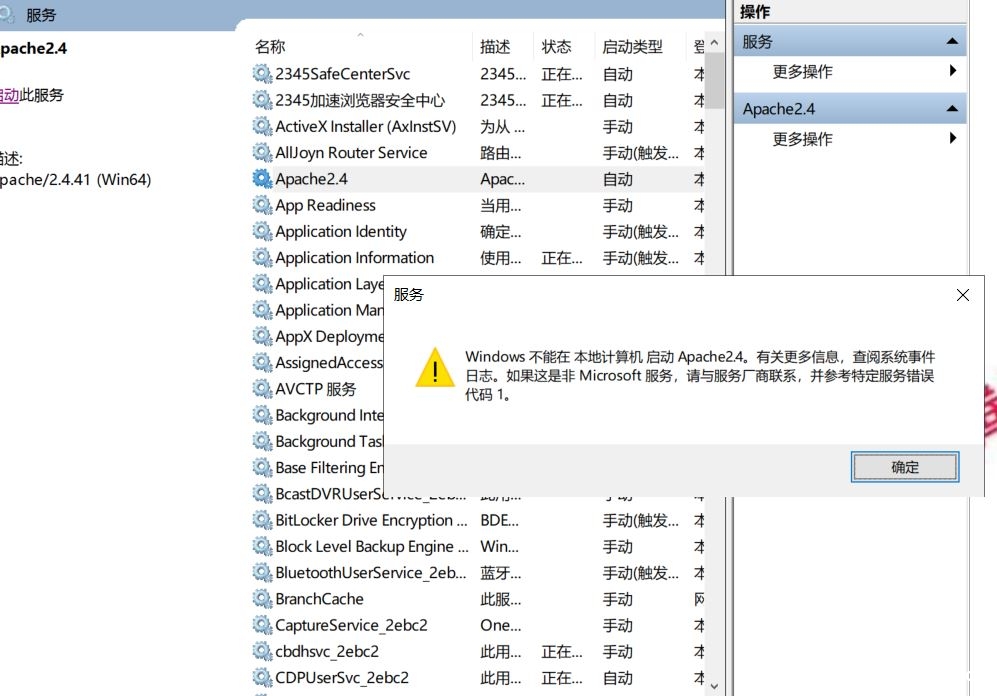
Apache安装后出现服务无法启动(服务里启动出现错误代码1)_Linux
很多朋友都遇到过这样的问题Apache安装后,显示安装成功,但是出现服务无法启动服务里启动出现错误代码1,怎么解决这个问题呢,下面小编通过本文给大家详细介绍下,需要的朋友参考下吧 目录一、...

