





CraftCMS /ConditionsController.php 代码执行漏洞(CVE-2023-41892)
漏洞标题 CraftCMS /ConditionsController.php 代码执行漏洞(CVE-2023-41892) 漏洞描述 Craft CMS是一个开源的内容管理系统,它专注于用户友好的内容创建过程,逻辑清晰明了,是一个高度自由...
74CMS任意文件读取(CVE-2022-26271)
漏洞标题 74CMS任意文件读取(CVE-2022-26271) 漏洞描述 74CMS人才招聘系统/upload/application/index/controller/Download.php文件任意文件读取漏洞,可读取系统配置等文件,导致网站处于极度不...
CVE-2023-30869: Easy Digital Downloads – Privilege Escalation
漏洞标题 CVE-2023-30869: Easy Digital Downloads - Privilege Escalation 漏洞描述 Improper Authentication vulnerability in Easy Digital Downloads plugin allows unauth. Privilege Esca...
CVE-2024-37656: GnuBoard5 5.5.16 – Open Redirect
漏洞标题 CVE-2024-37656: GnuBoard5 5.5.16 - Open Redirect 漏洞描述 Gnuboard5 5.5.16 contains an open redirect vulnerability caused by insufficient URL parameter verification in bbs...
CVE-2020-9484: Apache Tomcat Remote Command Execution
漏洞标题 CVE-2020-9484: Apache Tomcat Remote Command Execution 漏洞描述 When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7...
Apache Flink 任意文件写入(CVE-2020-17518)
漏洞标题 Apache Flink 任意文件写入(CVE-2020-17518) 漏洞描述 【漏洞对象】Apache Flink 【涉及版本】Flink1.5.1-1.11.2 \【漏洞描述】ApacheFlink是一个开源的流处理框架,具有强大的流处理...
CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
CVE-2022-2414: FreeIPA – XML Entity Injection
漏洞标题 CVE-2022-2414: FreeIPA - XML Entity Injection 漏洞描述 Access to external entities when parsing XML documents can lead to XML external entity (XXE) attacks. This flaw allo...
CVE-2023-30869: Easy Digital Downloads – Privilege Escalation
漏洞标题 CVE-2023-30869: Easy Digital Downloads - Privilege Escalation 漏洞描述 Improper Authentication vulnerability in Easy Digital Downloads plugin allows unauth. Privilege Esca...
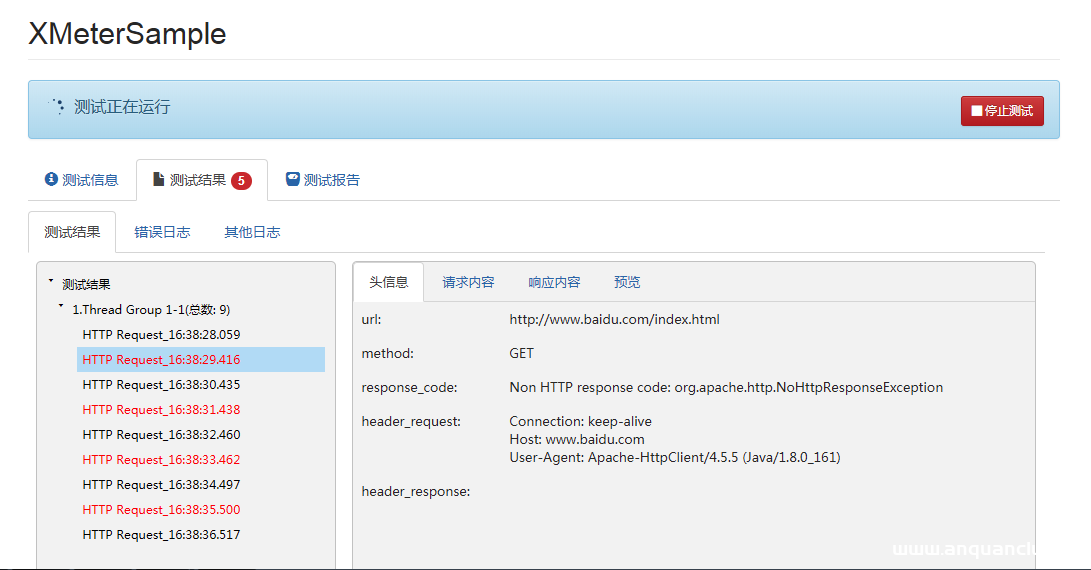
Xmeter API接口测试工具使用方法解析_服务器其它
这篇文章主要介绍了Xmeter API接口测试工具使用方法解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 XMeter API提供了基于JMeter的一...
CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
CVE-2024-47533: Cobbler ‘XML-RPC’ – Authentication Bypass
漏洞标题 CVE-2024-47533: Cobbler 'XML-RPC' - Authentication Bypass 漏洞描述 Cobbler, a Linux installation server that allows for rapid setup of network installation envir...
CVE-2023-35844: Lightdash Arbitrary File Read
漏洞标题 CVE-2023-35844: Lightdash Arbitrary File Read 漏洞描述 Lightdash是一款数据分析平台,它可以让数据团队和其他业务部门聚集在一起以做出更好的数据驱动决策 Lightdash 0.510.3之前...
CVE-2023-27638: tshirtecommerce PrestaShop Module – SQL Injection
漏洞标题 CVE-2023-27638: tshirtecommerce PrestaShop Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via the...
CVE-2023-39120: Nodogsplash – Directory Traversal
漏洞标题 CVE-2023-39120: Nodogsplash - Directory Traversal 漏洞描述 Nodogsplash product was affected by a directory traversal vulnerability that also impacted the OpenWrt product. ...
CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection
漏洞标题 CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection 漏洞描述 CRLF Injection leads to Stack Trace Exposure due to lack of filtering at https://demo.microweber.org/ in Pa...

