





CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 – Local File Inclusion
漏洞标题 CVE-2017-1000029: Oracle GlassFish Server Open Source Edition 3.0.1 - Local File Inclusion 漏洞描述 Oracle GlassFish Server Open Source Edition 3.0.1 (build 22) is vulnera...
CVE-2004-0437: Titan FTP Server 3.01 – DoS via LIST Command Disconnection
漏洞标题 CVE-2004-0437: Titan FTP Server 3.01 - DoS via LIST Command Disconnection 漏洞描述 Titan FTP Server version 3.01 build 163 (and possibly other older versions) contains a v...
CVE-2021-26598: ImpressCMS <1.4.3 - Incorrect Authorization
漏洞标题 CVE-2021-26598: ImpressCMS <1.4.3 - Incorrect Authorization 漏洞描述 ImpressCMS before 1.4.3 is susceptible to incorrect authorization via include/findusers.php. An att...
CVE-2018-1000129: Jolokia 1.3.7 – Cross-Site Scripting
漏洞标题 CVE-2018-1000129: Jolokia 1.3.7 - Cross-Site Scripting 漏洞描述 Jolokia 1.3.7 is vulnerable to cross-site scripting in the HTTP servlet and allows an attacker to execute m...
CVE-2014-4210: Oracle Weblogic – Server-Side Request Forgery
漏洞标题 CVE-2014-4210: Oracle Weblogic - Server-Side Request Forgery 漏洞描述 An unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0...
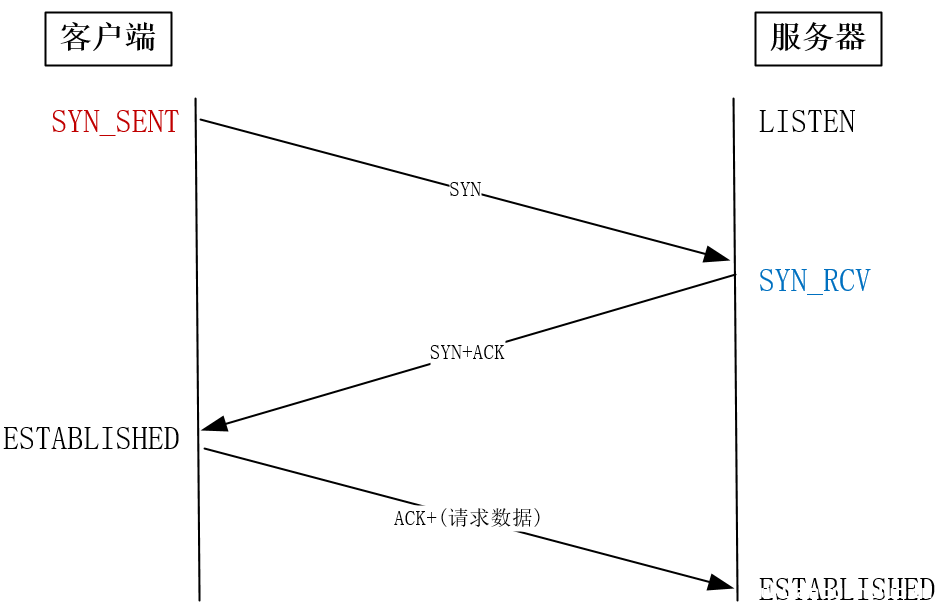
TCP性能调优实现原理及过程解析_服务器其它
这篇文章主要介绍了TCP性能调优实现原理及过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 三次握手阶段 客户端SYN包的重试次数 s...
CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS
漏洞标题 CVE-2009-0884: FileZilla Server < 0.9.31 - SSL/TLS Packet Overflow DoS 漏洞描述 FileZilla Server versions prior to 0.9.31 contain a buffer overflow vulnerability relate...
CVE-2021-20123: Draytek VigorConnect 1.6.0-B – Local File Inclusion
漏洞标题 CVE-2021-20123: Draytek VigorConnect 1.6.0-B - Local File Inclusion 漏洞描述 Draytek VigorConnect 1.6.0-B3 is susceptible to local file inclusion in the file download func...
CVE-2025-0868: DocsGPT – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-0868: DocsGPT - Unauthenticated Remote Code Execution 漏洞描述 A vulnerability, that could result in Remote Code Execution (RCE), has been found in DocsGPT. Due t...
CVE-2024-6220: WordPress Keydatas ≤ 2.5.2 – Arbitrary File Upload
漏洞标题 CVE-2024-6220: WordPress Keydatas ≤ 2.5.2 - Arbitrary File Upload 漏洞描述 The Keydatas plugin for WordPress (known in Chinese as "简数采集器") is vulnerable to...
CVE-2023-34124: SonicWall GMS and Analytics Web Services – Shell Injection
漏洞标题 CVE-2023-34124: SonicWall GMS and Analytics Web Services - Shell Injection 漏洞描述 The authentication mechanism in SonicWall GMS and Analytics Web Services had insufficie...
CVE-2023-21839: Oracle WebLogic Server – Unauthorized Access
漏洞标题 CVE-2023-21839: Oracle WebLogic Server - Unauthorized Access 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Su...
CVE-2023-39677: PrestaShop MyPrestaModules – PhpInfo Disclosure
漏洞标题 CVE-2023-39677: PrestaShop MyPrestaModules - PhpInfo Disclosure 漏洞描述 PrestaShop modules by MyPrestaModules expose PHPInfo PoC代码
CVE-2021-39152: XStream <1.4.18 - Server-Side Request Forgery
漏洞标题 CVE-2021-39152: XStream <1.4.18 - Server-Side Request Forgery 漏洞描述 XStream before 1.4.18 is susceptible to server-side request forgery. An attacker can request data...
CVE-2022-34047: WAVLINK WN530HG4 – Improper Access Control
漏洞标题 CVE-2022-34047: WAVLINK WN530HG4 - Improper Access Control 漏洞描述 WAVLINK WN530HG4 M30HG4.V5030.191116 is susceptible to improper access control. An attacker can obtain ...
(CVE-2021-39141) XStream 反序列化漏洞
漏洞标题 (CVE-2021-39141) XStream 反序列化漏洞 漏洞描述 (CVE-2021-39141) XStream 反序列化漏洞 PoC代码 暂无

