





CraftCMS /ConditionsController.php 代码执行漏洞(CVE-2023-41892)
漏洞标题 CraftCMS /ConditionsController.php 代码执行漏洞(CVE-2023-41892) 漏洞描述 Craft CMS是一个开源的内容管理系统,它专注于用户友好的内容创建过程,逻辑清晰明了,是一个高度自由...
74CMS任意文件读取(CVE-2022-26271)
漏洞标题 74CMS任意文件读取(CVE-2022-26271) 漏洞描述 74CMS人才招聘系统/upload/application/index/controller/Download.php文件任意文件读取漏洞,可读取系统配置等文件,导致网站处于极度不...
CVE-2023-30869: Easy Digital Downloads – Privilege Escalation
漏洞标题 CVE-2023-30869: Easy Digital Downloads - Privilege Escalation 漏洞描述 Improper Authentication vulnerability in Easy Digital Downloads plugin allows unauth. Privilege Esca...
CVE-2020-9484: Apache Tomcat Remote Command Execution
漏洞标题 CVE-2020-9484: Apache Tomcat Remote Command Execution 漏洞描述 When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7...
CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
CVE-2023-37580: Zimbra Collaboration Suite (ZCS) v.8.8.15 – Cross-Site Scripting
漏洞标题 CVE-2023-37580: Zimbra Collaboration Suite (ZCS) v.8.8.15 - Cross-Site Scripting 漏洞描述 Zimbra Collaboration (ZCS) 8 before 8.8.15 Patch 41 allows XSS in the Zimbra Clas...
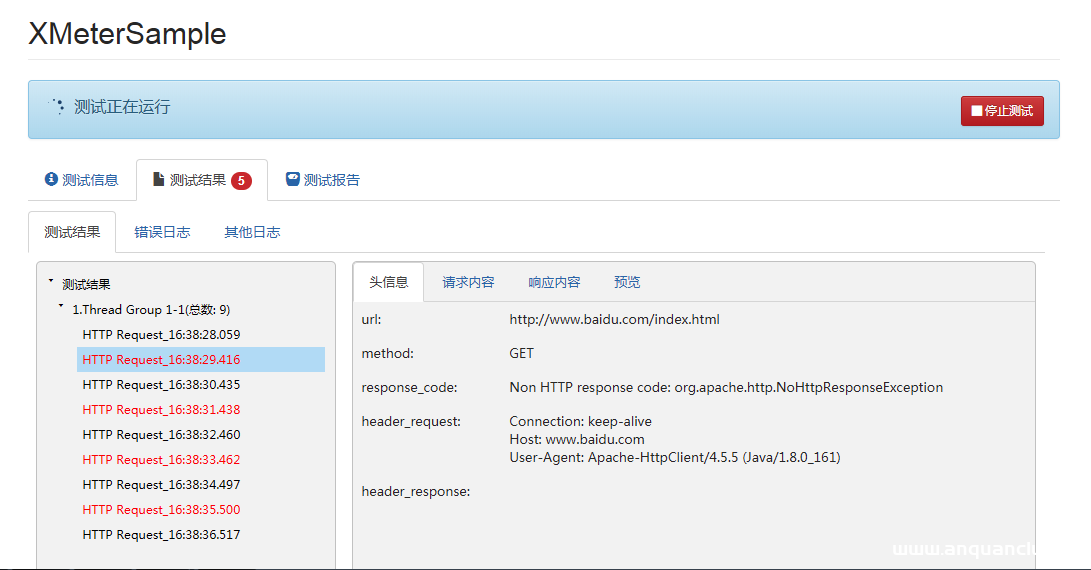
Xmeter API接口测试工具使用方法解析_服务器其它
这篇文章主要介绍了Xmeter API接口测试工具使用方法解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 XMeter API提供了基于JMeter的一...
CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload
漏洞标题 CVE-2022-4328: WooCommerce Checkout Field Manager < 18.0 - Arbitrary File Upload 漏洞描述 The WooCommerce Checkout Field Manager WordPress plugin before 18.0 does not v...
CVE-2024-47533: Cobbler ‘XML-RPC’ – Authentication Bypass
漏洞标题 CVE-2024-47533: Cobbler 'XML-RPC' - Authentication Bypass 漏洞描述 Cobbler, a Linux installation server that allows for rapid setup of network installation envir...
CVE-2017-10974: Yaws 1.91 – Local File Inclusion
漏洞标题 CVE-2017-10974: Yaws 1.91 - Local File Inclusion 漏洞描述 Yaws 1.91 allows unauthenticated local file inclusion via /%5C../ submitted to port 8080. PoC代码
CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection
漏洞标题 CVE-2022-0666: Microweber < 1.2.11 - CRLF Injection 漏洞描述 CRLF Injection leads to Stack Trace Exposure due to lack of filtering at https://demo.microweber.org/ in Pa...
CVE-2019-1003000: Jenkins Script Security Plugin <=1.49 - Sandbox Bypass
漏洞标题 CVE-2019-1003000: Jenkins Script Security Plugin <=1.49 - Sandbox Bypass 漏洞描述 A sandbox bypass vulnerability exists in the Jenkins Script Security Plugin (versions ...
CVE-2021-22175: GitLab CI Lint API – Server-Side Request Forgery
漏洞标题 CVE-2021-22175: GitLab CI Lint API - Server-Side Request Forgery 漏洞描述 GitLab 10.5 and later contain a server-side request forgery caused by insecure handling of webhoo...
CVE-2017-11629: FineCMS <=5.0.10 - Cross-Site Scripting
漏洞标题 CVE-2017-11629: FineCMS <=5.0.10 - Cross-Site Scripting 漏洞描述 FineCMS through 5.0.10 contains a cross-site scripting vulnerability in controllers/api.php via the fun...

