





CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞
漏洞标题 CVE-2020-7961: Liferay Portal RCE 反序列化命令执行漏洞 漏洞描述 Liferay Portal CE是一款用来快速构建网站的开源系统。其7.2.0 GA1及以前的版本API接口中存在一处反序列化漏洞,利...
CVE-2025-55749: XWiki – Information Disclosure
漏洞标题 CVE-2025-55749: XWiki - Information Disclosure 漏洞描述 XWiki 16.7.0 to 16.10.11, 17.4.4, and 17.7.0 using XJetty contains an information disclosure vulnerability caused b...
CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting
漏洞标题 CVE-2023-4151: Store Locator WordPress < 1.4.13 - Cross-Site Scripting 漏洞描述 The Store Locator WordPress plugin before 1.4.13 does not sanitise and escape an invalid...
CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 – SQL Injection
漏洞标题 CVE-2018-7314: Joomla! Component PrayerCenter 3.0.2 - SQL Injection 漏洞描述 SQL Injection exists in the PrayerCenter 3.0.2 component for Joomla! via the sessionid paramet...
(CVE-2023-3765) MLflow 绝对路径遍历漏洞
漏洞标题 (CVE-2023-3765) MLflow 绝对路径遍历漏洞 漏洞描述 (CVE-2023-3765) MLflow 绝对路径遍历漏洞 PoC代码 暂无
CVE-2021-39146: XStream 1.4.18 – Arbitrary Code Execution
漏洞标题 CVE-2021-39146: XStream 1.4.18 - Arbitrary Code Execution 漏洞描述 XStream 1.4.18 is susceptible to remote code execution. An attacker can execute commands of the host by ...
CVE-2017-11107: phpLDAPadmin <= 1.2.3 - Reflected XSS
漏洞标题 CVE-2017-11107: phpLDAPadmin <= 1.2.3 - Reflected XSS 漏洞描述 phpLDAPadmin <= 1.2.3 contains a reflected cross-site scripting caused by unsanitized input in htdocs/...
CVE-2023-4220: Chamilo LMS <= 1.11.24 - Remote Code Execution
漏洞标题 CVE-2023-4220: Chamilo LMS <= 1.11.24 - Remote Code Execution 漏洞描述 Unrestricted file upload in big file upload functionality in `/main/inc/lib/javascript/bigupload/...
CVE-2022-25481: ThinkPHP 5.0.24 – Information Disclosure
漏洞标题 CVE-2022-25481: ThinkPHP 5.0.24 - Information Disclosure 漏洞描述 ThinkPHP 5.0.24 is susceptible to information disclosure. This version was configured without the PATHINF...
docker安装tomcat并部署Springboot项目war包的方法_docker
这篇文章主要介绍了docker安装tomcat并部署Springboot项目war包的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 说来也简单,直接上教程吧...
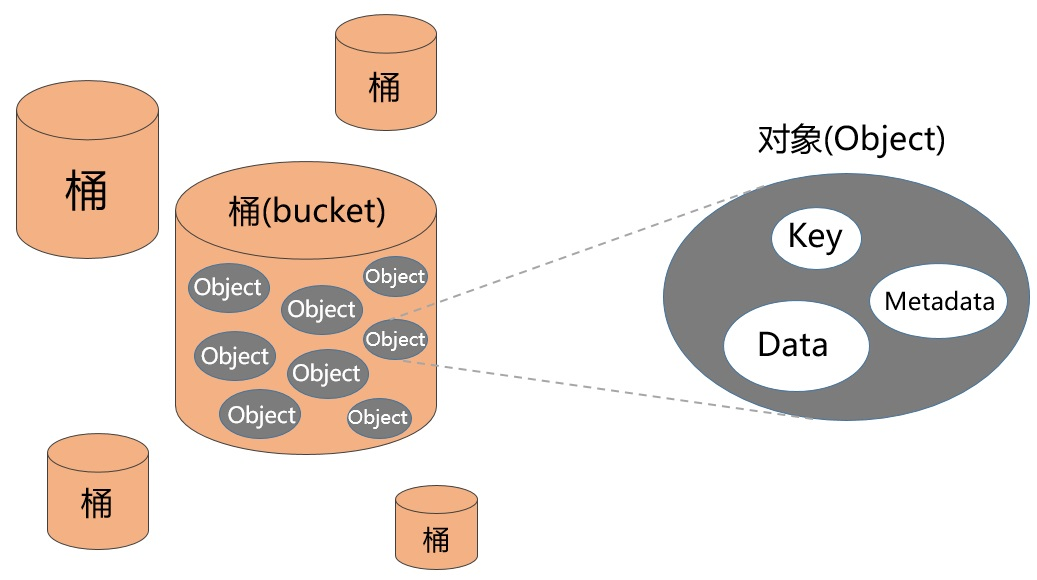
AWS S3 对象存储攻防
0x00 前言 对象存储(Object-Based Storage),也可以叫做面向对象的存储,现在也有不少厂商直接把它叫做云存储。 说到对象存储就不得不提 Amazon,Amazon S3 (Simple Storage Service) 简单存...
CVE-2025-27222: TRUfusion Enterprise <= 7.10.4.0 - Path Traversal
漏洞标题 CVE-2025-27222: TRUfusion Enterprise <= 7.10.4.0 - Path Traversal 漏洞描述 Pre-Auth Path Traversal Allowing to Leak Local server files disclosing sensitive clear-text p...
CVE-2023-22952: SugarCRM Unauthenticated – Remote Code Execution
漏洞标题 CVE-2023-22952: SugarCRM Unauthenticated - Remote Code Execution 漏洞描述 In SugarCRM before 12.0. Hotfix 91155, a crafted request can inject custom PHP code through the E...
CVE-2025-2746: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0011)
漏洞标题 CVE-2025-2746: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0011) 漏洞描述 Before Kentico Xperience 13 Hotfix 173, this vulnerability can be e...
CVE-2020-5405: Spring Cloud Config – Local File Inclusion
漏洞标题 CVE-2020-5405: Spring Cloud Config - Local File Inclusion 漏洞描述 Spring Cloud Config versions 2.2.x prior to 2.2.2, 2.1.x prior to 2.1.7, and older unsupported versions ...
CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion
漏洞标题 CVE-2015-1000012: WordPress MyPixs <=0.3 - Local File Inclusion 漏洞描述 WordPress MyPixs 0.3 and prior contains a local file inclusion vulnerability. PoC代码

