





CVE-2024-0986: Issabel Authenticated – Remote Code Execution
漏洞标题 CVE-2024-0986: Issabel Authenticated - Remote Code Execution 漏洞描述 A vulnerability was found in Issabel PBX 4.0.0. It has been rated as critical. This issue affects som...

如何使用Docker搭建pypi私有仓库_docker
这篇文章主要介绍了如何使用Docker搭建pypi私有仓库,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、搭建 1、准备htpasswd.txt文件 该...
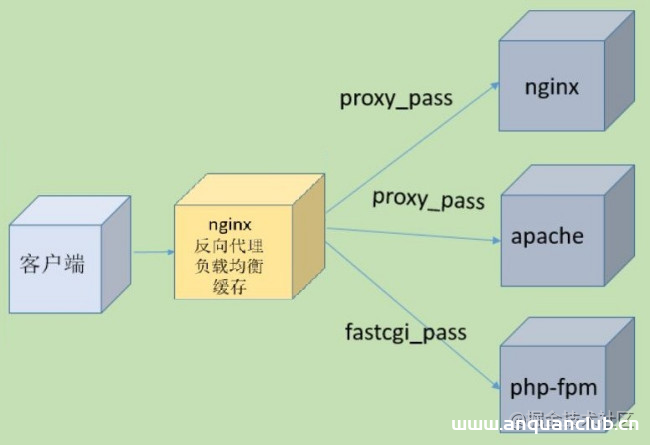
Nginx反向代理入门实战指南_nginx
反向代理:反向代理也叫reverse proxy,指的是代理外网用户的请求到内部的指定web服务器,并将数据返回给用户的一种方式,这是用的比较多的一种方式,下面这篇文章主要给大家介绍了关于Nginx反向代...
spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+
漏洞标题 spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+ 漏洞描述 A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to rem...
CVE-2015-7245: D-Link DVG-N5402SP – Local File Inclusion
漏洞标题 CVE-2015-7245: D-Link DVG-N5402SP - Local File Inclusion 漏洞描述 D-Link DVG-N5402SP is susceptible to local file inclusion in products with firmware W1000CN-00, W1000CN-0...
CVE-2023-30192: PrestaShop ‘possearchproducts’ <= 1.7 - SQL Injection
漏洞标题 CVE-2023-30192: PrestaShop 'possearchproducts' <= 1.7 - SQL Injection 漏洞描述 In the module “Search Products” (possearchproducts) from PosThemes for Presta...
CVE-2023-4450: JeecgBoot JimuReport – Template injection
漏洞标题 CVE-2023-4450: JeecgBoot JimuReport - Template injection 漏洞描述 A vulnerability was found in jeecgboot JimuReport up to 1.6.0. It has been declared as critical. Affected...
CVE-2025-64446: FortiWeb – Authentication Bypass
漏洞标题 CVE-2025-64446: FortiWeb - Authentication Bypass 漏洞描述 A relative path traversal vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.1, FortiWeb 7.6.0 through 7.6.4, F...
CVE-2022-1904: WordPress Easy Pricing Tables <3.2.1 - Cross-Site Scripting
漏洞标题 CVE-2022-1904: WordPress Easy Pricing Tables <3.2.1 - Cross-Site Scripting 漏洞描述 WordPress Easy Pricing Tables plugin before 3.2.1 contains a reflected cross-site sc...
CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
CVE-2015-6477: Nordex NC2 – Cross-Site Scripting
漏洞标题 CVE-2015-6477: Nordex NC2 - Cross-Site Scripting 漏洞描述 Nordex NC2 contains a cross-site scripting vulnerability which allows an attacker to execute arbitrary script cod...
CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
CVE-2025-52488: DNN (DotNetNuke) – Unicode Path Normalization NTLM Hash Disclosure
漏洞标题 CVE-2025-52488: DNN (DotNetNuke) - Unicode Path Normalization NTLM Hash Disclosure 漏洞描述 DNN (formerly DotNetNuke) is an open-source web content management platform (CM...
CVE-2023-33193: Emby Server – Authentication Bypass
漏洞标题 CVE-2023-33193: Emby Server - Authentication Bypass 漏洞描述 Emby Server is a user-installable home media server which stores and organizes a user's media files of vi...
CVE-2025-47423: Personal Weather Station Dashboard 12 – Directory Traversal
漏洞标题 CVE-2025-47423: Personal Weather Station Dashboard 12 - Directory Traversal 漏洞描述 Personal Weather Station Dashboard 12_lts allows unauthenticated remote attackers to r...
CVE-2023-6023: VertaAI ModelDB – Path Traversal
漏洞标题 CVE-2023-6023: VertaAI ModelDB - Path Traversal 漏洞描述 The endpoint "/api/v1/artifact/getArtifact?artifact_path=" is vulnerable to path traversal. The main cau...

