





CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway – Remote Code Injection
漏洞标题 CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway - Remote Code Injection 漏洞描述 Citrix ADC and NetScaler Gateway are susceptible to remote code injection. An attac...
CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668)
漏洞标题 CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
CVE-2023-41621: Emlog Pro v2.1.14 – Cross-Site Scripting
漏洞标题 CVE-2023-41621: Emlog Pro v2.1.14 - Cross-Site Scripting 漏洞描述 Cross Site Scripting (XSS) vulnerability in Emlog Pro v2.1.14 via /admin/store.php. PoC代码
CVE-2025-53364: Parse Server – GraphQL Schema Information Disclosure
漏洞标题 CVE-2025-53364: Parse Server - GraphQL Schema Information Disclosure 漏洞描述 The Parse Server GraphQL API previously allowed public access to the GraphQL schema without r...

docker 添加端口及获取dockerfile的方法_docker
这篇文章主要介绍了docker 添加端口及获取dockerfile的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 从dock...
CVE-2024-0986: Issabel Authenticated – Remote Code Execution
漏洞标题 CVE-2024-0986: Issabel Authenticated - Remote Code Execution 漏洞描述 A vulnerability was found in Issabel PBX 4.0.0. It has been rated as critical. This issue affects som...
如何使用Docker搭建pypi私有仓库_docker
这篇文章主要介绍了如何使用Docker搭建pypi私有仓库,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、搭建 1、准备htpasswd.txt文件 该...
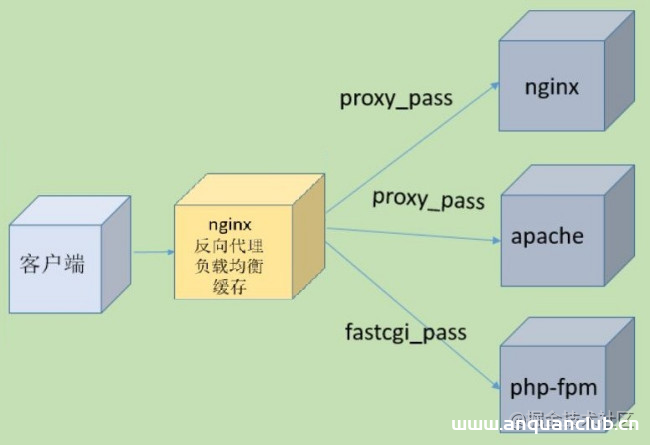
Nginx反向代理入门实战指南_nginx
反向代理:反向代理也叫reverse proxy,指的是代理外网用户的请求到内部的指定web服务器,并将数据返回给用户的一种方式,这是用的比较多的一种方式,下面这篇文章主要给大家介绍了关于Nginx反向代...
spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+
漏洞标题 spring4shell-CVE-2022-22965: Spring Framework RCE via Data Binding on JDK 9+ 漏洞描述 A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to rem...
CVE-2015-7245: D-Link DVG-N5402SP – Local File Inclusion
漏洞标题 CVE-2015-7245: D-Link DVG-N5402SP - Local File Inclusion 漏洞描述 D-Link DVG-N5402SP is susceptible to local file inclusion in products with firmware W1000CN-00, W1000CN-0...
CVE-2023-30192: PrestaShop ‘possearchproducts’ <= 1.7 - SQL Injection
漏洞标题 CVE-2023-30192: PrestaShop 'possearchproducts' <= 1.7 - SQL Injection 漏洞描述 In the module “Search Products” (possearchproducts) from PosThemes for Presta...
CVE-2024-8698: Keycloak – SAML Core Package Signature Validation Flaw
漏洞标题 CVE-2024-8698: Keycloak - SAML Core Package Signature Validation Flaw 漏洞描述 A flaw exists in the SAML signature validation method within the Keycloak XMLSignatureUtil c...
CVE-2023-4450: JeecgBoot JimuReport – Template injection
漏洞标题 CVE-2023-4450: JeecgBoot JimuReport - Template injection 漏洞描述 A vulnerability was found in jeecgboot JimuReport up to 1.6.0. It has been declared as critical. Affected...
CVE-2023-4450: JeecgBoot JimuReport – Template injection
漏洞标题 CVE-2023-4450: JeecgBoot JimuReport - Template injection 漏洞描述 A vulnerability was found in jeecgboot JimuReport up to 1.6.0. It has been declared as critical. Affected...
CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 – SQL Injection
漏洞标题 CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 - SQL Injection 漏洞描述 WordPress Easy Digital Downloads plugin 3.1.0.2 and 3.1.0.3 contains a SQL inject...
CVE-2025-64446: FortiWeb – Authentication Bypass
漏洞标题 CVE-2025-64446: FortiWeb - Authentication Bypass 漏洞描述 A relative path traversal vulnerability in Fortinet FortiWeb 8.0.0 through 8.0.1, FortiWeb 7.6.0 through 7.6.4, F...

