





CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting
漏洞标题 CVE-2013-4625: WordPress Plugin Duplicator < 0.4.5 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in files/installer.cleanup.php in the Duplicator...
CVE-2024-3272: D-Link Network Attached Storage – Backdoor Account
漏洞标题 CVE-2024-3272: D-Link Network Attached Storage - Backdoor Account 漏洞描述 A vulnerability, which was classified as very critical, has been found in D-Link DNS-320L, DNS-3...
CVE-2022-35653: Moodle LTI module Reflected – Cross-Site Scripting
漏洞标题 CVE-2022-35653: Moodle LTI module Reflected - Cross-Site Scripting 漏洞描述 A reflected XSS issue was identified in the LTI module of Moodle. The vulnerability exists due ...
CVE-2023-30212: OURPHP <= 7.2.0 - Cross Site Scripting
漏洞标题 CVE-2023-30212: OURPHP <= 7.2.0 - Cross Site Scripting 漏洞描述 OURPHP <= 7.2.0 is vulnerale to Cross Site Scripting (XSS) via /client/manage/ourphp_out.php. PoC代码
CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
CVE-2021-4073: RegistrationMagic <= 5.0.1.7 - Authentication Bypass
漏洞标题 CVE-2021-4073: RegistrationMagic <= 5.0.1.7 - Authentication Bypass 漏洞描述 RegistrationMagic WordPress plugin versions <= 5.0.1.7 contain an authentication bypass ...
CVE-2020-27838: KeyCloak – Information Exposure
漏洞标题 CVE-2020-27838: KeyCloak - Information Exposure 漏洞描述 A flaw was found in keycloak in versions prior to 13.0.0. The client registration endpoint allows fetching informa...
CVE-2024-28200: N-able N-central < 2024.2 - Authentication Bypass Detection
漏洞标题 CVE-2024-28200: N-able N-central < 2024.2 - Authentication Bypass Detection 漏洞描述 N-central server versions prior to 2024.2 contain an authentication bypass in the u...
CVE-2022-1768: WordPress RSVPMaker <=9.3.2 - SQL Injection
漏洞标题 CVE-2022-1768: WordPress RSVPMaker <=9.3.2 - SQL Injection 漏洞描述 WordPress RSVPMaker plugin through 9.3.2 contains a SQL injection vulnerability due to insufficient ...
CVE-2010-5286: Joomla! Component Jstore – ‘Controller’ Local File Inclusion
漏洞标题 CVE-2010-5286: Joomla! Component Jstore - 'Controller' Local File Inclusion 漏洞描述 A directory traversal vulnerability in Jstore (com_jstore) component for Joo...
Linux实现DHCP服务器的搭建_Linux
Linux常见的服务器有几种,本文详细介绍了Linux实现DHCP服务器的搭建,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录一.基础知识:二.DHCP服务器的相...
CVE-2019-25141: Easy WP SMTP <= 1.3.9 - Missing Authorization to Arbitrary Options Update
漏洞标题 CVE-2019-25141: Easy WP SMTP <= 1.3.9 - Missing Authorization to Arbitrary Options Update 漏洞描述 The Easy WP SMTP plugin for WordPress is vulnerable to authorization ...
CVE-2018-2894: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2018-2894: Oracle WebLogic Server - Remote Code Execution 漏洞描述 The Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS - Web Services) ...
CVE-2024-3234: Chuanhu Chat – Directory Traversal
漏洞标题 CVE-2024-3234: Chuanhu Chat - Directory Traversal 漏洞描述 The gaizhenbiao/chuanhuchatgpt application is vulnerable to a path traversal attack due to its use of an outdate...
CVE-2022-26960: elFinder <=2.1.60 - Local File Inclusion
漏洞标题 CVE-2022-26960: elFinder <=2.1.60 - Local File Inclusion 漏洞描述 elFinder through 2.1.60 is affected by local file inclusion via connector.minimal.php. This allows una...
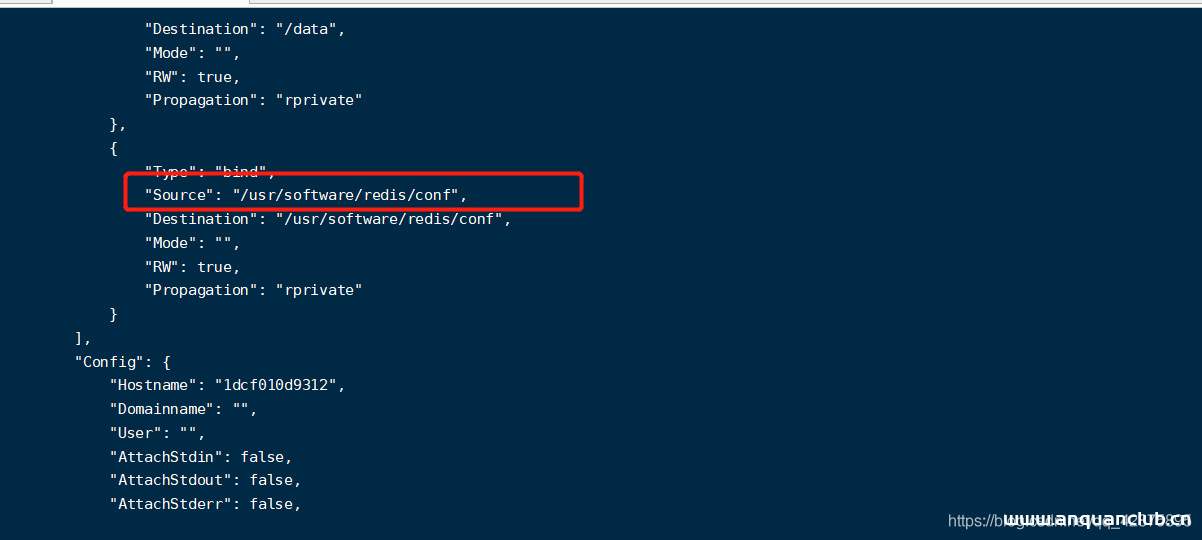
Docker常用命令详解_docker
这篇文章主要介绍了Docker常用命令详解,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 一. 帮助命令 1. 查看当前docker版本 docker version 2. ...

