






CVE-2018-20463: WordPress JSmol2WP <=1.07 - Local File Inclusion
漏洞标题 CVE-2018-20463: WordPress JSmol2WP <=1.07 - Local File Inclusion 漏洞描述 WordPress JSmol2WP plugin 1.07 is susceptible to local file inclusion via ../ directory traver...
CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure
漏洞标题 CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure 漏洞描述 WordPress WPS Hide Login plugin before 1.9.1 is susceptible to incorrect authorization...
CVE-2022-3477: WordPress tagDiv Composer < 3.5 - Authentication Bypass
漏洞标题 CVE-2022-3477: WordPress tagDiv Composer < 3.5 - Authentication Bypass 漏洞描述 The tagDiv Composer WordPress plugin before 3.5, required by the Newspaper WordPress the...
CVE-2019-7256: eMerge E3 1.00-06 – Remote Code Execution
漏洞标题 CVE-2019-7256: eMerge E3 1.00-06 - Remote Code Execution 漏洞描述 Linear eMerge E3-Series devices are susceptible to remote code execution vulnerabilities. PoC代码
CVE-2022-1933: WordPress CDI <5.1.9 - Cross Site Scripting
漏洞标题 CVE-2022-1933: WordPress CDI <5.1.9 - Cross Site Scripting 漏洞描述 WordPress CDI plugin prior to 5.1.9 contains a cross-site scripting vulnerability. The plugin does n...
CVE-2025-2747: Kentico Xperience 13 CMS – Staging Service Authentication Bypass (WT-2025-0006)
漏洞标题 CVE-2025-2747: Kentico Xperience 13 CMS - Staging Service Authentication Bypass (WT-2025-0006) 漏洞描述 An authentication bypass vulnerability in Kentico Xperience allows ...
CVE-2021-3019: ffay lanproxy Directory Traversal
漏洞标题 CVE-2021-3019: ffay lanproxy Directory Traversal 漏洞描述 ffay lanproxy 0.1 is susceptible to a directory traversal vulnerability that could let attackers read /../conf/co...
CVE-2021-37416: Zoho ManageEngine ADSelfService Plus <=6103 - Cross-Site Scripting
漏洞标题 CVE-2021-37416: Zoho ManageEngine ADSelfService Plus <=6103 - Cross-Site Scripting 漏洞描述 Zoho ManageEngine ADSelfService Plus 6103 and prior contains a reflected cro...
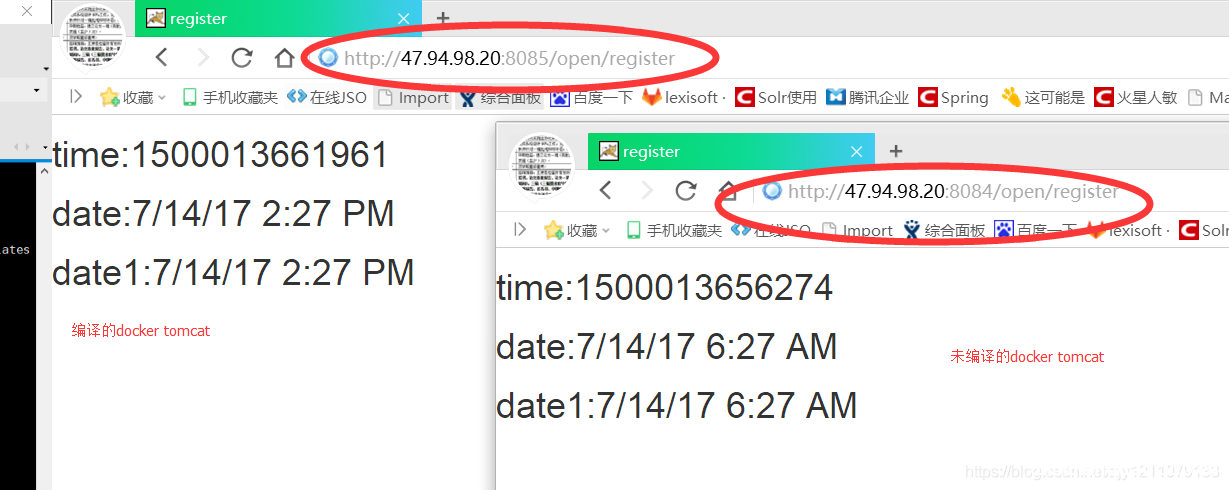
docker时区问题和迁移数据问题_docker
这篇文章主要介绍了docker时区问题和迁移数据问题,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 最新解决办法: ...
CVE-2018-20985: WordPress Payeezy Pay <=2.97 - Local File Inclusion
漏洞标题 CVE-2018-20985: WordPress Payeezy Pay <=2.97 - Local File Inclusion 漏洞描述 WordPress Plugin WP Payeezy Pay is prone to a local file inclusion vulnerability because it...
CVE-2017-17562: Embedthis GoAhead <3.6.5 - Remote Code Execution
漏洞标题 CVE-2017-17562: Embedthis GoAhead <3.6.5 - Remote Code Execution 漏洞描述 description: Embedthis GoAhead before 3.6.5 allows remote code execution if CGI is enabled and...
CVE-2019-16313: ifw8 Router ROM v4.31 – Credential Discovery
漏洞标题 CVE-2019-16313: ifw8 Router ROM v4.31 - Credential Discovery 漏洞描述 ifw8 Router ROM v4.31 is vulnerable to credential disclosure via action/usermanager.htm HTML source c...
CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation
漏洞标题 CVE-2024-2771: Contact Form Plugin by Fluent Forms < 5.1.17 - Unauthenticated Limited Privilege Escalation 漏洞描述 The plugin is vulnerable to privilege escalation due...
CVE-2025-11749: WordPress AI Engine Plugin – Token Exposure
漏洞标题 CVE-2025-11749: WordPress AI Engine Plugin - Token Exposure 漏洞描述 Unauthenticated sensitive information exposure in AI Engine WordPress plugin <= 3.1.3 exposes beare...
CVE-2023-2059: DedeCMS 5.7.87 – Directory Traversal
漏洞标题 CVE-2023-2059: DedeCMS 5.7.87 - Directory Traversal 漏洞描述 Directory traversal vulnerability in DedeCMS 5.7.87 allows reading sensitive files via the $activepath paramet...
CVE-2024-24328: TotoLink Router setMacFilterRules – Command Injection
漏洞标题 CVE-2024-24328: TotoLink Router setMacFilterRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vulner...

