





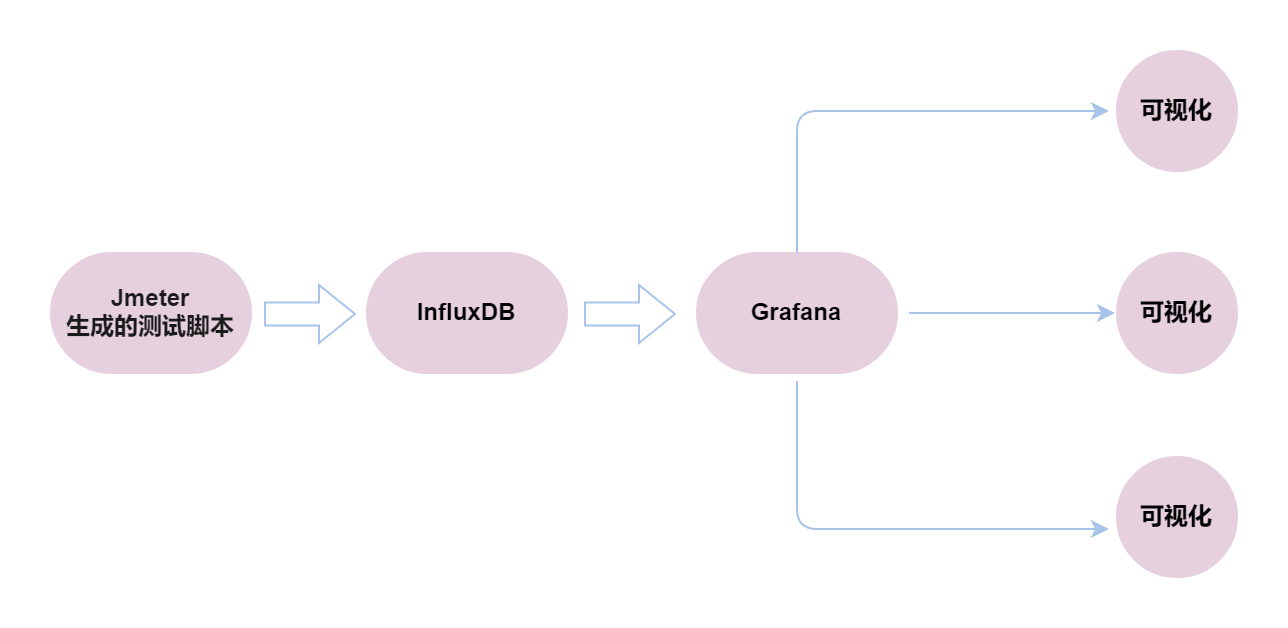
借助Docker搭建JMeter+Grafana+Influxdb监控平台的详细教程_docker
这篇文章主要介绍了借助Docker搭建JMeter+Grafana+Influxdb监控平台,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 我们都知道Jmeter提供了原生...
什么是 IP 冲突以及如何解决?
如果你曾经看到“Windows 检测到 IP 地址冲突”或“此网络上的另一台计算机具有相同的 IP 地址”消息,你可能想知道此警告的含义。虽然 IP 冲突问题通常不难解决,但它们令人困惑,尤其是对于那...

CVE-2015-7297: Joomla! Core SQL Injection
漏洞标题 CVE-2015-7297: Joomla! Core SQL Injection 漏洞描述 A SQL injection vulnerability in Joomla! 3.2 before 3.4.4 allows remote attackers to execute arbitrary SQL commands. PoC...
CVE-2018-1000129: Jolokia 1.3.7 – Cross-Site Scripting
漏洞标题 CVE-2018-1000129: Jolokia 1.3.7 - Cross-Site Scripting 漏洞描述 Jolokia 1.3.7 is vulnerable to cross-site scripting in the HTTP servlet and allows an attacker to execute m...
CVE-2021-44152: Reprise License Manager 14.2 – Authentication Bypass
漏洞标题 CVE-2021-44152: Reprise License Manager 14.2 - Authentication Bypass 漏洞描述 Reprise License Manager (RLM) 14.2 does not verify authentication or authorization and allows...
CVE-2023-4415: Ruijie RG-EW1200G Router Background – Login Bypass
漏洞标题 CVE-2023-4415: Ruijie RG-EW1200G Router Background - Login Bypass 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 07161417 r483. It has been rated as critical. Aff...
Citrix ADC and Citrix Gateway CVE-2023-3519未授权远程代码执行漏洞
漏洞标题 Citrix ADC and Citrix Gateway CVE-2023-3519未授权远程代码执行漏洞 漏洞描述 Citrix ADC and Citrix Gateway存在远程代码执行漏洞,此漏洞是由于缺乏有效的校验导致的。 PoC代码 暂...
CVE-2014-9614: Netsweeper 4.0.5 – Default Weak Account
漏洞标题 CVE-2014-9614: Netsweeper 4.0.5 - Default Weak Account 漏洞描述 The Web Panel in Netsweeper before 4.0.5 has a default password of 'branding' for the branding ac...
CVE-2024-33605: Sharp Multifunction Printers – Directory Listing
漏洞标题 CVE-2024-33605: Sharp Multifunction Printers - Directory Listing 漏洞描述 It was observed that Sharp printers are vulnerable to an arbitrary directory listing without auth...
CVE-2025-49002: DataEase 远程代码执行漏洞
漏洞标题 CVE-2025-49002: DataEase 远程代码执行漏洞 漏洞描述 CVE-2025-49002 是由于H2数据库模块没有严格过滤用户输入的JDBC连接参数,可使用大小写绕过补丁。攻击者可利用这些漏洞实现未授...
CVE-2021-42013: Apache 2.4.49/2.4.50 – Path Traversal and Remote Code Execution
漏洞标题 CVE-2021-42013: Apache 2.4.49/2.4.50 - Path Traversal and Remote Code Execution 漏洞描述 A flaw was found in a change made to path normalization in Apache HTTP Server 2.4....
CVE-2020-5284: Next.js .next limited path traversal
漏洞标题 CVE-2020-5284: Next.js .next limited path traversal 漏洞描述 前端目录遍历浏览 fofa: "Next.js" PoC代码
Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 – 1
漏洞标题 Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 - 1 漏洞描述 Citrix ADC and Gateway CVE-2023-4966 信息泄露漏洞 - 1 日期: 2024-02-07 | 影响软件: Citrix ADC | PoC代码 暂无
CVE-2018-15535: Responsive FileManager <9.13.4 - Local File Inclusion
漏洞标题 CVE-2018-15535: Responsive FileManager <9.13.4 - Local File Inclusion 漏洞描述 Responsive FileManager before version 9.13.4 is vulnerable to local file inclusion via fi...
CVE-2024-33610: Sharp Multifunction Printers – Cookie Exposure
漏洞标题 CVE-2024-33610: Sharp Multifunction Printers - Cookie Exposure 漏洞描述 It was observed that Sharp printers are vulnerable to a listing of session cookies without authenti...
CVE-2019-10758: mongo-express Remote Code Execution
漏洞标题 CVE-2019-10758: mongo-express Remote Code Execution 漏洞描述 mongo-express before 0.54.0 is vulnerable to remote code execution via endpoints that uses the `toBSON` method...

