





CVE-2022-1391: WordPress Cab fare calculator < 1.0.4 - Local File Inclusion
漏洞标题 CVE-2022-1391: WordPress Cab fare calculator < 1.0.4 - Local File Inclusion 漏洞描述 The Cab fare calculator WordPress plugin before 1.0.4 does not validate the control...
CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names
漏洞标题 CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when process...
CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names
漏洞标题 CVE-2005-0850: FileZilla Server < 0.9.6 - DoS via MS-DOS Device Names 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when process...
CVE-2005-3634: SAP Web Application Server 6.x/7.0 – Open Redirect
漏洞标题 CVE-2005-3634: SAP Web Application Server 6.x/7.0 - Open Redirect 漏洞描述 frameset.htm in the BSP runtime in SAP Web Application Server (WAS) 6.10 through 7.00 allows rem...
CVE-2005-3634: SAP Web Application Server 6.x/7.0 – Open Redirect
漏洞标题 CVE-2005-3634: SAP Web Application Server 6.x/7.0 - Open Redirect 漏洞描述 frameset.htm in the BSP runtime in SAP Web Application Server (WAS) 6.10 through 7.00 allows rem...
CVE-2022-2551: WordPress Duplicator <1.4.7 - Authentication Bypass
漏洞标题 CVE-2022-2551: WordPress Duplicator <1.4.7 - Authentication Bypass 漏洞描述 WordPress Duplicator plugin before 1.4.7 is susceptible to authentication bypass. The plugin...
CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection
漏洞标题 CVE-2022-33965: WordPress Visitor Statistics <=5.7 - SQL Injection 漏洞描述 WordPress Visitor Statistics plugin through 5.7 contains multiple unauthenticated SQL inject...

CVE-2022-4375: Mingsoft MCMS – SQL Injection
漏洞标题 CVE-2022-4375: Mingsoft MCMS - SQL Injection 漏洞描述 SQL injection vulnerability in Mingsoft MCMS up to 5.2.9 via the sqlWhere parameter in /cms/category/list. PoC代码
CVE-2020-26214: Alerta < 8.1.0 - Authentication Bypass
漏洞标题 CVE-2020-26214: Alerta < 8.1.0 - Authentication Bypass 漏洞描述 Alerta prior to version 8.1.0 is prone to authentication bypass when using LDAP as an authorization prov...
CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
漏洞标题 CVE-2025-4322: Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover 漏洞描述 The Motors theme for WordPress is vulnerable to pri...
欧盟数据主管命令欧洲刑警组织删除与犯罪无关的个人数据
根据欧盟数据保护监管机构EDPS于1月10日发布的新闻稿,EDPS已于一周前下令欧洲刑警组织删除与犯罪活动没有明确关联的个人的数据,以减少对公民个人权力和自由的侵犯。 此前,欧洲刑警组织...
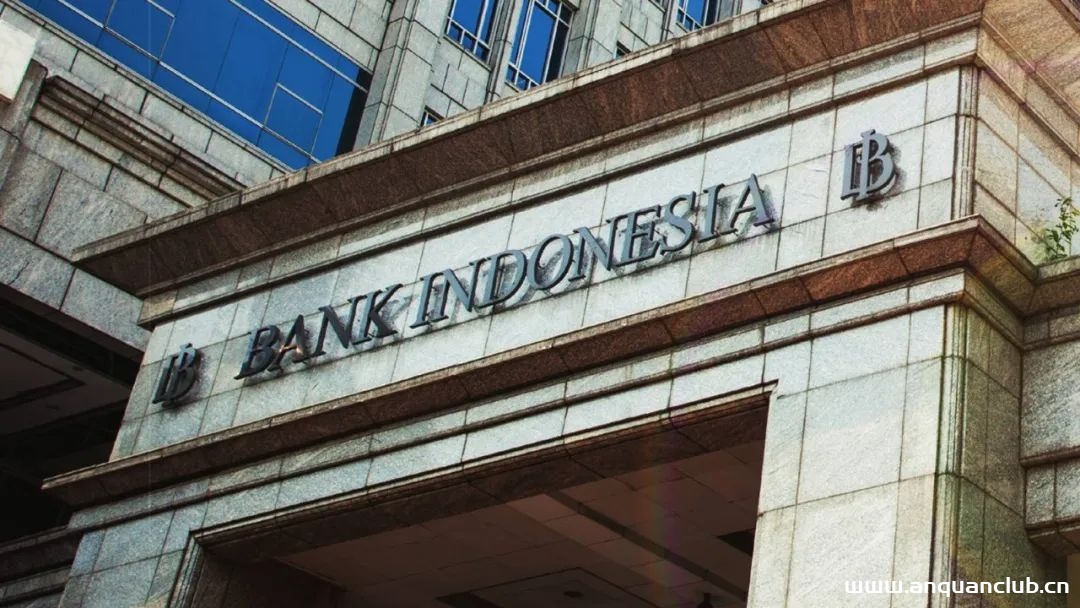
印尼央行确认遭受勒索软件攻击
1月20日,印度尼西亚共和国中央银行——印度尼西亚银行(BANK INDONESIA)通信部执行主任Erwin Haryono证实,银行于上个月遭受了勒索软件攻击。中央银行有着管理货币部门、维持支付系统和金融系...

