




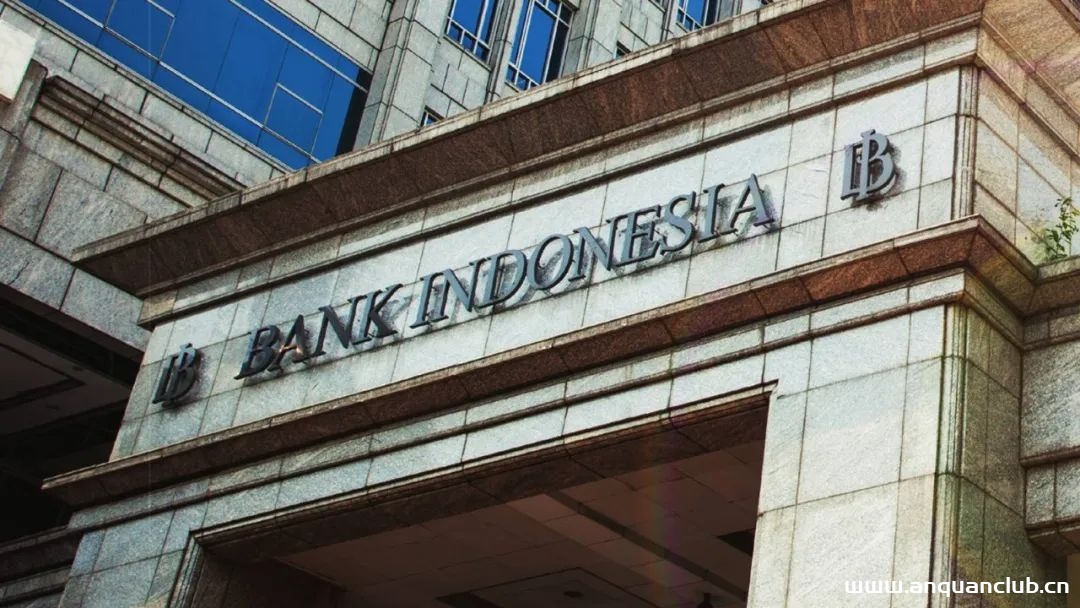
印尼央行确认遭受勒索软件攻击
1月20日,印度尼西亚共和国中央银行——印度尼西亚银行(BANK INDONESIA)通信部执行主任Erwin Haryono证实,银行于上个月遭受了勒索软件攻击。中央银行有着管理货币部门、维持支付系统和金融系...
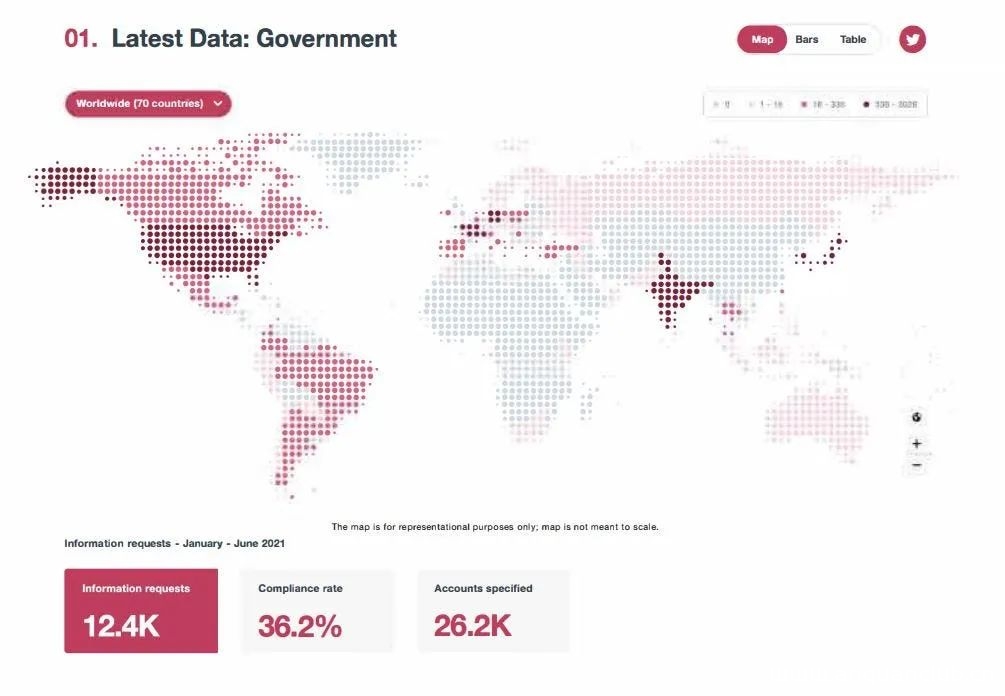
推特透明度报告:美国政府索要的信息最多
1月25日,推特Twitter透明度中心公布了一份透明度报告,以让用户了解世界范围内各国政府向他们提出的要求。 推特认为透明度有利于保护持续受到威胁的开放互联网,并且对于追究公司和政府的...
恶意软件开发者公布密钥并宣布退出江湖
近日,一位名为“Topleak”的用户在BleepingComputer论坛上发布了一个引人注目的帖子,其自称是Maze、Egregor、Sekhmet恶意软件开发者,表示决定向公众发布Maze、Egregor、Sekhmet勒索软件家族...

CVE-2025-4009: Evertz SDVN 3080ipx-10G – Unauthenticated Arbitrary Command Injection
漏洞标题 CVE-2025-4009: Evertz SDVN 3080ipx-10G - Unauthenticated Arbitrary Command Injection 漏洞描述 The Evertz SDVN 3080ipx-10G is a High Bandwidth Ethernet Switching Fabric for...
CVE-2025-51501: Microweber CMS2.0 – Cross-Site Scripting
漏洞标题 CVE-2025-51501: Microweber CMS2.0 - Cross-Site Scripting 漏洞描述 Reflected Cross-Site Scripting (XSS) in the `id` parameter of the `live_edit.module_settings` API endpoin...
CVE-2025-26793: FREEDOM Administration – Default Login
漏洞标题 CVE-2025-26793: FREEDOM Administration - Default Login 漏洞描述 The Web GUI configuration panel of Hirsch (formerly Identiv and Viscount) Enterphone MESH through 2024 ship...
CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
CVE-2025-34085: WordPress Simple File List <=4.2.2 - Remote Code Execution
漏洞标题 CVE-2025-34085: WordPress Simple File List <=4.2.2 - Remote Code Execution 漏洞描述 An unrestricted file upload vulnerability in the WordPress Simple File List plugin b...
CVE-2000-0760: Jakarta Tomcat 3.1 and 3.0 – Information Disclosure
漏洞标题 CVE-2000-0760: Jakarta Tomcat 3.1 and 3.0 - Information Disclosure 漏洞描述 Jakarta Tomcat 3.1 and 3.0 under Apache contain a vulnerability in the Snoop servlet that revea...
CVE-2025-40630: IceWarp Mail Server ≤11.4.0 – Open Redirect
漏洞标题 CVE-2025-40630: IceWarp Mail Server ≤11.4.0 - Open Redirect 漏洞描述 IceWarp Mail Server version 11.4.0 and below contains an open redirect vulnerability that allows atta...
CVE-2025-40630: IceWarp Mail Server ≤11.4.0 – Open Redirect
漏洞标题 CVE-2025-40630: IceWarp Mail Server ≤11.4.0 - Open Redirect 漏洞描述 IceWarp Mail Server version 11.4.0 and below contains an open redirect vulnerability that allows atta...
CVE-2025-25231: Omnissa Workspace ONE UEM – Path Traversal
漏洞标题 CVE-2025-25231: Omnissa Workspace ONE UEM - Path Traversal 漏洞描述 Omnissa Workspace ONE UEM contains a path traversal caused by crafted GET requests to restricted API en...
CVE-2025-34031: Moodle Jmol Filter 6.1 – Local File Inclusion
漏洞标题 CVE-2025-34031: Moodle Jmol Filter 6.1 - Local File Inclusion 漏洞描述 Moodle Jmol Filter 6.1 is vulnerable to local file inclusion through the jsmol.php file, allowing at...
CVE-2025-2748: Kentico Xperience CMS – Unauthenticated Stored XSS
漏洞标题 CVE-2025-2748: Kentico Xperience CMS - Unauthenticated Stored XSS 漏洞描述 The Kentico Xperience application does not fully validate or filter files uploaded via the multi...
CVE-2025-34045: WeiPHP 5.0 – Path Traversal
漏洞标题 CVE-2025-34045: WeiPHP 5.0 - Path Traversal 漏洞描述 WeiPHP 5.0 contains a path traversal caused by insufficient input validation of the picUrl parameter in /public/index....
CVE-2025-34040: Zhiyuan OA Platform – Arbitrary File Upload
漏洞标题 CVE-2025-34040: Zhiyuan OA Platform - Arbitrary File Upload 漏洞描述 An arbitrary file upload vulnerability exists in the Zhiyuan OA platform 5.0, 5.1 - 5.6sp1, 6.0 - 6.1s...

