




Docker+selenium实现自动化健康报备的方法_docker
这篇文章主要介绍了Docker+selenium实现自动化健康报备的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 本文...

CVE-2025-6970: WordPress Events Manager <= 7.0.3 - SQL Injection
漏洞标题 CVE-2025-6970: WordPress Events Manager <= 7.0.3 - SQL Injection 漏洞描述 The Events Manager - Calendar, Bookings, Tickets, and more! plugin for WordPress is vulnerable...
CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) – Authentication Bypass
漏洞标题 CVE-2023-35078: Ivanti Endpoint Manager Mobile (EPMM) - Authentication Bypass 漏洞描述 Ivanti Endpoint Manager Mobile (EPMM), formerly MobileIron Core, through 11.10 allow...


Spring Boot 打包上传Docker 仓库的详细步骤_docker
这篇文章主要介绍了Spring Boot 打包上传Docker 仓库的详细步骤,本文分步骤给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 重要提示:学习本文之前需...
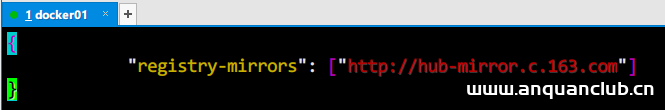
Docker 使用国内镜像仓库的方法_docker
这篇文章主要介绍了Docker 使用国内镜像仓库的方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 1、问题描述 由...
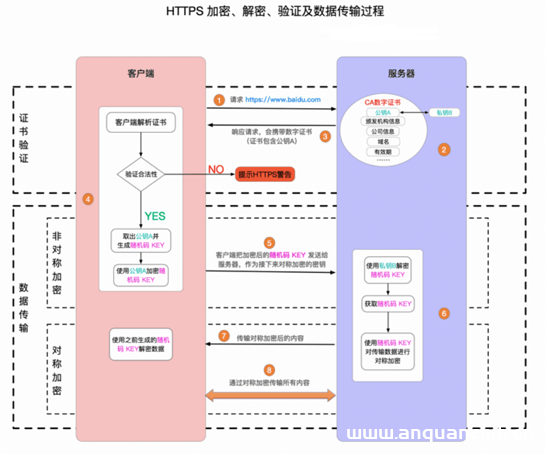
基于Nginx实现HTTPS网站设置的步骤_nginx
本文主要介绍了Nginx实现HTTPS网站设置的步骤,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录前言:加密算法:一、HTTPS 简介二、Nginx 实现 HTTPS ...
CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion
漏洞标题 CVE-2021-39316: WordPress DZS Zoomsounds <=6.50 - Local File Inclusion 漏洞描述 WordPress Zoomsounds plugin 6.45 and earlier allows arbitrary files, including sensitive...
CVE-2025-47445: WordPress Eventin (Themewinter) ≤ 4.0.26 – Arbitrary File Download
漏洞标题 CVE-2025-47445: WordPress Eventin (Themewinter) ≤ 4.0.26 - Arbitrary File Download 漏洞描述 Themewinter Eventin contains a path traversal caused by relative path manipula...
CVE-2025-28367: mojoPortal <=2.9.0.1 - Directory Traversal
漏洞标题 CVE-2025-28367: mojoPortal <=2.9.0.1 - Directory Traversal 漏洞描述 mojoPortal <=2.9.0.1 is vulnerable to Directory Traversal via BetterImageGallery API Controller -...
CVE-2018-20462: WordPress JSmol2WP <=1.07 - Cross-Site Scripting
漏洞标题 CVE-2018-20462: WordPress JSmol2WP <=1.07 - Cross-Site Scripting 漏洞描述 WordPress JSmol2WP version 1.07 and earlier is vulnerable to cross-site scripting and allows r...
CVE-2025-53118: Securden Unified PAM – Authentication Bypass
漏洞标题 CVE-2025-53118: Securden Unified PAM - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists which allows an unauthenticated attacker to control adm...
CVE-2023-33629: H3C Magic R300-2100M – Remote Code Execution
漏洞标题 CVE-2023-33629: H3C Magic R300-2100M - Remote Code Execution 漏洞描述 H3C Magic R300 version R300-2100MV100R004 was discovered to contain a stack overflow via the Deltrigg...
CVE-2017-18487: AdPush < 1.44 - Cross-Site Scripting
漏洞标题 CVE-2017-18487: AdPush < 1.44 - Cross-Site Scripting 漏洞描述 The adsense-plugin (aka Google AdSense) plugin before 1.44 for WordPress has multiple XSS issues. PoC代码
CVE-2014-8799: WordPress Plugin DukaPress 2.5.2 – Directory Traversal
漏洞标题 CVE-2014-8799: WordPress Plugin DukaPress 2.5.2 - Directory Traversal 漏洞描述 A directory traversal vulnerability in the dp_img_resize function in php/dp-functions.php in...
CVE-2019-8086: Adobe Experience Manager – XML External Entity Injection
漏洞标题 CVE-2019-8086: Adobe Experience Manager - XML External Entity Injection 漏洞描述 Adobe Experience Manager 6.5, 6.4, 6.3 and 6.2 are susceptible to XML external entity inje...

