





CVE-2023-25573: Metersphere – Arbitrary File Read
漏洞标题 CVE-2023-25573: Metersphere - Arbitrary File Read 漏洞描述 Metersphere is an open source continuous testing platform. In affected versions an improper access control vulne...
CVE-2011-4804: Joomla! Component com_kp – ‘Controller’ Local File Inclusion
漏洞标题 CVE-2011-4804: Joomla! Component com_kp - 'Controller' Local File Inclusion 漏洞描述 A directory traversal vulnerability in the obSuggest (com_obsuggest) compone...
CVE-2022-35413: WAPPLES Web Application Firewall <=6.0 - Hardcoded Credentials
漏洞标题 CVE-2022-35413: WAPPLES Web Application Firewall <=6.0 - Hardcoded Credentials 漏洞描述 WAPPLES Web Application Firewall through 6.0 contains a hardcoded credentials vu...
CVE-2023-46574: TOTOLINK A3700R – Command Injection
漏洞标题 CVE-2023-46574: TOTOLINK A3700R - Command Injection 漏洞描述 An issue in TOTOLINK A3700R v.9.1.2u.6165_20211012 allows a remote attacker to execute arbitrary code via the ...
CVE-2020-2551: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2020-2551: Oracle WebLogic Server - Remote Code Execution 漏洞描述 Oracle WebLogic Server (Oracle Fusion Middleware (component: WLS Core Components) is susceptible to ...

CVE-2022-2627: WordPress Newspaper < 12 - Cross-Site Scripting
漏洞标题 CVE-2022-2627: WordPress Newspaper < 12 - Cross-Site Scripting 漏洞描述 WordPress Newspaper theme before 12 is susceptible to cross-site scripting. The does not sanitiz...
CVE-2010-1302: Joomla! Component DW Graph – Local File Inclusion
漏洞标题 CVE-2010-1302: Joomla! Component DW Graph - Local File Inclusion 漏洞描述 A directory traversal vulnerability in dwgraphs.php in the DecryptWeb DW Graphs (com_dwgraphs) co...
CVE-2018-16716: NCBI ToolBox – Directory Traversal
漏洞标题 CVE-2018-16716: NCBI ToolBox - Directory Traversal 漏洞描述 NCBI ToolBox 2.0.7 through 2.2.26 legacy versions contain a path traversal vulnerability via viewcgi.cgi which ...
CVE-2020-22208: 74cms – ajax_street.php ‘x’ SQL Injection
漏洞标题 CVE-2020-22208: 74cms - ajax_street.php 'x' SQL Injection 漏洞描述 SQL Injection in 74cms 3.2.0 via the x parameter to plus/ajax_street.php. PoC代码
Linux磁盘空间释放问题整理_Linux
在本篇文章里小编给大家分享了一篇关于Linux磁盘空间释放问题整理内容,有需要的朋友们可以学习参考下。 IDC里的一台服务器的/分区使用率爆满了!已达到100%!经查看发现有个文件过大(80G),...
CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export
漏洞标题 CVE-2019-17228: Motors Car Dealer & Classified Ads <= 1.4.0 - Unauthenticated settings import/export 漏洞描述 includes/options.php in the motors-car-dealership-clas...
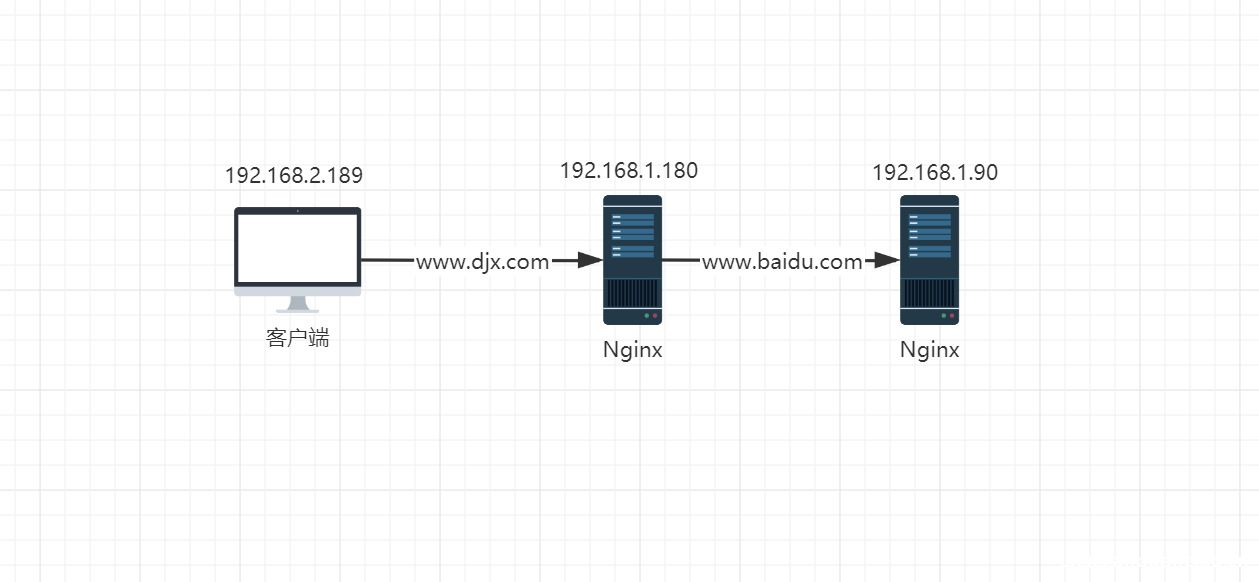
解决Nginx 配置 proxy_pass 后 返回404问题_nginx
这篇文章主要介绍了Nginx 配置 proxy_pass 后 返回404问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、 Nginx 配置 proxy_pass 后 返...
CVE-2025-5605: WSO2 Management Console – Authentication Bypass
漏洞标题 CVE-2025-5605: WSO2 Management Console - Authentication Bypass 漏洞描述 An authentication bypass vulnerability exists in the Management Console of multiple WSO2 products. ...
CVE-2019-25152: Abandoned Cart Lite for WooCommerce < 5.2.0 - Cross-Site Scripting
漏洞标题 CVE-2019-25152: Abandoned Cart Lite for WooCommerce < 5.2.0 - Cross-Site Scripting 漏洞描述 The Abandoned Cart Lite for WooCommerce and Abandoned Cart Pro for WooCommer...
CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting
漏洞标题 CVE-2018-11709: WordPress wpForo Forum <= 1.4.11 - Cross-Site Scripting 漏洞描述 WordPress wpForo Forum plugin before 1.4.12 for WordPress allows unauthenticated reflec...

