





CVE-2025-5086: Dassault Systèmes DELMIA Apriso (up to 2025) – Insecure Deserialization
漏洞标题 CVE-2025-5086: Dassault Systèmes DELMIA Apriso (up to 2025) - Insecure Deserialization 漏洞描述 A deserialization of untrusted data vulnerability affecting DELMIA Apriso ...
CVE-2023-3846: MooDating 1.2 – Cross-Site Scripting
漏洞标题 CVE-2023-3846: MooDating 1.2 - Cross-Site Scripting 漏洞描述 A vulnerability classified as problematic has been found in mooSocial mooDating 1.2. This affects an unknown p...
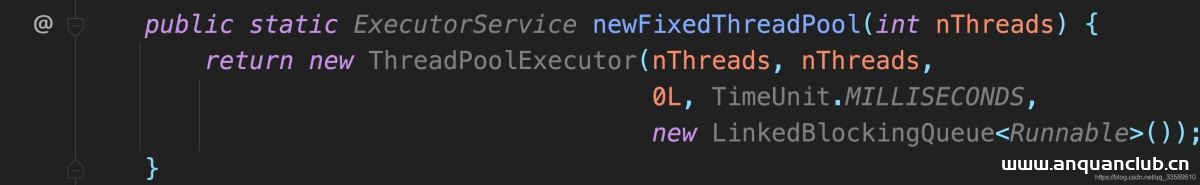
Tomcat修正JDK原生线程池bug的实现原理_Tomcat
这篇文章主要介绍了Tomcat是如何修正JDK原生线程池bug的,本文通过实例代码给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 为提高处理能力和并发度,We...
CVE-2025-49029: WordPress Custom Login And Signup Widget Plugin <= 1.0 - Arbitrary Code Execution
漏洞标题 CVE-2025-49029: WordPress Custom Login And Signup Widget Plugin <= 1.0 - Arbitrary Code Execution 漏洞描述 Improper Control of Generation of Code ('Code Injection&...
CVE-2010-1534: Joomla! Component Shoutbox Pro – Local File Inclusion
漏洞标题 CVE-2010-1534: Joomla! Component Shoutbox Pro - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Shoutbox Pro (com_shoutbox) component for Joomla! ...
CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 – Information Disclosure
漏洞标题 CVE-2020-2733: JD Edwards EnterpriseOne Tools 9.2 - Information Disclosure 漏洞描述 JD Edwards EnterpriseOne Tools 9.2 is susceptible to information disclosure via the Mon...
CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 – Directory Traversal
漏洞标题 CVE-2013-7240: WordPress Plugin Advanced Dewplayer 1.2 - Directory Traversal 漏洞描述 A directory traversal vulnerability in download-file.php in the Advanced Dewplayer pl...
CVE-2022-24260: VoipMonitor – Pre-Auth SQL Injection
漏洞标题 CVE-2022-24260: VoipMonitor - Pre-Auth SQL Injection 漏洞描述 A SQL injection vulnerability in Voipmonitor GUI before v24.96 allows attackers to escalate privileges to the...
CVE-2023-4169: Ruijie RG-EW1200G Router – Password Reset
漏洞标题 CVE-2023-4169: Ruijie RG-EW1200G Router - Password Reset 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 1.0(1)B1P5. It has been declared as critical. Affected by ...
CVE-2015-1579: WordPress Slider Revolution – Local File Disclosure
漏洞标题 CVE-2015-1579: WordPress Slider Revolution - Local File Disclosure 漏洞描述 Directory traversal vulnerability in the Elegant Themes Divi theme for WordPress allows remote ...
CVE-2022-26585: Mingsoft MCMS v5.2.7 – SQL Injection
漏洞标题 CVE-2022-26585: Mingsoft MCMS v5.2.7 - SQL Injection 漏洞描述 Mingsoft MCMS v5.2.7 contains an SQL injection vulnerability via /cms/content/list that allows unauthenticate...
CVE-2020-14750: Oracle WebLogic Server – Remote Command Execution
漏洞标题 CVE-2020-14750: Oracle WebLogic Server - Remote Command Execution 漏洞描述 Oracle WebLogic Server 10.3.6.0.0, 12.1.3.0.0, 12.2.1.3.0, 12.2.1.4.0 and 14.1.1.0.0 is suscepti...
CVE-2024-41713: MitelMiCollab 身份绕过导致任意文件读取漏洞
漏洞标题 CVE-2024-41713: MitelMiCollab 身份绕过导致任意文件读取漏洞 漏洞描述 Mitel MiCollab 是一个企业协作平台,它将各种通信工具整合到一个应用程序中,提供语音和视频通话、消息传递、...
CVE-2025-61884: Oracle E-Business Suite – Server-Side Request Forgery
漏洞标题 CVE-2025-61884: Oracle E-Business Suite - Server-Side Request Forgery 漏洞描述 Vulnerability in the Oracle Configurator product of Oracle E-Business Suite (component: Runt...
CVE-2011-2523: VSFTPD 2.3.4 – Backdoor Command Execution
漏洞标题 CVE-2011-2523: VSFTPD 2.3.4 - Backdoor Command Execution 漏洞描述 VSFTPD v2.3.4 had a serious backdoor vulnerability allowing attackers to execute arbitrary commands on th...
CVE-2024-38653: Ivanti Avalanche SmartDeviceServer – XML External Entity
漏洞标题 CVE-2024-38653: Ivanti Avalanche SmartDeviceServer - XML External Entity 漏洞描述 XXE in SmartDeviceServer in Ivanti Avalanche 6.3.1 allows a remote unauthenticated attack...

