





Linux下安装jdk包含卸载OpenJDK介绍_Linux
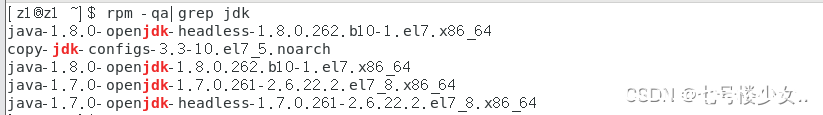
大家好,本篇文章主要讲的是Linux下安装jdk包含卸载OpenJDK介绍,感兴趣的同学赶快来看一看吧,对你有帮助的话记得收藏一下,方便下次浏览 1.查看openjdk rpm -qa|grep jdk 2.删除openjdk(rpm...

CVE-2025-62522: Vite – Information Disclosure
漏洞标题 CVE-2025-62522: Vite - Information Disclosure 漏洞描述 Vite is a frontend tooling framework for JavaScript.In versions from 2.9.18 to before 3.0.0, 3.2.9 to before 4.0.0, ...
CVE-2018-10736: Nagios XI SQL Inject
漏洞标题 CVE-2018-10736: Nagios XI SQL Inject 漏洞描述 Nagios XI SQL Inject PoC代码
CVE-2022-34305: Apache Tomcat Examples Web Application – Cross-Site Scripting
漏洞标题 CVE-2022-34305: Apache Tomcat Examples Web Application - Cross-Site Scripting 漏洞描述 Apache Tomcat 8.5.50 to 8.5.81, 9.0.30 to 9.0.64, 10.0.0-M1 to 10.0.22, and 10.1.0-M...

bugbounty技巧聚合20211112
漏洞报告 【Judge.me 】The response shows the nginx version http://hackerone.com/reports/1395068 【Slack 250刀】Cross-site leak allows attacker to de-anonymize members of his team f...
CVE-2022-25481: ThinkPHP 5.0.24 – Information Disclosure
漏洞标题 CVE-2022-25481: ThinkPHP 5.0.24 - Information Disclosure 漏洞描述 ThinkPHP 5.0.24 is susceptible to information disclosure. This version was configured without the PATHINF...
解决docker挂载的目录无法读写问题_docker
这篇文章主要介绍了解决docker挂载的目录无法读写问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 使用下面的命令可以创建一个容器并且把本地的/home/dock/Downloads目...
CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call
漏洞标题 CVE-2022-1020: WordPress WooCommerce <3.1.2 - Arbitrary Function Call 漏洞描述 WordPress WooCommerce plugin before 3.1.2 does not have authorisation and CSRF checks in ...
(CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞
漏洞标题 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 漏洞描述 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 PoC代码 暂无
CVE-2022-0760: WordPress Simple Link Directory <7.7.2 - SQL injection
漏洞标题 CVE-2022-0760: WordPress Simple Link Directory <7.7.2 - SQL injection 漏洞描述 WordPress Simple Link Directory plugin before 7.7.2 contains a SQL injection vulnerabilit...
CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion
漏洞标题 CVE-2023-5815: News & Blog Designer Pack – WordPress Blog Plugin <= 3.4.1 - Unauthenticated Local File Inclusion 漏洞描述 The News & Blog Designer Pack WordPre...
CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 – SQL Injection
漏洞标题 CVE-2018-6605: Joomla! Component Zh BaiduMap 3.0.0.1 - SQL Injection 漏洞描述 SQL Injection exists in the Zh BaiduMap 3.0.0.1 component for Joomla! via the id parameter in...
CVE-2022-26148: Grafana & Zabbix Integration – Credentials Disclosure
漏洞标题 CVE-2022-26148: Grafana & Zabbix Integration - Credentials Disclosure 漏洞描述 Grafana through 7.3.4, when integrated with Zabbix, contains a credential disclosure vul...
CVE-2023-30210: OURPHP <= 7.2.0 - Cross Site Scripting
漏洞标题 CVE-2023-30210: OURPHP <= 7.2.0 - Cross Site Scripting 漏洞描述 OURPHP <= 7.2.0 is vulnerable to Cross Site Scripting (XSS) via /client/manage/ourphp_tz.php. PoC代码
CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection
漏洞标题 CVE-2024-5057: WordPress Easy Digital Downloads <= 3.2.12 - SQL Injection 漏洞描述 Improper Neutralization of Special Elements used in an SQL Command ('SQL Injecti...
CVE-2022-43165: Rukovoditel <= 3.2.1 - Cross Site Scripting
漏洞标题 CVE-2022-43165: Rukovoditel <= 3.2.1 - Cross Site Scripting 漏洞描述 A stored cross-site scripting (XSS) vulnerability in the Global Variables feature (/index.php?modul...

