






CVE-2018-10736: Nagios XI SQL Inject
漏洞标题 CVE-2018-10736: Nagios XI SQL Inject 漏洞描述 Nagios XI SQL Inject PoC代码
CVE-2023-5244: Microweber < V.2.0 - Cross-Site Scripting
漏洞标题 CVE-2023-5244: Microweber < V.2.0 - Cross-Site Scripting 漏洞描述 Reflected Cross-Site Scripting Vulnerability in types GET parameter on the /editor_tools/rte_image_edi...
CVE-2017-14186: FortiGate FortiOS SSL VPN Web Portal – Cross-Site Scripting
漏洞标题 CVE-2017-14186: FortiGate FortiOS SSL VPN Web Portal - Cross-Site Scripting 漏洞描述 FortiGate FortiOS through SSL VPN Web Portal contains a cross-site scripting vulnerabi...
CVE-2023-39120: Nodogsplash – Directory Traversal
漏洞标题 CVE-2023-39120: Nodogsplash - Directory Traversal 漏洞描述 Nodogsplash product was affected by a directory traversal vulnerability that also impacted the OpenWrt product. ...
CVE-2020-0618: Microsoft SQL Server Reporting Services – Remote Code Execution
漏洞标题 CVE-2020-0618: Microsoft SQL Server Reporting Services - Remote Code Execution 漏洞描述 Microsoft SQL Server Reporting Services is vulnerable to a remote code execution vu...
CVE-2023-27638: tshirtecommerce PrestaShop Module – SQL Injection
漏洞标题 CVE-2023-27638: tshirtecommerce PrestaShop Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via the...
CVE-2020-24949: PHP-Fusion 9.03.50 – Remote Code Execution
漏洞标题 CVE-2020-24949: PHP-Fusion 9.03.50 - Remote Code Execution 漏洞描述 PHP-Fusion 9.03.50 downloads/downloads.php allows an authenticated user (not admin) to send a crafted r...
CVE-2020-24949: PHP-Fusion 9.03.50 – Remote Code Execution
漏洞标题 CVE-2020-24949: PHP-Fusion 9.03.50 - Remote Code Execution 漏洞描述 PHP-Fusion 9.03.50 downloads/downloads.php allows an authenticated user (not admin) to send a crafted r...
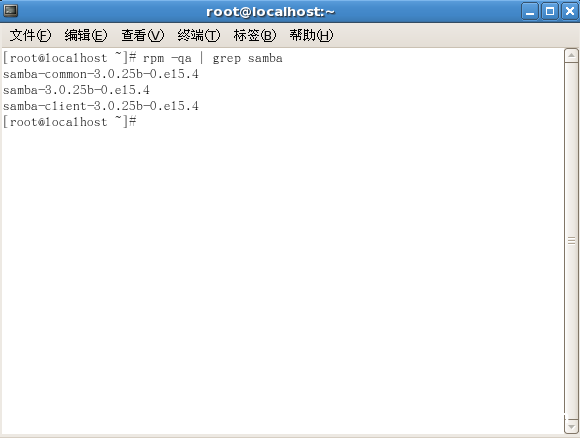
Linux Samba服务器超详细安装配置(附问题解决)_Linux
在嵌入式系统开发应用平台中,tftp、nfs和samba服务器是最常用的文件传输工具,本文详细的介绍一下Linux Samba服务器安装配置,感兴趣的可以了解一下 目录Samba服务器介绍Samba服务器组件Samba...
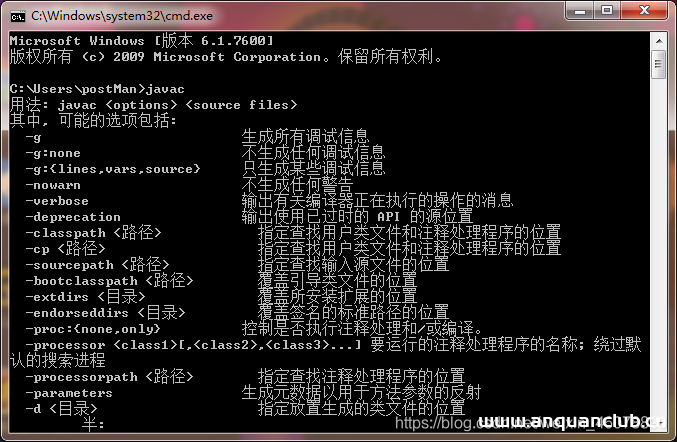
详解Tomcat双击startup.bat闪退的解决方法_Tomcat
这篇文章主要介绍了详解Tomcat双击startup.bat闪退的解决方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 作为...
CVE-2017-14135: OpenDreambox 2.0.0 – Remote Code Execution
漏洞标题 CVE-2017-14135: OpenDreambox 2.0.0 - Remote Code Execution 漏洞描述 OpenDreambox 2.0.0 is susceptible to remote code execution via the webadmin plugin. Remote attackers ca...
CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting
漏洞标题 CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting 漏洞描述 The plugin does not properly validate uploaded files allowing for the uploading of SVGs containing m...
CVE-2023-0527: Online Security Guards Hiring System – Cross-Site Scripting
漏洞标题 CVE-2023-0527: Online Security Guards Hiring System - Cross-Site Scripting 漏洞描述 A vulnerability was found in PHPGurukul Online Security Guards Hiring System 1.0 and cl...
CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass
漏洞标题 CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass 漏洞描述 Kubernetes Dashboard before 1.10.1 allows attackers to bypass authentication and use Dashb...
CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting
漏洞标题 CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting 漏洞描述 In Nagios XI before 5.8.6, XSS exists in the dashboard page (/dashboards/#) when administrative users ...
CVE-2021-25297: Nagios 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25297: Nagios 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command injection...

