





CVE-2017-3131: FortiOS 5.4.0 to 5.6.0 – Cross-Site Scripting
漏洞标题 CVE-2017-3131: FortiOS 5.4.0 to 5.6.0 - Cross-Site Scripting 漏洞描述 A Cross-Site Scripting vulnerability in Fortinet FortiOS versions 5.4.0 through 5.4.4 and 5.6.0 allow...
CVE-2023-38433: Fujitsu IP Series – Hardcoded Credentials
漏洞标题 CVE-2023-38433: Fujitsu IP Series - Hardcoded Credentials 漏洞描述 Fujitsu Real-time Video Transmission Gear “IP series” use hard-coded credentials, which may allow a re...
CVE-2018-10736: Nagios XI SQL Inject
漏洞标题 CVE-2018-10736: Nagios XI SQL Inject 漏洞描述 Nagios XI SQL Inject PoC代码
CVE-2023-39120: Nodogsplash – Directory Traversal
漏洞标题 CVE-2023-39120: Nodogsplash - Directory Traversal 漏洞描述 Nodogsplash product was affected by a directory traversal vulnerability that also impacted the OpenWrt product. ...
CVE-2020-0618: Microsoft SQL Server Reporting Services – Remote Code Execution
漏洞标题 CVE-2020-0618: Microsoft SQL Server Reporting Services - Remote Code Execution 漏洞描述 Microsoft SQL Server Reporting Services is vulnerable to a remote code execution vu...
CVE-2023-27638: tshirtecommerce PrestaShop Module – SQL Injection
漏洞标题 CVE-2023-27638: tshirtecommerce PrestaShop Module - SQL Injection 漏洞描述 The tshirtecommerce module for PrestaShop is vulnerable to unauthenticated SQL injection via the...
CVE-2024-10081: CodeChecker <= 6.24.1 - Authentication Bypass
漏洞标题 CVE-2024-10081: CodeChecker <= 6.24.1 - Authentication Bypass 漏洞描述 Authentication bypass occurs when the API URL ends with Authentication, Configuration or ServerIn...
CVE-2024-44000: LiteSpeed Cache <= 6.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-44000: LiteSpeed Cache <= 6.4.1 - Sensitive Information Exposure 漏洞描述 The LiteSpeed Cache plugin for WordPress is vulnerable to Sensitive Information Expos...
CVE-2020-24949: PHP-Fusion 9.03.50 – Remote Code Execution
漏洞标题 CVE-2020-24949: PHP-Fusion 9.03.50 - Remote Code Execution 漏洞描述 PHP-Fusion 9.03.50 downloads/downloads.php allows an authenticated user (not admin) to send a crafted r...
CVE-2020-24949: PHP-Fusion 9.03.50 – Remote Code Execution
漏洞标题 CVE-2020-24949: PHP-Fusion 9.03.50 - Remote Code Execution 漏洞描述 PHP-Fusion 9.03.50 downloads/downloads.php allows an authenticated user (not admin) to send a crafted r...
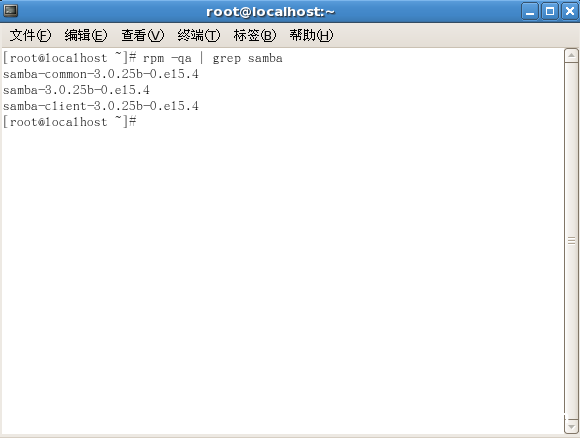
Linux Samba服务器超详细安装配置(附问题解决)_Linux
在嵌入式系统开发应用平台中,tftp、nfs和samba服务器是最常用的文件传输工具,本文详细的介绍一下Linux Samba服务器安装配置,感兴趣的可以了解一下 目录Samba服务器介绍Samba服务器组件Samba...
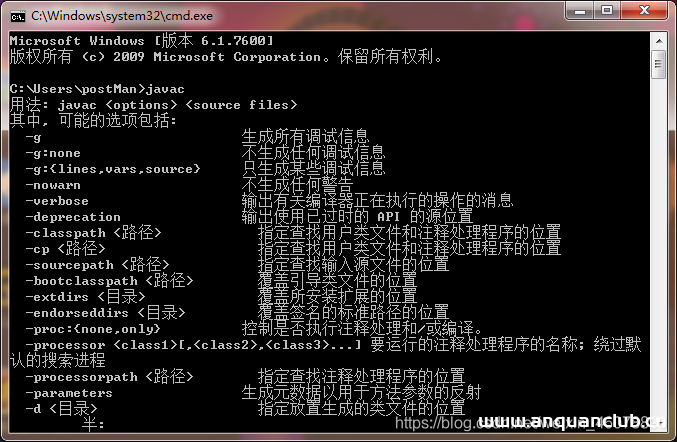
详解Tomcat双击startup.bat闪退的解决方法_Tomcat
这篇文章主要介绍了详解Tomcat双击startup.bat闪退的解决方法,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 作为...
CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting
漏洞标题 CVE-2024-8673: Z-Downloads < 1.11.7 - Cross-Site Scripting 漏洞描述 The plugin does not properly validate uploaded files allowing for the uploading of SVGs containing m...
CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting
漏洞标题 CVE-2021-38156: Nagios XI < 5.8.6 - Cross-Site Scripting 漏洞描述 In Nagios XI before 5.8.6, XSS exists in the dashboard page (/dashboards/#) when administrative users ...
CVE-2021-25297: Nagios 5.5.6-5.7.5 – Authenticated Remote Command Injection
漏洞标题 CVE-2021-25297: Nagios 5.5.6-5.7.5 - Authenticated Remote Command Injection 漏洞描述 Nagios XI 5.5.6 through 5.7.5 is susceptible to authenticated remote command injection...
CVE-2017-11586: FineCMS <5.0.9 - Open Redirect
漏洞标题 CVE-2017-11586: FineCMS <5.0.9 - Open Redirect 漏洞描述 FineCMS 5.0.9 contains an open redirect vulnerability via the url parameter in a sync action. An attacker can re...

