





CVE-2022-29464: WSO2 Management – Arbitrary File Upload & Remote Code Execution
漏洞标题 CVE-2022-29464: WSO2 Management - Arbitrary File Upload & Remote Code Execution 漏洞描述 Certain WSO2 products allow unrestricted file upload with resultant remote cod...
CVE-2021-24175: The Plus Addons for Elementor Page Builder < 4.1.7 - Authentication Bypass
漏洞标题 CVE-2021-24175: The Plus Addons for Elementor Page Builder < 4.1.7 - Authentication Bypass 漏洞描述 The Plus Addons for Elementor plugin (before version 4.1.7) allowed ...
CVE-2019-7254: eMerge E3 1.00-06 – Local File Inclusion
漏洞标题 CVE-2019-7254: eMerge E3 1.00-06 - Local File Inclusion 漏洞描述 Linear eMerge E3-Series devices are vulnerable to local file inclusion. PoC代码
CVE-2020-14181: Jira Server and Data Center – Information Disclosure
漏洞标题 CVE-2020-14181: Jira Server and Data Center - Information Disclosure 漏洞描述 Jira Server and Data Center is susceptible to information disclosure. An attacker can enumera...
CVE-2022-29081: Zoho ManageEngine – Access Control Bypass
漏洞标题 CVE-2022-29081: Zoho ManageEngine - Access Control Bypass 漏洞描述 Zoho ManageEngine Access Manager Plus before 4302, Password Manager Pro before 12007, and PAM360 before ...
CVE-2024-9487: GitHub Enterprise – SAML Authentication Bypass
漏洞标题 CVE-2024-9487: GitHub Enterprise - SAML Authentication Bypass 漏洞描述 An improper verification of cryptographic signature vulnerability was identified in GitHub Enterpris...
CVE-2019-7275: Optergy Proton/Enterprise Building Management System – Open Redirect
漏洞标题 CVE-2019-7275: Optergy Proton/Enterprise Building Management System - Open Redirect 漏洞描述 Optergy Proton/Enterprise Building Management System contains an open redirect...
CVE-2025-0108: PAN-OS Management Interface – Path Confusion to Authentication Bypass
漏洞标题 CVE-2025-0108: PAN-OS Management Interface - Path Confusion to Authentication Bypass 漏洞描述 A vulnerability in PAN-OS management interface allows authentication bypass t...
CVE-2022-38870: Free5gc 3.2.1 – Information Disclosure
漏洞标题 CVE-2022-38870: Free5gc 3.2.1 - Information Disclosure 漏洞描述 Free5gc 3.2.1 is susceptible to information disclosure. An attacker can possibly obtain sensitive informati...
CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection
漏洞标题 CVE-2022-1057: WordPress Pricing Deals for WooCommerce <=2.0.2.02 - SQL Injection 漏洞描述 WordPress Pricing Deals for WooCommerce plugin through 2.0.2.02 contains a SQ...
欧盟数据主管命令欧洲刑警组织删除与犯罪无关的个人数据
根据欧盟数据保护监管机构EDPS于1月10日发布的新闻稿,EDPS已于一周前下令欧洲刑警组织删除与犯罪活动没有明确关联的个人的数据,以减少对公民个人权力和自由的侵犯。 此前,欧洲刑警组织...
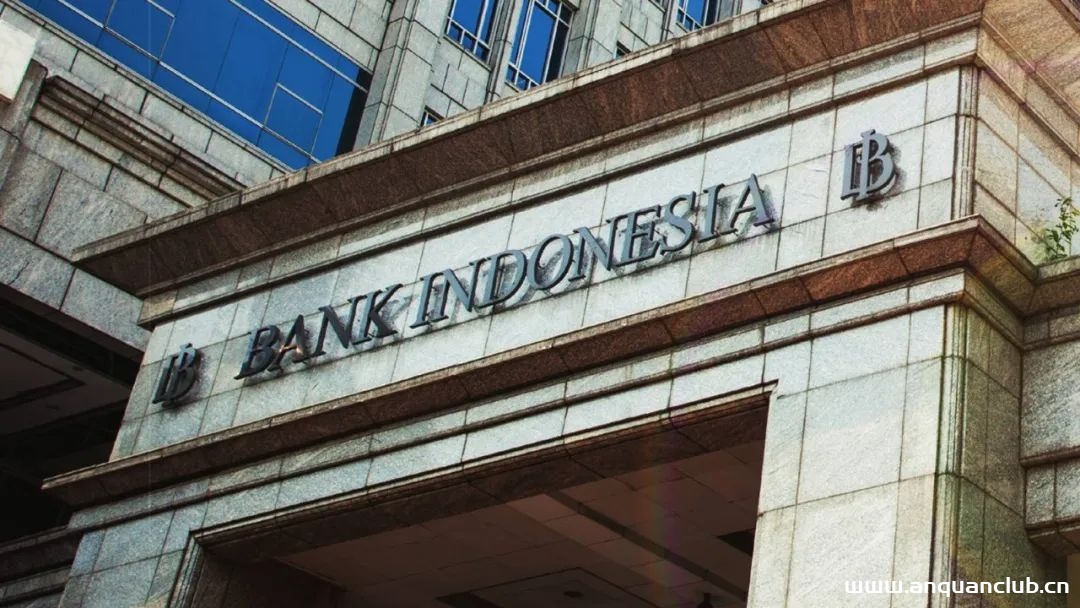
印尼央行确认遭受勒索软件攻击
1月20日,印度尼西亚共和国中央银行——印度尼西亚银行(BANK INDONESIA)通信部执行主任Erwin Haryono证实,银行于上个月遭受了勒索软件攻击。中央银行有着管理货币部门、维持支付系统和金融系...
恶意软件开发者公布密钥并宣布退出江湖
近日,一位名为“Topleak”的用户在BleepingComputer论坛上发布了一个引人注目的帖子,其自称是Maze、Egregor、Sekhmet恶意软件开发者,表示决定向公众发布Maze、Egregor、Sekhmet勒索软件家族...
CVE-2025-4009: Evertz SDVN 3080ipx-10G – Unauthenticated Arbitrary Command Injection
漏洞标题 CVE-2025-4009: Evertz SDVN 3080ipx-10G - Unauthenticated Arbitrary Command Injection 漏洞描述 The Evertz SDVN 3080ipx-10G is a High Bandwidth Ethernet Switching Fabric for...
CVE-2023-21839: Oracle WebLogic Server – Unauthorized Access
漏洞标题 CVE-2023-21839: Oracle WebLogic Server - Unauthorized Access 漏洞描述 Vulnerability in the Oracle WebLogic Server product of Oracle Fusion Middleware (component: Core). Su...
CVE-2025-24354: Imgproxy < 3.27.2 - Server-Side Request Forgery (SSRF)
漏洞标题 CVE-2025-24354: Imgproxy < 3.27.2 - Server-Side Request Forgery (SSRF) 漏洞描述 imgproxy contains an issue caused by not blocking the 0.0.0.0 address even when IMGPROXY...

