





CVE-2024-6049: Lawo AG vsm LTC Time Sync (vTimeSync) – Path Traversal
漏洞标题 CVE-2024-6049: Lawo AG vsm LTC Time Sync (vTimeSync) - Path Traversal 漏洞描述 The web server of Lawo AG vsm LTC Time Sync (vTimeSync) is affected by a "..." (tr...
CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File
漏洞标题 CVE-2024-10486: Google for WooCommerce <= 2.8.6 - Information Disclosure via Publicly Accessible PHP Info File 漏洞描述 The Google for WooCommerce plugin for WordPress ...
CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure
漏洞标题 CVE-2024-30269: DataEase <= 2.4.1 - Sensitive Information Exposure 漏洞描述 DataEase, an open source data visualization and analysis tool, has a database configuration ...
CVE-2021-24943: Registrations for the Events Calendar < 2.7.6 - SQL Injection
漏洞标题 CVE-2021-24943: Registrations for the Events Calendar < 2.7.6 - SQL Injection 漏洞描述 The Registrations for the Events Calendar WordPress plugin before 2.7.6 does not ...
CVE-2021-24452: WordPress W3 Total Cache <2.1.5 - Cross-Site Scripting
漏洞标题 CVE-2021-24452: WordPress W3 Total Cache <2.1.5 - Cross-Site Scripting 漏洞描述 WordPress W3 Total Cache plugin before 2.1.5 is susceptible to cross-site scripting via ...
CVE-2021-21345: XStream < 1.4.16 - Remote Code Execution
漏洞标题 CVE-2021-21345: XStream < 1.4.16 - Remote Code Execution 漏洞描述 XStream before 1.4.16 is susceptible to remote code execution. An attacker who has sufficient rights c...
CVE-2023-6379: OpenCMS 14 & 15 – Cross Site Scripting
漏洞标题 CVE-2023-6379: OpenCMS 14 & 15 - Cross Site Scripting 漏洞描述 Cross-site scripting (XSS) vulnerability in Alkacon Software Open CMS, affecting versions 14 and 15 of t...
CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read
漏洞标题 CVE-2022-33901: WordPress MultiSafepay for WooCommerce <=4.13.1 - Arbitrary File Read 漏洞描述 WordPress MultiSafepay for WooCommerce plugin through 4.13.1 contains an ...
CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting
漏洞标题 CVE-2021-24300: WordPress WooCommerce <1.13.22 - Cross-Site Scripting 漏洞描述 WordPress WooCommerce before 1.13.22 contains a reflected cross-site scripting vulnerabil...
CVE-2024-3673: Web Directory Free < 1.7.3 - Local File Inclusion
漏洞标题 CVE-2024-3673: Web Directory Free < 1.7.3 - Local File Inclusion 漏洞描述 The Web Directory Free WordPress plugin before 1.7.3 does not validate a parameter before usin...
CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion
漏洞标题 CVE-2018-12613: PhpMyAdmin 4.8.1 Remote File Inclusion 漏洞描述 An issue was discovered in phpMyAdmin 4.8.x before 4.8.2, in which an attacker can include (view and potent...
CVE-2023-6549: Citrix Netscaler ADC & Gateway – Out-Of-Bounds Memory Read
漏洞标题 CVE-2023-6549: Citrix Netscaler ADC & Gateway - Out-Of-Bounds Memory Read 漏洞描述 The vulnerability would enable an attacker to remotely obtain sensitive information ...
CVE-2022-4320: WordPress Events Calendar <1.4.5 - Cross-Site Scripting
漏洞标题 CVE-2022-4320: WordPress Events Calendar <1.4.5 - Cross-Site Scripting 漏洞描述 WordPress Events Calendar plugin before 1.4.5 contains multiple cross-site scripting vul...
CVE-2021-24389: WordPress FoodBakery <2.2 - Cross-Site Scripting
漏洞标题 CVE-2021-24389: WordPress FoodBakery <2.2 - Cross-Site Scripting 漏洞描述 WordPress FoodBakery before 2.2 contains an unauthenticated reflected cross-site scripting vul...
CVE-2024-35584: openSIS < 9.1 - SQL Injection
漏洞标题 CVE-2024-35584: openSIS < 9.1 - SQL Injection 漏洞描述 SQL injection vulnerability in Ajax.php, ForWindow.php, ForExport.php, Modules.php, functions/HackingLogFnc.php i...
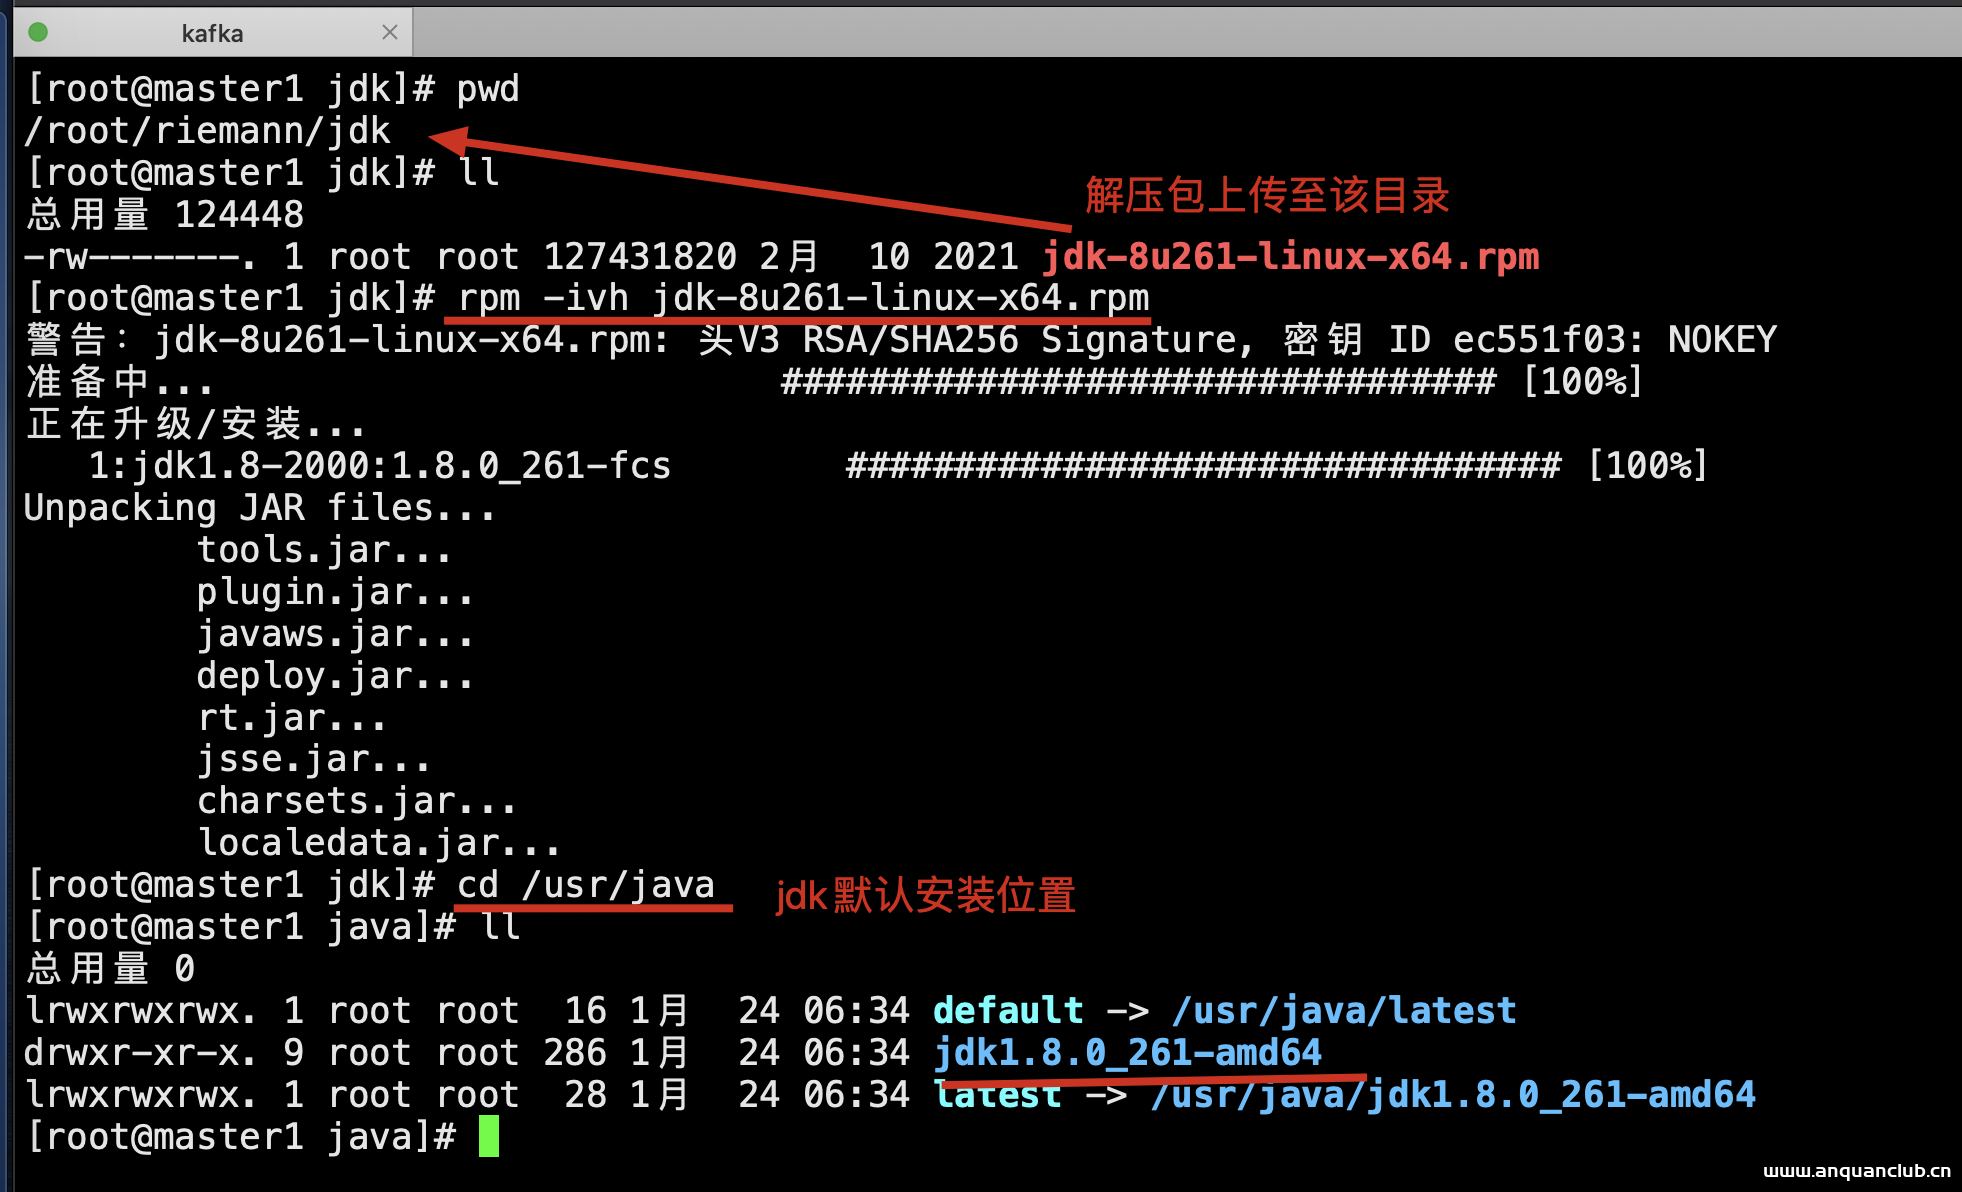
在Linux环境下安装Kafka_Linux
本文以安装Kafka的步骤做了图文详细介绍,Kafka是一种高吞吐量 的分布式发布订阅消息系统,对Kagka感兴趣的小伙伴可以参考参考本篇文章 目录1.1 Java环境为前提1.2 Zookeeper的安装配置1.3 Kafk...

