





CVE-2022-34265: Django – SQL injection
漏洞标题 CVE-2022-34265: Django - SQL injection 漏洞描述 An issue was discovered in Django 3.2 before 3.2.14 and 4.0 before 4.0.6. The Trunc() and Extract() database functions are ...

SEATA事务服务DOCKER部署的过程详解_docker
这篇文章主要介绍了SEATA事务服务DOCKER部署的过程详解,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1、创库授权语句 > create database se...
CVE-2020-22208: 74cms – ajax_street.php ‘x’ SQL Injection
漏洞标题 CVE-2020-22208: 74cms - ajax_street.php 'x' SQL Injection 漏洞描述 SQL Injection in 74cms 3.2.0 via the x parameter to plus/ajax_street.php. PoC代码
CVE-2018-2894: Oracle WebLogic Server – Remote Code Execution
漏洞标题 CVE-2018-2894: Oracle WebLogic Server - Remote Code Execution 漏洞描述 The Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS - Web Services) ...
(CVE-2025-15004)DedeCMS至5.7.118版本freelist_main.php文件orderby参数SQL注入漏洞
漏洞标题 (CVE-2025-15004)DedeCMS至5.7.118版本freelist_main.php文件orderby参数SQL注入漏洞 漏洞描述 (CVE-2025-15004)DedeCMS至5.7.118版本freelist_main.php文件orderby参数SQL注入漏...
CVE-2024-6924: TrueBooker <= 1.0.2 - SQL Injection
漏洞标题 CVE-2024-6924: TrueBooker <= 1.0.2 - SQL Injection 漏洞描述 The TrueBooker Appointment Booking and Scheduler Plugin. plugin for WordPress is vulnerable to SQL Injection...
CVE-2025-6204: DELMIA Apriso – Command Injection
漏洞标题 CVE-2025-6204: DELMIA Apriso - Command Injection 漏洞描述 An Improper Control of Generation of Code (code injection / file upload → RCE) vulnerability affecting DELMIA Ap...
(CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞
漏洞标题 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 漏洞描述 (CVE-2025-4123) Grafana 路径遍历与开放重定向导致的跨站脚本漏洞 PoC代码 暂无
Cellinx NVT 摄像机 GetFileContent.cgi 任意文件读取漏洞 (CVE-2023-23063)
漏洞标题 Cellinx NVT 摄像机 GetFileContent.cgi 任意文件读取漏洞 (CVE-2023-23063) 漏洞描述 Cellinx NVT IP PTZ是韩国Cellinx公司的一个摄像机设备。Cellinx NVTv1.0.6.002b版本存在安全漏...
CVE-2019-17671: WordPress <= 5.2.4 - Unauthenticated View Private/Draft Posts
漏洞标题 CVE-2019-17671: WordPress <= 5.2.4 - Unauthenticated View Private/Draft Posts 漏洞描述 WordPress before 5.2.4 contains an information disclosure caused by mishandling o...
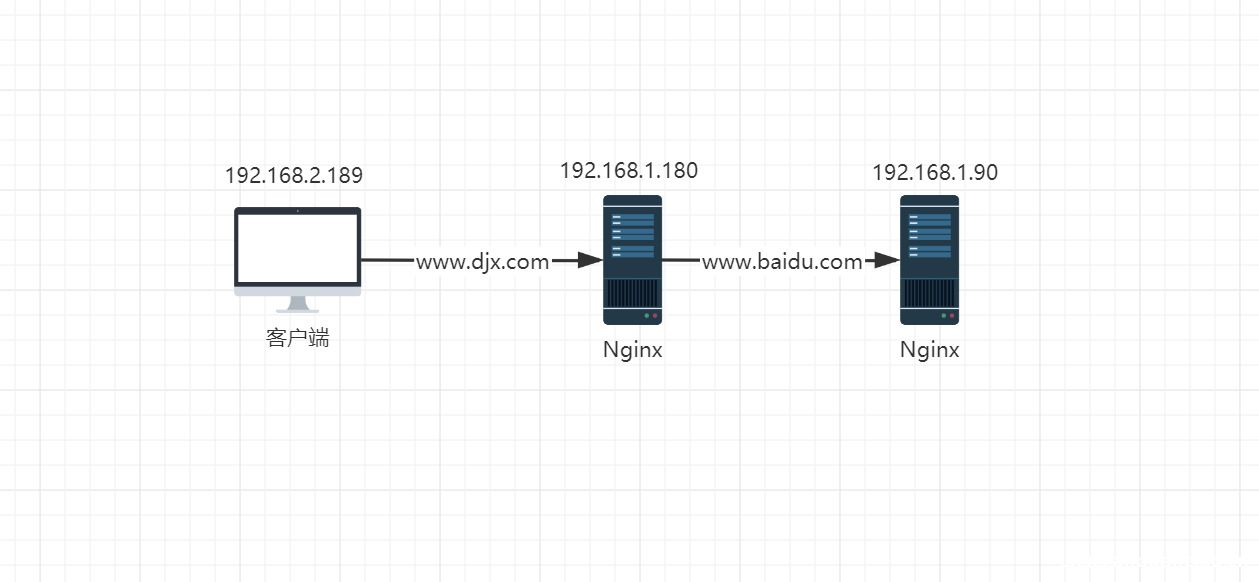
解决Nginx 配置 proxy_pass 后 返回404问题_nginx
这篇文章主要介绍了Nginx 配置 proxy_pass 后 返回404问题,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录一、 Nginx 配置 proxy_pass 后 返...
CVE-2024-51568: CyberPanel – Command Injection
漏洞标题 CVE-2024-51568: CyberPanel - Command Injection 漏洞描述 CyberPanel (aka Cyber Panel) before 2.3.5 allows Command Injection via completePath in the ProcessUtilities.outputE...
CVE-2021-41277 Metabase 信息泄露漏洞
漏洞标题 CVE-2021-41277 Metabase 信息泄露漏洞 漏洞描述 CVE-2021-41277 Metabase 信息泄露漏洞 PoC代码 暂无
CVE-2023-4169: Ruijie RG-EW1200G Router – Password Reset
漏洞标题 CVE-2023-4169: Ruijie RG-EW1200G Router - Password Reset 漏洞描述 A vulnerability was found in Ruijie RG-EW1200G 1.0(1)B1P5. It has been declared as critical. Affected by ...
CVE-2022-25488: Atom CMS v2.0 – SQL Injection
漏洞标题 CVE-2022-25488: Atom CMS v2.0 - SQL Injection 漏洞描述 Atom CMS v2.0 was discovered to contain a SQL injection vulnerability via the id parameter in /admin/ajax/avatar.php...
CVE-2021-3110: PrestaShop 1.7.7.0 – SQL Injection
漏洞标题 CVE-2021-3110: PrestaShop 1.7.7.0 - SQL Injection 漏洞描述 PrestaShop 1.7.7.0 contains a SQL injection vulnerability via the store system. It allows time-based boolean SQL...

