





CVE-2023-41763: Skype for Business 2019 (SfB) – Blind Server-side Request Forgery
漏洞标题 CVE-2023-41763: Skype for Business 2019 (SfB) - Blind Server-side Request Forgery 漏洞描述 Skype Pre-Auth Server-side Request Forgery (SSRF) vulnerability PoC代码
CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
CVE-2010-1602: Joomla! Component ZiMB Comment 0.8.1 – Local File Inclusion
漏洞标题 CVE-2010-1602: Joomla! Component ZiMB Comment 0.8.1 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the ZiMB Comment (com_zimbcomment) component 0.8...
CVE-2021-24165: WordPress Ninja Forms <3.4.34 - Open Redirect
漏洞标题 CVE-2021-24165: WordPress Ninja Forms <3.4.34 - Open Redirect 漏洞描述 WordPress Ninja Forms plugin before 3.4.34 contains an open redirect vulnerability via the wp_aja...
CVE-2023-46359: cPH2 Charging Station v1.87.0 – OS Command Injection
漏洞标题 CVE-2023-46359: cPH2 Charging Station v1.87.0 - OS Command Injection 漏洞描述 An OS command injection vulnerability in Hardy Barth cPH2 Ladestation v1.87.0 and earlier, ma...
CVE-2022-22963: Spring Cloud – Remote Code Execution
漏洞标题 CVE-2022-22963: Spring Cloud - Remote Code Execution 漏洞描述 Spring Cloud Function versions 3.1.6, 3.2.2 and older unsupported versions are susceptible to remote code exe...
CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read
漏洞标题 CVE-2024-23897: Jenkins < 2.441 - Arbitrary File Read 漏洞描述 Jenkins 2.441 and earlier, LTS 2.426.2 and earlier does not disable a feature of its CLI command parser t...
CVE-2024-12209: WP Umbrella Update Backup Restore & Monitoring <= 2.17.0 - Local File Inclusion
漏洞标题 CVE-2024-12209: WP Umbrella Update Backup Restore & Monitoring <= 2.17.0 - Local File Inclusion 漏洞描述 The WP Umbrella: Update Backup Restore & Monitoring plu...
CVE-2022-43170: Rukovoditel <= 3.2.1 - Cross Site Scripting
漏洞标题 CVE-2022-43170: Rukovoditel <= 3.2.1 - Cross Site Scripting 漏洞描述 A stored cross-site scripting (XSS) vulnerability in the Dashboard Configuration feature (index.php...
docker实现redis集群搭建的方法步骤_docker
本文主要介绍了docker实现redis集群搭建的方法步骤,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录一、创建redis docker基础镜像二、制作redis节点...
CVE-2022-0281: Microweber Information Disclosure
漏洞标题 CVE-2022-0281: Microweber Information Disclosure 漏洞描述 Microweber contains a vulnerability that allows exposure of sensitive information to an unauthorized actor in Pac...
CVE-2022-1026: Kyocera Net View Address Book Exposure
漏洞标题 CVE-2022-1026: Kyocera Net View Address Book Exposure 漏洞描述 Kyocera multifunction printers running vulnerable versions of Net View unintentionally expose sensitive user...
CVE-2023-0676: phpIPAM 1.5.1 – Cross-site Scripting
漏洞标题 CVE-2023-0676: phpIPAM 1.5.1 - Cross-site Scripting 漏洞描述 Cross-site Scripting (XSS) - Reflected in GitHub repository phpipam/phpipam prior to 1.5.1. PoC代码
CVE-2022-2546: WordPress All-in-One WP Migration <=7.62 - Cross-Site Scripting
漏洞标题 CVE-2022-2546: WordPress All-in-One WP Migration <=7.62 - Cross-Site Scripting 漏洞描述 WordPress All-in-One WP Migration plugin 7.62 and prior contains a cross-site sc...
CVE-2023-4415: 锐捷(ruijie)RG-EW1200G路由器 后台登录绕过
漏洞标题 CVE-2023-4415: 锐捷(ruijie)RG-EW1200G路由器 后台登录绕过 漏洞描述 Ruijie Networks RG-EW1200G是中国锐捷网络(Ruijie Networks)公司的一款无线路由器。 锐捷网络RG-EW1200G路由...
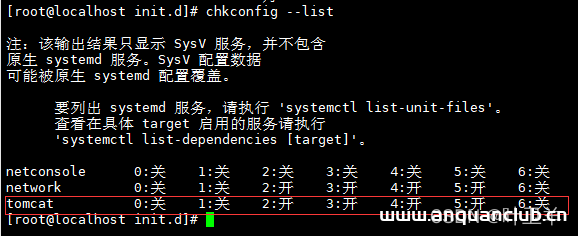
Linux系统设置tomcat开机自启介绍_Linux
大家好,本篇文章主要讲的是Linux系统设置tomcat开机自启介绍,感兴趣的同学赶快来看一看吧,对你有帮助的话记得收藏一下,方便下次浏览 1.进入到 /etc/init.d 目录中: cd /etc/init.d 2.创建 ...

