





CVE-2023-43208: NextGen Healthcare Mirth Connect – Remote Code Execution
漏洞标题 CVE-2023-43208: NextGen Healthcare Mirth Connect - Remote Code Execution 漏洞描述 Unauthenticated remote code execution vulnerability in NextGen Healthcare Mirth Connect b...
CVE-2022-2633: All-In-One Video Gallery <=2.6.0 - Server-Side Request Forgery
漏洞标题 CVE-2022-2633: All-In-One Video Gallery <=2.6.0 - Server-Side Request Forgery 漏洞描述 WordPress All-in-One Video Gallery plugin through 2.6.0 is susceptible to arbitra...
CVE-2024-3080: ASUS DSL-AC88U – Authentication Bypass
漏洞标题 CVE-2024-3080: ASUS DSL-AC88U - Authentication Bypass 漏洞描述 A vulnerability in the ASUS DSL-AC88U router permits unauthorized individuals to bypass authentication.When ...
CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update
漏洞标题 CVE-2022-28666: Custom Product Tabs for WooCommerce < 1.7.8 - Unauthenticated Toggle Content Setting Update 漏洞描述 YIKES Inc. Custom Product Tabs for WooCommerce plug...
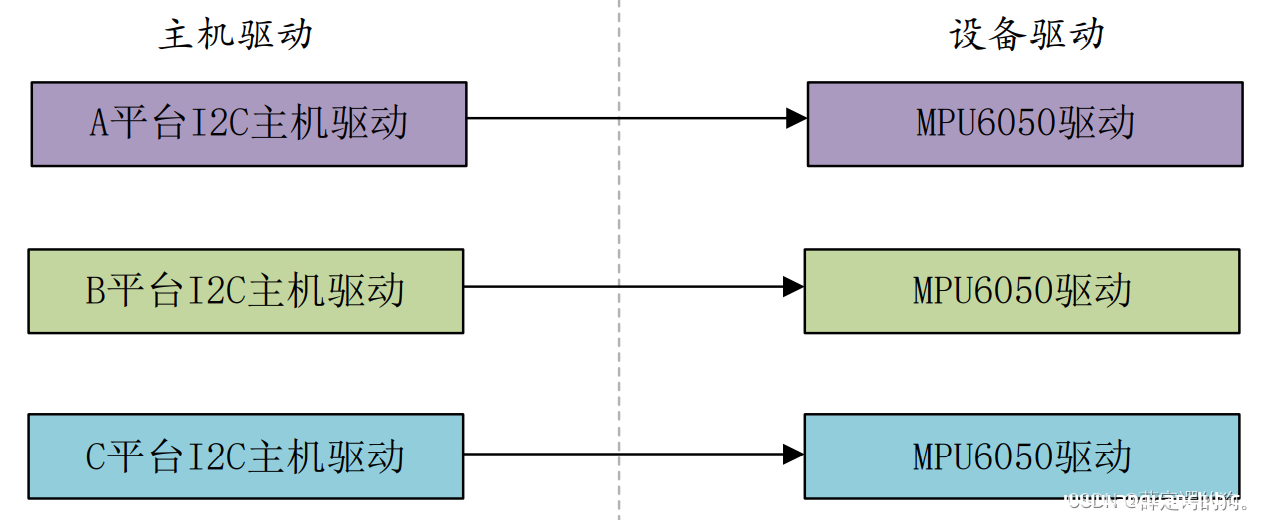
Linux驱动之platform总线详解_Linux
目录1、platform 总线简介1.1、Linux 驱动的分离和分层思想1.1.1、Linux 驱动的分离1.2、platform 平台驱动模型2、platform 框架2.1、platform 总线2.2、platform 驱动2.2.1、platform 驱动定义...
CVE-2024-4257: BlueNet Technology Clinical Browsing System 1.2.1 – Sql Injection
漏洞标题 CVE-2024-4257: BlueNet Technology Clinical Browsing System 1.2.1 - Sql Injection 漏洞描述 A vulnerability was found in BlueNet Technology Clinical Browsing System 1.2.1. I...
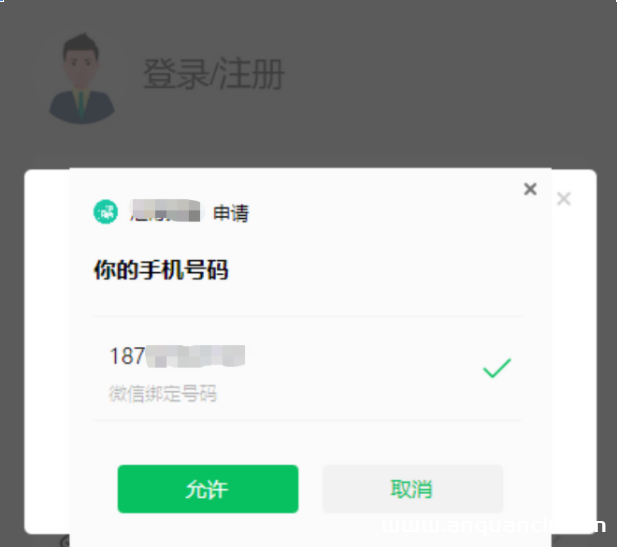
微信小程序SessionKey导致的任意手机号接管
如果小程序存在手机号快捷登录,首先需要获取微信用户绑定的手机号。先调用wx.login接口,由用户主动触发来获取手机号。微信小程序存在EncryptedData、SessionKey、IV来进行加密的机制,Encrypt...
CVE-2022-0678: Microweber <1.2.11 - Cross-Site Scripting
漏洞标题 CVE-2022-0678: Microweber <1.2.11 - Cross-Site Scripting 漏洞描述 Packagist prior to 1.2.11 contains a cross-site scripting vulnerability via microweber/microweber. Use...
CVE-2024-57514: TP-Link Archer A20 v3 Router – Cross-site Scripting
漏洞标题 CVE-2024-57514: TP-Link Archer A20 v3 Router - Cross-site Scripting 漏洞描述 The TP-Link Archer A20 v3 router is vulnerable to Cross-site Scripting (XSS) due to improper h...
CVE-2023-4547: SPA-Cart eCommerce CMS 1.9.0.3 – Cross-Site Scripting
漏洞标题 CVE-2023-4547: SPA-Cart eCommerce CMS 1.9.0.3 - Cross-Site Scripting 漏洞描述 A vulnerability was found in SPA-Cart eCommerce CMS 1.9.0.3. It has been rated as problematic...
CVE-2024-55556: InvoiceShelf <= 1.3.0 - PHP Deserialization
漏洞标题 CVE-2024-55556: InvoiceShelf <= 1.3.0 - PHP Deserialization 漏洞描述 InvoiceShelf version 1.3.0 and below contains an unauthenticated PHP deserialization vulnerability ...
CVE-2024-49757: Zitadel – User Registration Bypass
漏洞标题 CVE-2024-49757: Zitadel - User Registration Bypass 漏洞描述 The open-source identity infrastructure software Zitadel allows administrators to disable the user self-registr...
Apache Solr反序列化漏洞(CVE-2019-0192)
漏洞标题 Apache Solr反序列化漏洞(CVE-2019-0192) 漏洞描述 ApacheSolr是一个独立的企业级搜索应用服务器,它对外提供类似于Web-service的API接口。用户可以通过http请求,向搜索引擎服务器提...
CVE-2023-43795: GeoServer WPS – Server Side Request Forgery
漏洞标题 CVE-2023-43795: GeoServer WPS - Server Side Request Forgery 漏洞描述 GeoServer is an open source software server written in Java that allows users to share and edit geospa...
CVE-2020-14144: Gitea 1.1.0 – 1.12.5 – Remote Code Execution
漏洞标题 CVE-2020-14144: Gitea 1.1.0 - 1.12.5 - Remote Code Execution 漏洞描述 Gitea 1.1.0 through 1.12.5 is susceptible to authenticated remote code execution, via the git hook fu...
CVE-2024-47062: Navidrome < 0.53.0 - Authenticated SQL Injection
漏洞标题 CVE-2024-47062: Navidrome < 0.53.0 - Authenticated SQL Injection 漏洞描述 Navidrome is an open source web-based music collection server and streamer. Navidrome automati...

