





CVE-2019-5591: FortiOS – Insecure LDAP Configuration Detection
漏洞标题 CVE-2019-5591: FortiOS - Insecure LDAP Configuration Detection 漏洞描述 The FortiGate LDAP configuration was detected to be insecure due to missing ca-cert, secure LDAPS, ...
cloudpanel /file-manager/backend/makefile 任意文件上传漏洞(CVE-2023-35885)
漏洞标题 cloudpanel /file-manager/backend/makefile 任意文件上传漏洞(CVE-2023-35885) 漏洞描述 CloudPanel是CloudPanel开源的一款免费软件。用于配置和管理服务器。CloudPanel 2.3.1之前...

bugbounty技巧聚合20210917
热点跟踪 匿名黑客泄露数百 GB 的 Epik 数据 下载地址:http://ddosecrets.com/images/1/13/EpikFail.torrent 漏洞报告 Topcoder SSRF经典利用方式,读取aws元数据 http://hackerone.com/report...
Aria2 WebUI控制台 /../../../../etc/passwd 文件读取漏洞(CVE-2023-39141)
漏洞标题 Aria2 WebUI控制台 /../../../../etc/passwd 文件读取漏洞(CVE-2023-39141) 漏洞描述 搜索: etc/passwd 文件读取漏洞(CVE-2023-39141) 最近共 1 条结果 2024-11-15 Aria2 WebUI控...
CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting
漏洞标题 CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting 漏洞描述 WordPress Visualizer plugin before 3.3.1 contains a stored cross-site scripting vulnerabilit...
CVE-2024-42009: Roundcube Webmail – Cross-Site Scripting
漏洞标题 CVE-2024-42009: Roundcube Webmail - Cross-Site Scripting 漏洞描述 A Cross-Site Scripting vulnerability in Roundcube through 1.5.7 and 1.6.x through 1.6.7 allows a remote a...

linux 配置本地yum源,配置国内yum源,配置epel源的步骤_Linux
这篇文章主要介绍了linux 配置本地yum源,配置国内yum源,配置epel源的步骤,帮助大家更好的配置服务器,感兴趣的朋友可以了解下 一.配置本地yum源 1.挂载ISO镜像 mount -o loop /mnt/yum-iso/C...
我有一个朋友,他被裸聊诈骗了。我只能看看能不能帮帮他
小说三要素:时间、地点、人物 时间:2021年12月份 地点:互联网 人物:我有一个朋友 我有一个朋友,当时跟我说的时候已经被骗了23w,想继续充钱10w,问我能不能继续冲,我听了来龙去脉,很明显...
Docker方式启动tomcat访问首页出现404错误_docker
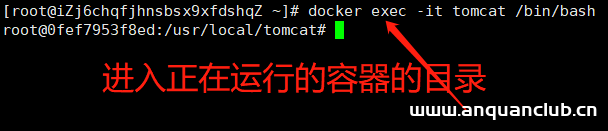
这篇文章主要介绍了Docker方式启动tomcat访问首页出现404错误。文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 场景...
基于docker搭建selenium分布式环境_docker
这篇文章主要介绍了基于docker搭建selenium分布式环境,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 1、下载镜像 docker pull selenium/...
Docker开启远程访问的实现方式_docker
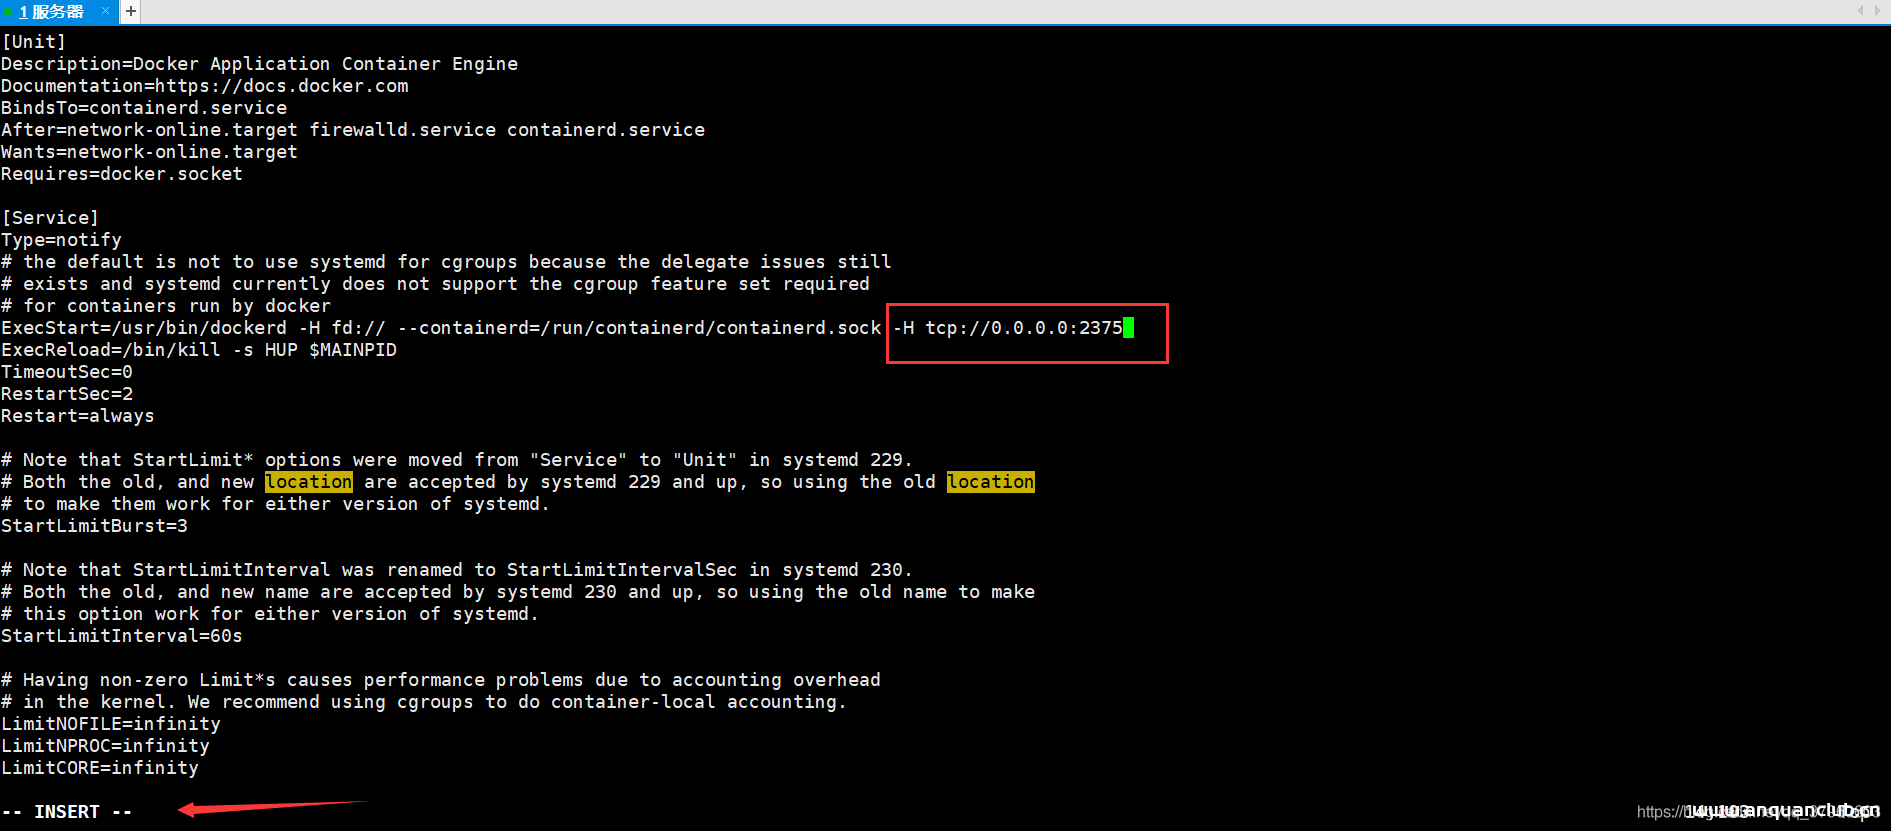
这篇文章主要介绍了Docker开启远程访问的实现方式,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 Docker守护进程...
CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF)
漏洞标题 CVE-2023-30019: Imgproxy <= 3.14.0 - Server-side request forgery (SSRF) 漏洞描述 imgproxy <=3.14.0 is vulnerable to Server-Side Request Forgery (SSRF) due to a lack ...
Docker 命令自动补全的实现_docker
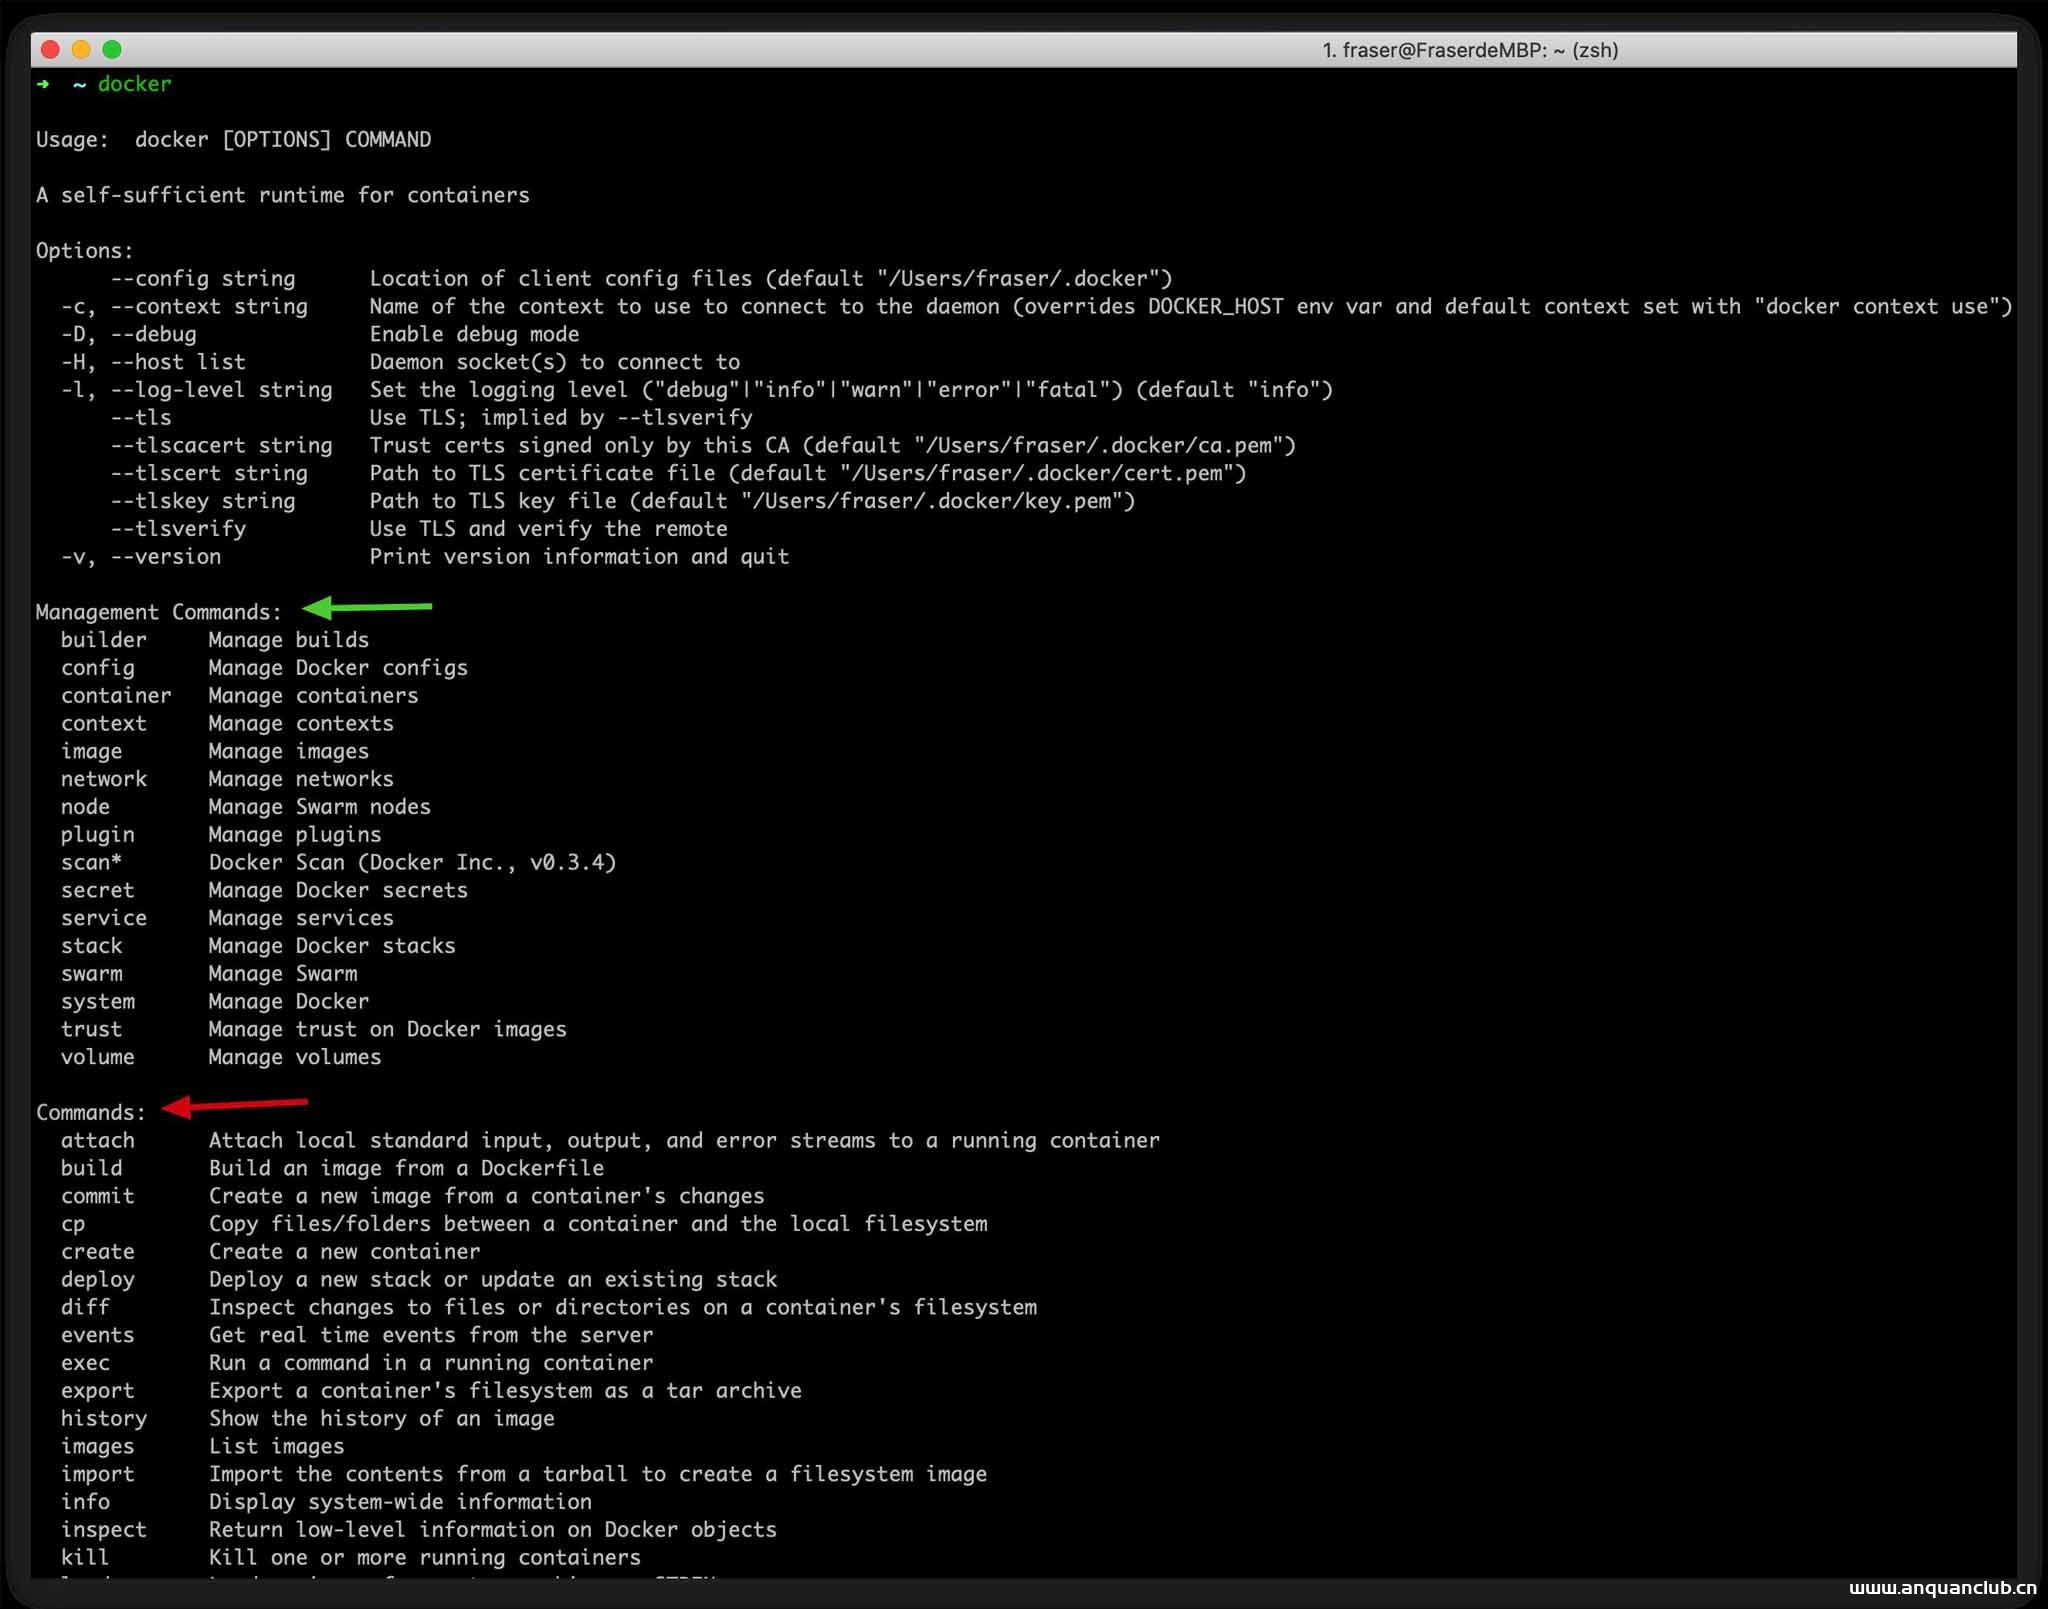
这篇文章主要介绍了Docker 命令自动补全的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 前言 不知道这个小...
bugbounty技巧聚合20210923
漏洞报告 Zomato 【750刀】安卓deeplink利用 http://hackerone.com/reports/532225 挖洞技巧 【15000刀】npm漏洞五连杀 CVE-2021-32804 ($10,000) CVE-2021-32803 ($2,000) CVE-2021-37701 ($2,...
CVE-2023-49494: DedeCMS v5.7.111 – Cross-Site Scripting
漏洞标题 CVE-2023-49494: DedeCMS v5.7.111 - Cross-Site Scripting 漏洞描述 DedeCMS v5.7.111 was discovered to contain a reflective cross-site scripting (XSS) vulnerability via the c...
Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965)
漏洞标题 Apache Struts2(S2-012)远程代码执行漏洞(CVE-2013-1965) 漏洞描述 S2-012中,包含特制请求参数的请求可用于将任意 OGNL代码注入属性,然后用作重定向地址的请求参数,这将导致进一步...

