




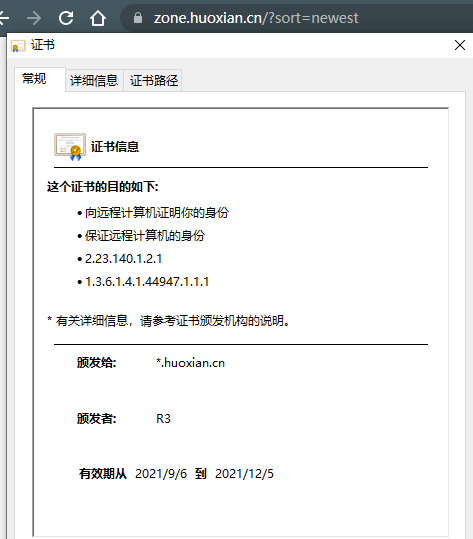
批量获取网站SSL证书里的域名
大佬们在日常刷洞过程中,或者批量扫某个POC时,总会扫到很多未知资产或者结果量太大一个个去验证资产归属太费时费力。而一些https站点的证书中能看到证书归属,一般通过证书定位的资产都比较准...
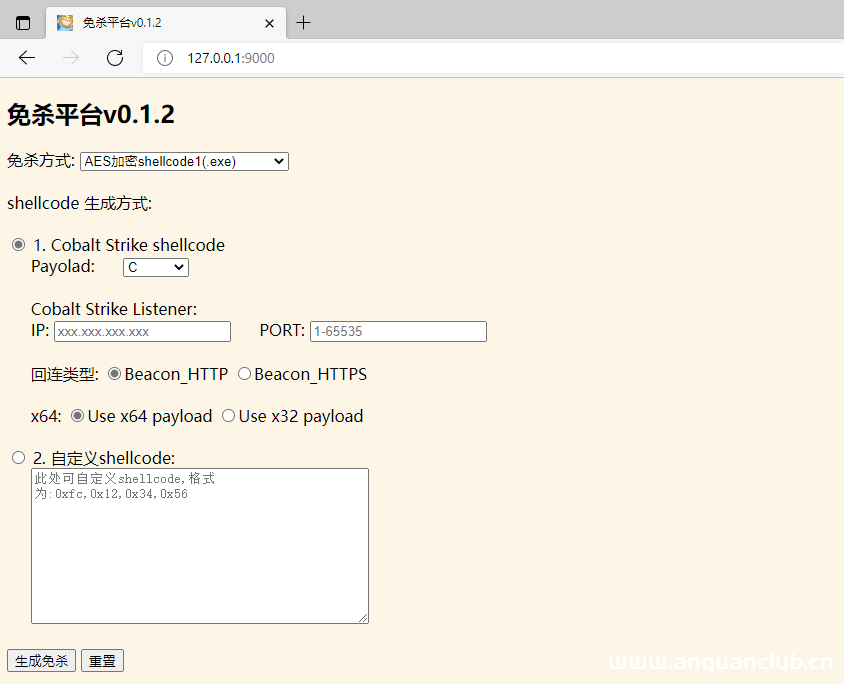
免杀基础教学
0x00 前言: 最近闲来无事搞了一个免杀平台玩儿玩儿,用于生成免杀Cobalt Strike木马和免杀加载一些其它shellcode(如msf、自定义等),这里就和大家分享一下免杀思路。 通过本篇文章你将学会: 杀...

Nginx服务器添加Systemd自定义服务过程解析_nginx
这篇文章主要介绍了Nginx服务器添加Systemd自定义服务过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 一、以nginx为例 使用yum命...
使用Tomcat Native提升Tomcat IO效率的方法详解_Tomcat
这篇文章主要介绍了使用Tomcat Native提升Tomcat IO效率的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 目录简介Tomcat的连接方式APR和Tom...
Nginx 负载均衡是什么以及该如何配置_nginx
这篇文章主要介绍了Nginx 负载均衡是什么以及该如何配置,帮助大家更好的理解和使用Nginx服务器,感兴趣的朋友可以了解下 什么是负载均衡 负载均衡主要通过专门的硬件设备或者通过软件算法实现...
docker 连接宿主Mysql操作_docker
这篇文章主要介绍了docker 连接宿主Mysql操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 今天公司项目要配置docker,顺利在windows上装完了之后,发现连接不上本地的mys...
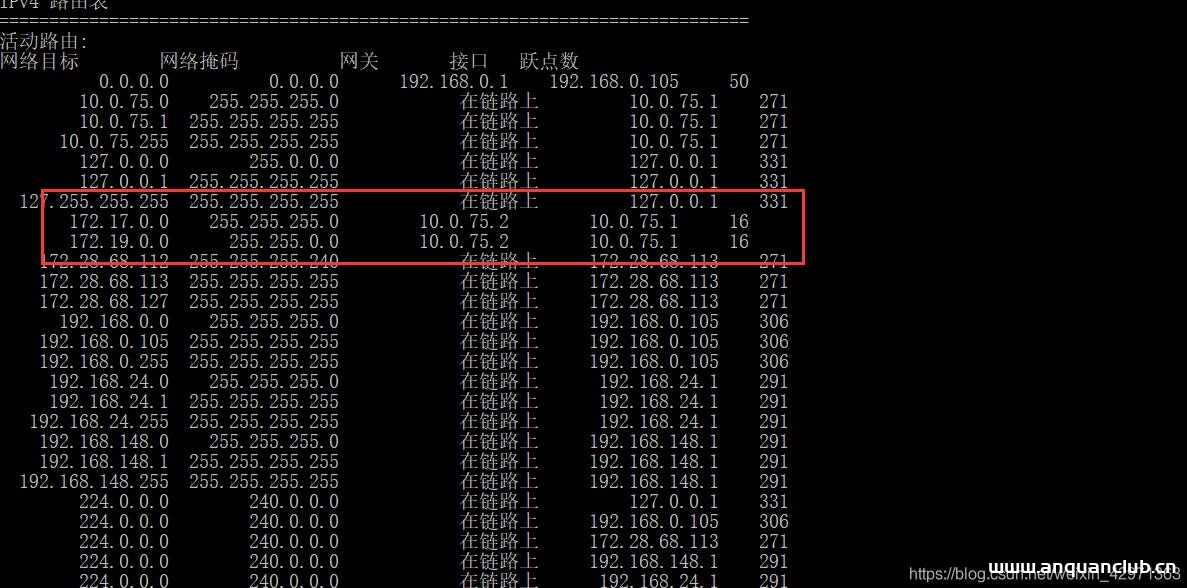
docker win ping 不通容器 避坑指南_docker
这篇文章主要介绍了docker win ping 不通容器 避坑指南,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 使用win docker-desktop,想连接容器开发,尝试了各种网络上的路子。...

CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure
漏洞标题 CVE-2021-24917: WordPress WPS Hide Login <1.9.1 - Information Disclosure 漏洞描述 WordPress WPS Hide Login plugin before 1.9.1 is susceptible to incorrect authorization...
CVE-2021-32789: WooCommerce Blocks 2.5 to 5.5 – Unauthenticated SQL Injection
漏洞标题 CVE-2021-32789: WooCommerce Blocks 2.5 to 5.5 - Unauthenticated SQL Injection 漏洞描述 woocommerce-gutenberg-products-block is a feature plugin for WooCommerce Gutenberg B...
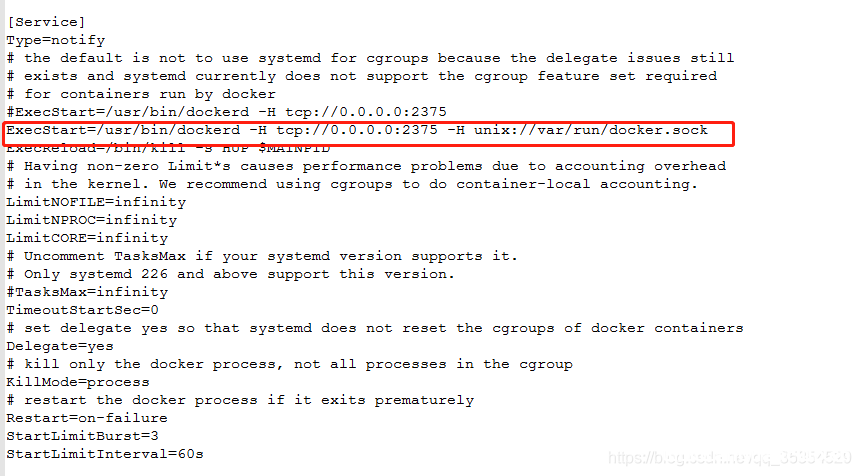
IDEA 配置Docker的过程_docker
这篇文章主要介绍了IDEA 配置Docker的过程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 IDEA是Java最常用的开发工具,而Docker是当下最火的部...
CVE-2013-4117: WordPress Plugin Category Grid View Gallery 2.3.1 – Cross-Site Scripting
漏洞标题 CVE-2013-4117: WordPress Plugin Category Grid View Gallery 2.3.1 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in includes/CatGridPost.php in the Ca...
CVE-2024-40422: Devika v1 – Path Traversal
漏洞标题 CVE-2024-40422: Devika v1 - Path Traversal 漏洞描述 The snapshot_path parameter in the /api/get-browser-snapshot endpoint in stitionai devika v1 is susceptible to a path t...
Docker images导出和导入操作_docker
这篇文章主要介绍了Docker images导出和导入操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 之前已配置好基础镜像,其他地方也需要用到这些镜像时怎么办呢? 答案:镜...
CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting
漏洞标题 CVE-2019-16931: WordPress Visualizer <3.3.1 - Cross-Site Scripting 漏洞描述 WordPress Visualizer plugin before 3.3.1 contains a stored cross-site scripting vulnerabilit...
CVE-2023-45852: Viessmann Vitogate 300 – Remote Code Execution
漏洞标题 CVE-2023-45852: Viessmann Vitogate 300 - Remote Code Execution 漏洞描述 In Vitogate 300 2.1.3.0, /cgi-bin/vitogate.cgi allows an unauthenticated attacker to bypass authent...
CVE-2014-6271: ShellShock – Remote Code Execution
漏洞标题 CVE-2014-6271: ShellShock - Remote Code Execution 漏洞描述 GNU Bash through 4.3 processes trailing strings after function definitions in the values of environment variable...

