






CVE-2021-31589: BeyondTrust Secure Remote Access Base <=6.0.1 - Cross-Site Scripting
漏洞标题 CVE-2021-31589: BeyondTrust Secure Remote Access Base <=6.0.1 - Cross-Site Scripting 漏洞描述 BeyondTrust Secure Remote Access Base through 6.0.1 contains a cross-site ...
CVE-2021-24175: The Plus Addons for Elementor Page Builder < 4.1.7 - Authentication Bypass
漏洞标题 CVE-2021-24175: The Plus Addons for Elementor Page Builder < 4.1.7 - Authentication Bypass 漏洞描述 The Plus Addons for Elementor plugin (before version 4.1.7) allowed ...
CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass
漏洞标题 CVE-2025-27223: TRUfusion Enterprise <= 7.10.4.0 - Authentication Bypass 漏洞描述 Hard-Coded Cryptographic key allowing to forge session cookies that can be used to ent...
CVE-2023-2356: Mlflow <2.3.0 - Local File Inclusion
漏洞标题 CVE-2023-2356: Mlflow <2.3.0 - Local File Inclusion 漏洞描述 Relative Path Traversal in GitHub repository mlflow/mlflow prior to 2.3.1. PoC代码
CVE-2025-6934: The Opal Estate Pro – Property Management <= 1.7.5 - Unauthenticated Privilege Escalation
漏洞标题 CVE-2025-6934: The Opal Estate Pro – Property Management <= 1.7.5 - Unauthenticated Privilege Escalation 漏洞描述 The Opal Estate Pro plugin (≤ 1.7.5) is vulnerable t...
CVE-2010-2680: Joomla! Component jesectionfinder – Local File Inclusion
漏洞标题 CVE-2010-2680: Joomla! Component jesectionfinder - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the JExtensions JE Section/Property Finder (jesecti...
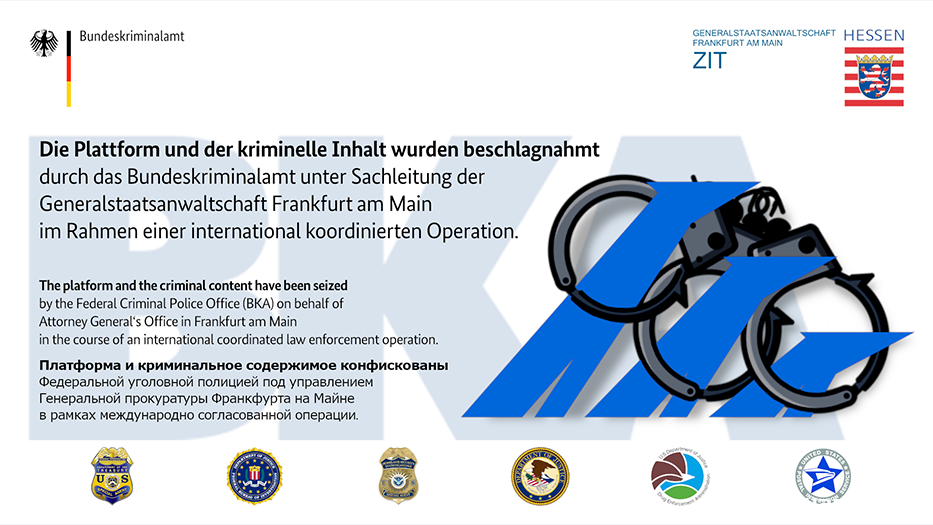
美德联合执法拿下世界最大暗网市场
本周二,美国司法部和德国联邦警察公布了其一次联合执法行动的成果——拆除了世界上最大的暗网市场之一Hydra,查获并扣押了Hydra的服务器和价值2500万美元的比特币。Hydra是一个使用俄语的地下...
CVE-2022-27228: Bitrix Site Manager – Remote Code Execution
漏洞标题 CVE-2022-27228: Bitrix Site Manager - Remote Code Execution 漏洞描述 In the vote (aka "Polls, Votes") module before 21.0.100 of Bitrix Site Manager, a remote una...
CVE-2022-30073: WBCE CMS 1.5.2 – Cross-Site Scripting
漏洞标题 CVE-2022-30073: WBCE CMS 1.5.2 - Cross-Site Scripting 漏洞描述 WBCE CMS 1.5.2 contains a stored cross-site scripting vulnerability via \admin\user\save.php Display Name pa...
CVE-2020-26948: Emby < 4.5.0 - Server Server-Side Request Forgery
漏洞标题 CVE-2020-26948: Emby < 4.5.0 - Server Server-Side Request Forgery 漏洞描述 Emby Server before 4.5.0 allows server-side request forgery (SSRF) via the Items/RemoteSearch...
CVE-2021-30134: Php-mod/curl Library <2.3.2 - Cross-Site Scripting
漏洞标题 CVE-2021-30134: Php-mod/curl Library <2.3.2 - Cross-Site Scripting 漏洞描述 Php-mod/curl library before 2.3.2 contains a cross-site scripting vulnerability via the post...
CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection
漏洞标题 CVE-2022-0434: WordPress Page Views Count <2.4.15 - SQL Injection 漏洞描述 WordPress Page Views Count plugin prior to 2.4.15 contains an unauthenticated SQL injection v...
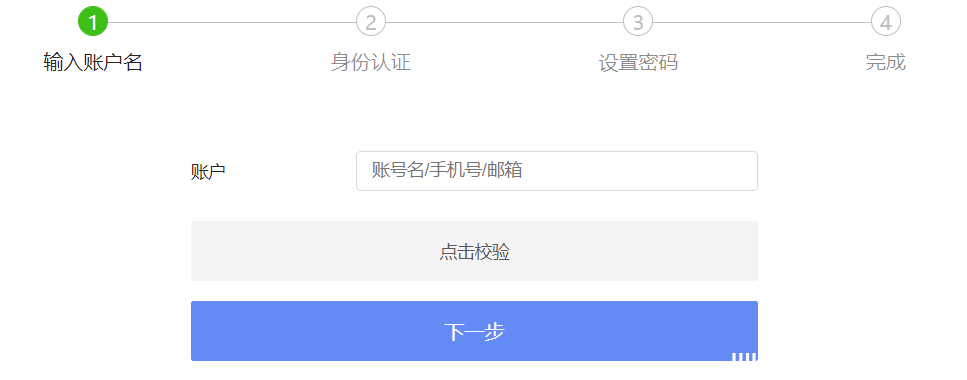
一次任意密码重置漏洞挖洞剖析
前言: 之前参加一家企业SRC挖洞,正赶上厂商搞活动,秉着有活动我就参加,有漏洞我就捡的良好心态,就去看了一下该企业的一些资产,因为活动是按漏洞危害等级给奖励,所以找一些边缘资产参加活...
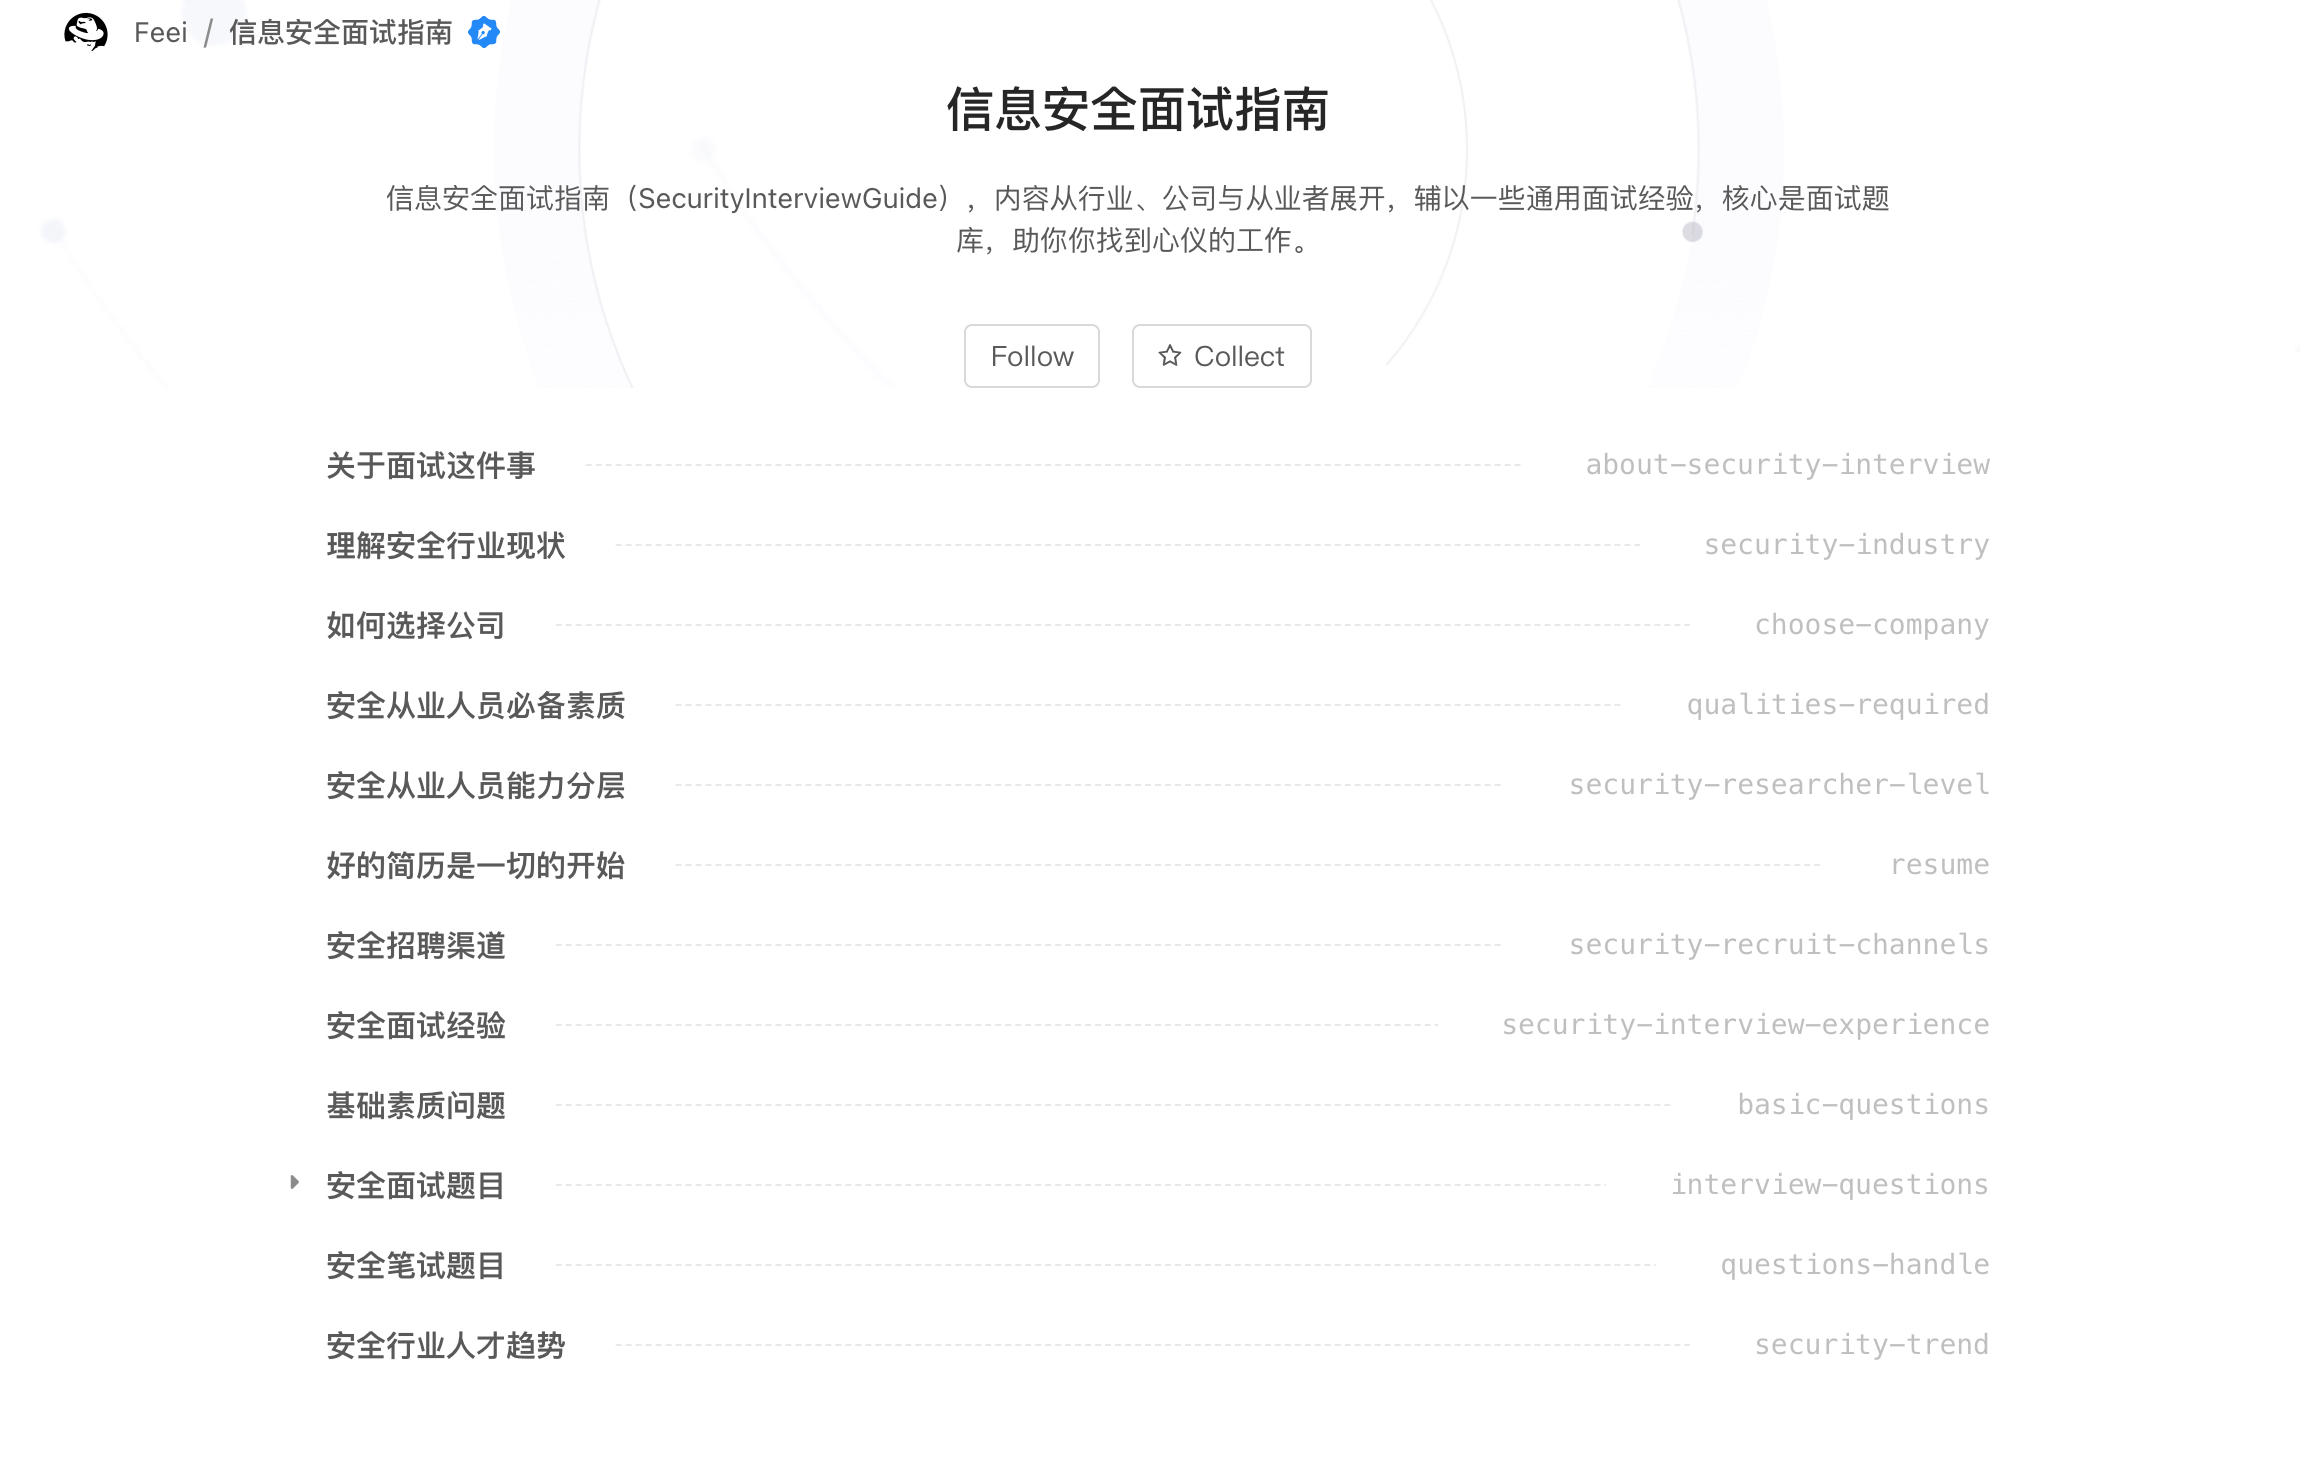
信息安全面试指南
地址: http://www.yuque.com/feei/sig 信息安全面试指南(SecurityInterviewGuide),内容从行业、公司与从业者展开,辅以一些通用面试经验,核心是面试题库,助你你找到心仪的工作。
CVE-2010-5028: Joomla! Component JE Job 1.0 – Local File Inclusion
漏洞标题 CVE-2010-5028: Joomla! Component JE Job 1.0 - Local File Inclusion 漏洞描述 A SQL injection vulnerability in the JExtensions JE Job (com_jejob) component 1.0 for Joomla! a...
CVE-2022-28117: Navigate CMS 2.9.4 – Server-Side Request Forgery
漏洞标题 CVE-2022-28117: Navigate CMS 2.9.4 - Server-Side Request Forgery 漏洞描述 Navigate CMS 2.9.4 is susceptible to server-side request forgery via feed_parser class. This can ...

