





CVE-2022-22965: Spring – Remote Code Execution
漏洞标题 CVE-2022-22965: Spring - Remote Code Execution 漏洞描述 Spring MVC and Spring WebFlux applications running on Java Development Kit 9+ are susceptible to remote code execut...
CVE-2022-1390: WordPress Admin Word Count Column 2.2 – Local File Inclusion
漏洞标题 CVE-2022-1390: WordPress Admin Word Count Column 2.2 - Local File Inclusion 漏洞描述 The plugin does not validate the path parameter given to readfile(), which could allow...
CVE-2015-3306: ProFTPd – Remote Code Execution
漏洞标题 CVE-2015-3306: ProFTPd - Remote Code Execution 漏洞描述 ProFTPD 1.3.5 contains a remote code execution vulnerability via the mod_copy module which allows remote attackers ...
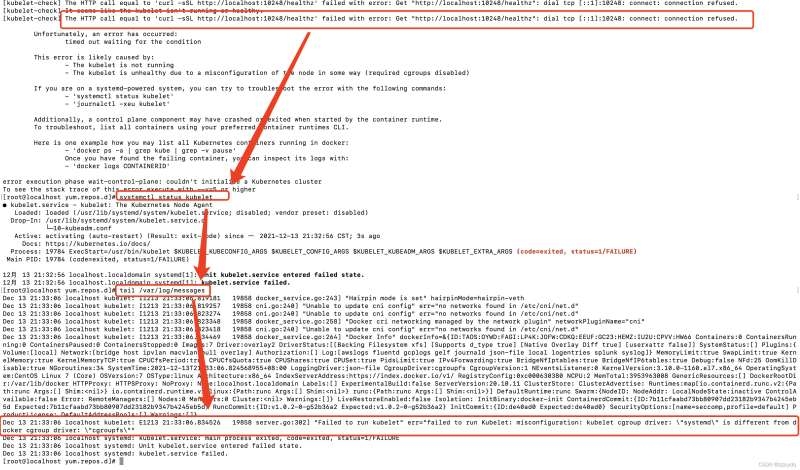
centos7系统部署k8s集群详细介绍_Linux
目录1 版本、规划1.1 版本信息:1.2集群规划2.部署1、关闭防火墙2、关闭selinux3、关闭swap4、添加主机名和IP对应关系5、将桥接的IPV4流量传递给iptables的链6、安装docker 安装:7、添加阿里云...
充分利用互联网资源的小tips-续集
挖掘src的时候找到一个资产如下 正常测试弱口令,未授权接口等无果 通过fofa搜索指纹,发现是一个通用的cms 把站点都薅下来,然后尝试弱口令,成功进入后台,顺便发现了一个这个后台的通用默认...
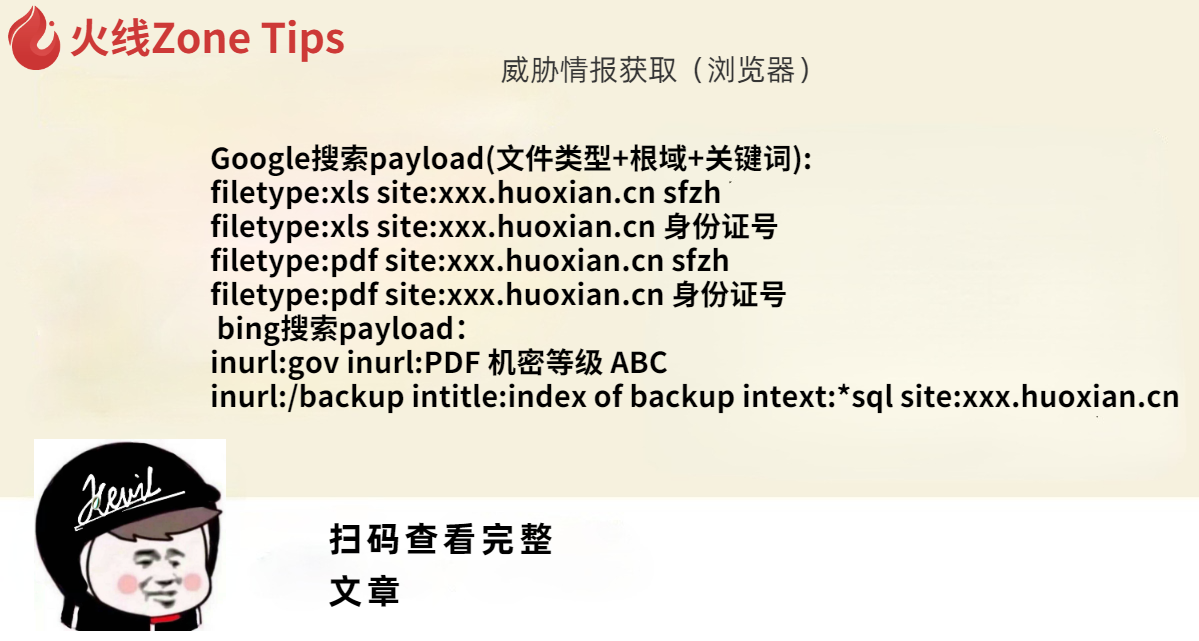
威胁情报获取(浏览器)
Google搜索payload(文件类型+根域+关键词): filetype:xls site:xxx.huoxian.cn sfzh filetype:xls site:xxx.huoxian.cn 身份证号 filetype:pdf site:xxx.huoxian.cn sfzh filetype:pdf site:xxx...
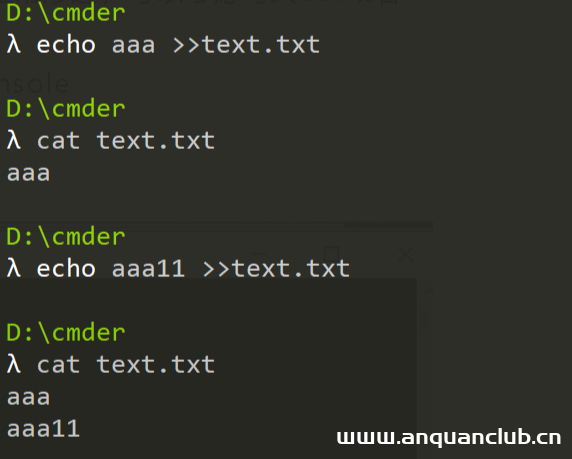
文件写入小技巧
在某些场景,我们可能需要写入bat,vbs,py等文件,当我们逐个echo将字符写入文件时,写入内容会自动换行: 可以通过命令 >>text.txt set/p='test' < nul 避免写入内容被换行 文字来源...
CVE-2021-25299: Nagios XI 5.7.5 – Cross-Site Scripting
漏洞标题 CVE-2021-25299: Nagios XI 5.7.5 - Cross-Site Scripting 漏洞描述 Nagios XI 5.7.5 contains a cross-site scripting vulnerability in the file /usr/local/nagiosxi/html/admin/ss...
CVE-2022-34487: ShortCode Addons – Unauthenticated Options Update
漏洞标题 CVE-2022-34487: ShortCode Addons - Unauthenticated Options Update 漏洞描述 WordPress plugin Shortcode Addons <= 3.0.2 contains an unauthenticated arbitrary option updat...
CVE-2025-46822: Java-springboot-codebase 1.1 – Arbitrary File Read
漏洞标题 CVE-2025-46822: Java-springboot-codebase 1.1 - Arbitrary File Read 漏洞描述 OsamaTaher/Java-springboot-codebase is a collection of Java and Spring Boot code snippets, appl...
CVE-2018-19127: PHPCMS 2008 – Remote Code Execution via Template Injection
漏洞标题 CVE-2018-19127: PHPCMS 2008 - Remote Code Execution via Template Injection 漏洞描述 PHPCMS 2008 suffers from an unauthenticated RCE via template injection in type.php, whe...
CVE-2017-7504: JBoss 4.x JBossMQ JMS 反序列化漏洞
漏洞标题 CVE-2017-7504: JBoss 4.x JBossMQ JMS 反序列化漏洞 漏洞描述 fofa: jbossmq PoC代码
CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 – Local File Inclusion
漏洞标题 CVE-2010-3426: Joomla! Component Jphone 1.0 Alpha 3 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in jphone.php in the JPhone (com_jphone) component ...
CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection
漏洞标题 CVE-2024-43917: WordPress TI WooCommerce Wishlist Plugin <= 2.8.2 - SQL Injection 漏洞描述 In the latest version (2.8.2 as of writing the article) and below, the plugin...
CVE-2024-9047: WordPress File Upload <= 4.24.11 - Arbitrary File Read
漏洞标题 CVE-2024-9047: WordPress File Upload <= 4.24.11 - Arbitrary File Read 漏洞描述 The WordPress File Upload plugin for WordPress is vulnerable to Path Traversal in all ver...
CVE-2014-3120: ElasticSearch v1.1.1/1.2 RCE
漏洞标题 CVE-2014-3120: ElasticSearch v1.1.1/1.2 RCE 漏洞描述 The default configuration in Elasticsearch before 1.2 enables dynamic scripting, which allows remote attackers to exec...

