





CVE-2025-10211: ChanCMS <= 3.3.0 - Server-Side Request Forgery
漏洞标题 CVE-2025-10211: ChanCMS <= 3.3.0 - Server-Side Request Forgery 漏洞描述 yanyutao0402 ChanCMS 3.3.0 contains a server-side request forgery caused by manipulation of the ...
CVE-2025-1974: CVE-2025-1974
漏洞标题 CVE-2025-1974: CVE-2025-1974 漏洞描述 shodan: ssl:"ingress-nginx" port:8443 Kubernetes ingress-nginx是云原生计算基金会(Cloud Native Computing Foundation)开源...
(CVE-2025-9242) WatchGuard Fireware OS 未授权远程代码执行漏洞
漏洞标题 (CVE-2025-9242) WatchGuard Fireware OS 未授权远程代码执行漏洞 漏洞描述 (CVE-2025-9242) WatchGuard Fireware OS 未授权远程代码执行漏洞 PoC代码 暂无
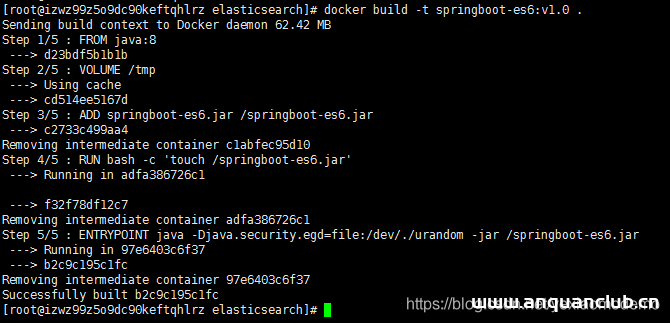
Docker运行springboot项目的实现_docker
这篇文章主要介绍了Docker运行springboot项目的实现,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友们下面随着小编来一起学习学习吧 简介: Docker...
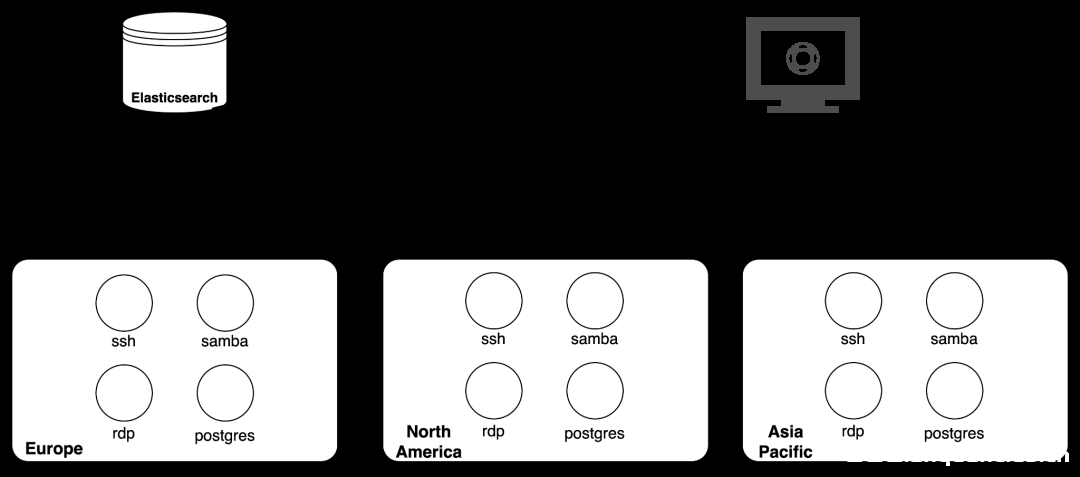
320个蜜罐其中80%在一天内沦陷
11月22日,网络安全公司Palo Alto Networks旗下威胁情报团队Unit 42公布了一份研究报告,报告中指出,该团队研究人员设置的320个蜜罐,其中的80%在24小时内被攻陷,而所有蜜罐都在一周内被攻陷...
CVE-2023-37645: EyouCms v1.6.3 – Information Disclosure
漏洞标题 CVE-2023-37645: EyouCms v1.6.3 - Information Disclosure 漏洞描述 EyouCms v1.6.3 was discovered to contain an information disclosure vulnerability via the component /custom...
CVE-2021-41878: i-Panel Administration System 2.0 – Cross-Site Scripting
漏洞标题 CVE-2021-41878: i-Panel Administration System 2.0 - Cross-Site Scripting 漏洞描述 i-Panel Administration System 2.0 contains a cross-site scripting vulnerability that enab...

zabbix-agent在麒麟V10上的安装过程_zabbix
这篇文章主要介绍了zabbix-agent在麒麟V10上的安装过程,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 1、安装包下载 下载地址:http://sourcefo...
CVE-2025-53364: Parse Server – GraphQL Schema Information Disclosure
漏洞标题 CVE-2025-53364: Parse Server - GraphQL Schema Information Disclosure 漏洞描述 The Parse Server GraphQL API previously allowed public access to the GraphQL schema without r...
CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668)
漏洞标题 CirCarLifeScada停车场自动化管理系统repository-信息泄漏(CVE-2018-16668) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circ...
CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway – Remote Code Injection
漏洞标题 CVE-2020-8194: Citrix ADC and Citrix NetScaler Gateway - Remote Code Injection 漏洞描述 Citrix ADC and NetScaler Gateway are susceptible to remote code injection. An attac...
CVE-2024-13159: Ivanti EPM – Credential Coercion Vulnerability in GetHashForWildcardRecursive
漏洞标题 CVE-2024-13159: Ivanti EPM - Credential Coercion Vulnerability in GetHashForWildcardRecursive 漏洞描述 A vulnerability in Ivanti Endpoint Manager (EPM) allows an unauthent...
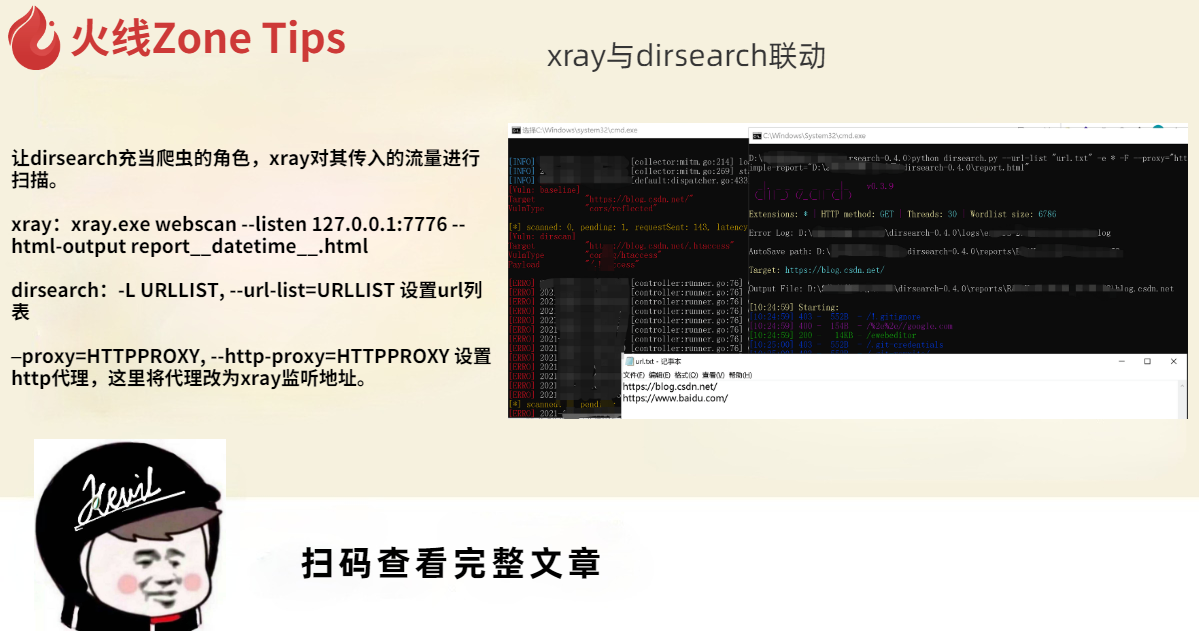
xray与dirsearch联动
让dirsearch充当爬虫的角色,xray对其传入的流量进行扫描。 xray:xray.exe webscan --listen 127.0.0.1:7776 --html-output reportdatetime.html dirsearch:-L URLLIST, --url-list=URLLIST ...
CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection
漏洞标题 CVE-2022-0783: Multiple Shipping Address Woocommerce < 2.0 - SQL Injection 漏洞描述 The Multiple Shipping Address Woocommerce plugin before 2.0 does not properly saniti...
CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal
漏洞标题 CVE-2021-21234: Spring Boot Actuator Logview Directory Traversal 漏洞描述 spring-boot-actuator-logview before version 0.2.13 contains a directory traversal vulnerability i...
CVE-2000-0760: Jakarta Tomcat 3.1 and 3.0 – Information Disclosure
漏洞标题 CVE-2000-0760: Jakarta Tomcat 3.1 and 3.0 - Information Disclosure 漏洞描述 Jakarta Tomcat 3.1 and 3.0 under Apache contain a vulnerability in the Snoop servlet that revea...

