





CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation
漏洞标题 CVE-2024-4898: WordPress InstaWP Connect <= 0.1.0.38 - Unauthenticated User Creation 漏洞描述 The InstaWP Connect – 1-click WP Staging & Migration plugin for WordP...
CVE-2024-51567: CyberPanel v2.3.6 Pre-Auth Remote Code Execution
漏洞标题 CVE-2024-51567: CyberPanel v2.3.6 Pre-Auth Remote Code Execution 漏洞描述 upgrademysqlstatus in databases/views.py in CyberPanel (aka Cyber Panel) before 5b08cd6 allows re...
CVE-2023-28432: MinIO Cluster Deployment – Information Disclosure
漏洞标题 CVE-2023-28432: MinIO Cluster Deployment - Information Disclosure 漏洞描述 MinIO is susceptible to information disclosure. In a cluster deployment starting with RELEASE.20...
CVE-2021-35250: SolarWinds Serv-U 15.3 – Directory Traversal
漏洞标题 CVE-2021-35250: SolarWinds Serv-U 15.3 - Directory Traversal 漏洞描述 SolarWinds Serv-U 15.3 is susceptible to local file inclusion, which may allow an attacker access to ...
CVE-2023-48084: Nagios XI < 5.11.3 - SQL Injection
漏洞标题 CVE-2023-48084: Nagios XI < 5.11.3 - SQL Injection 漏洞描述 SQL injection vulnerability in Nagios XI before version 5.11.3 via the bulk modification tool. PoC代码
CVE-2023-23752: Joomla! Webservice – Password Disclosure
漏洞标题 CVE-2023-23752: Joomla! Webservice - Password Disclosure 漏洞描述 An issue was discovered in Joomla! 4.0.0 through 4.2.7. An improper access check allows unauthorized acce...
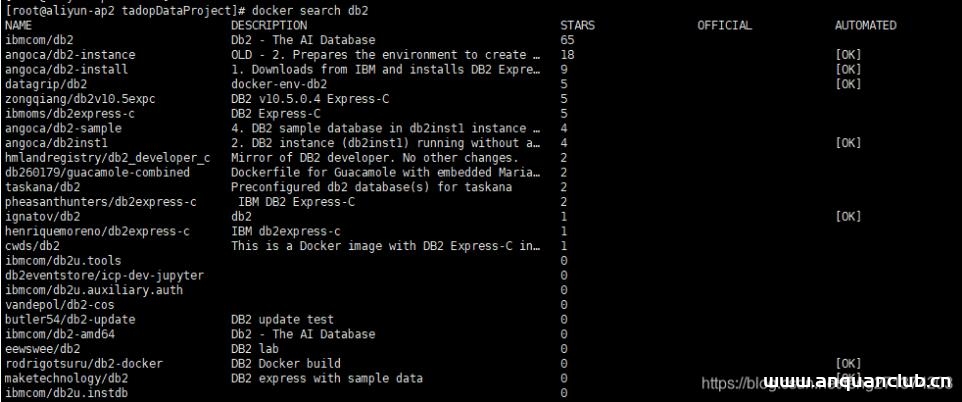
docker-compose安装db2数据库操作_docker
这篇文章主要介绍了docker-compose安装db2数据库操作,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 db2数据库在宿主机直接安装比较麻烦,而且涉及用户和权限也不方便,所...
CVE-2022-36923: Zoho ManageEngine – getUserAPIKey Authentication Bypass
漏洞标题 CVE-2022-36923: Zoho ManageEngine - getUserAPIKey Authentication Bypass 漏洞描述 Zoho ManageEngine OpManager, OpManager Plus, OpManager MSP, Network Configuration Manager,...
CVE-2025-6403: Code-Projects School Fees Payment System 1.0 – SQL Injection
漏洞标题 CVE-2025-6403: Code-Projects School Fees Payment System 1.0 - SQL Injection 漏洞描述 A vulnerability was found in code-projects School Fees Payment System 1.0. It has been...
CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 – SQL Injection
漏洞标题 CVE-2023-23489: WordPress Easy Digital Downloads 3.1.0.2/3.1.0.3 - SQL Injection 漏洞描述 WordPress Easy Digital Downloads plugin 3.1.0.2 and 3.1.0.3 contains a SQL inject...
5款超好用的开源 Docker工具强烈推荐_docker
这篇文章主要介绍了5款超好用的开源 Docker工具强烈推荐,这5个工具非常实用,有需要同学可以学习下 导读 Docker 社区已经创建了许多开源工具,它们能帮我们处理各种用例。作者在本文中推荐了 5...
CVE-2025-11371: Gladinet CentreStack & TrioFox – Local File Inclusion
漏洞标题 CVE-2025-11371: Gladinet CentreStack & TrioFox - Local File Inclusion 漏洞描述 In the default installation and configuration of Gladinet CentreStack and TrioFox, there...
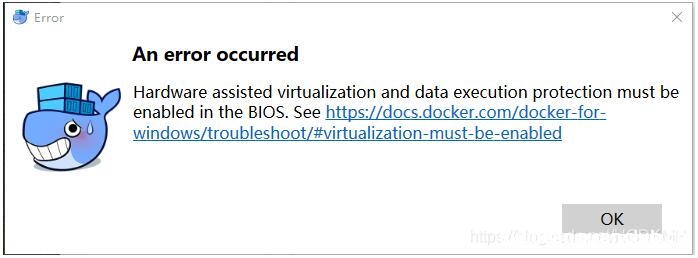
解决docker与vmware的冲突问题_docker
这篇文章主要介绍了解决docker与vmware的冲突问题,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 1、docker启动问题: 问题解决: 需要开启Hyper-V,(开启方法:控制面板-...
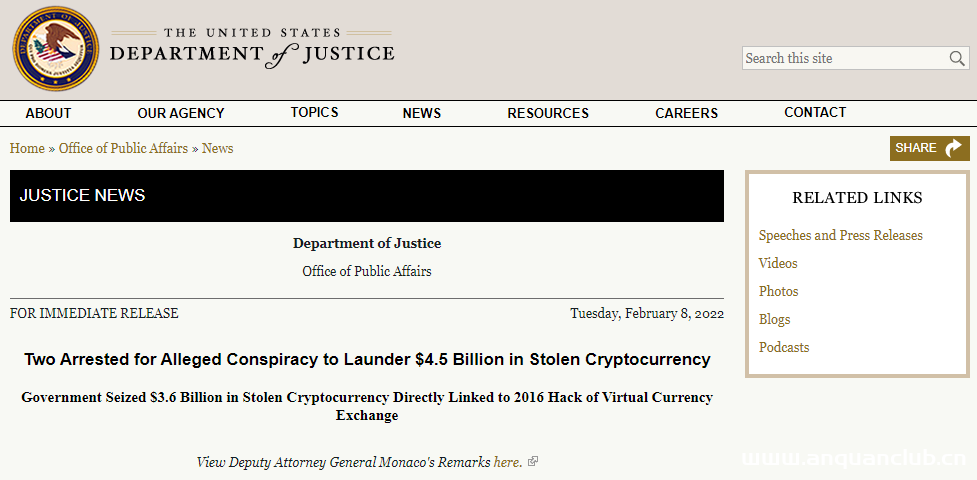
美国追回六年前黑客从Bitfinex窃取的现值36亿美元加密货币
2022年2月8日,美国司法部在一篇新闻稿中称,其以涉嫌共谋加密货币洗钱的罪名逮捕了一对夫妇,该案件涉及的加密货币价值约45亿美元,并且查明这些加密货币与六年前的一起黑客攻击案有关。总部设...
CVE-2024-24329: TotoLink Router setPortForwardRules – Command Injection
漏洞标题 CVE-2024-24329: TotoLink Router setPortForwardRules - Command Injection 漏洞描述 TOTOLINK A3300R V17.0.0cu.557_B20221024 was discovered to contain a command injection vuln...
CVE-2025-34040: Zhiyuan OA Platform – Arbitrary File Upload
漏洞标题 CVE-2025-34040: Zhiyuan OA Platform - Arbitrary File Upload 漏洞描述 An arbitrary file upload vulnerability exists in the Zhiyuan OA platform 5.0, 5.1 - 5.6sp1, 6.0 - 6.1s...

