





CVE-2024-53995: SickChill – Open Redirect
漏洞标题 CVE-2024-53995: SickChill - Open Redirect 漏洞描述 SickChill's login endpoint's 'next_' parameter accepts arbitrary content, allowing authenticated att...
CVE-2020-2103: Jenkins <=2.218 - Information Disclosure
漏洞标题 CVE-2020-2103: Jenkins <=2.218 - Information Disclosure 漏洞描述 Jenkins through 2.218, LTS 2.204.1 and earlier, is susceptible to information disclosure. An attacker c...
CVE-2012-0392: Apache Struts2 S2-008 RCE
漏洞标题 CVE-2012-0392: Apache Struts2 S2-008 RCE 漏洞描述 The CookieInterceptor component in Apache Struts before 2.3.1.1 does not use the parameter-name whitelist, which allows r...
CVE-2023-28432: MinIO Cluster Deployment – Information Disclosure
漏洞标题 CVE-2023-28432: MinIO Cluster Deployment - Information Disclosure 漏洞描述 MinIO is susceptible to information disclosure. In a cluster deployment starting with RELEASE.20...

Docker内网穿透frp部署实现过程解析_docker
这篇文章主要介绍了Docker内网穿透frp部署实现过程解析,文中通过示例代码介绍的非常详细,对大家的学习或者工作具有一定的参考学习价值,需要的朋友可以参考下 1.创建配置文件目录 cd /home目录 ...
CVE-2023-47218: QNAP QTS and QuTS Hero – OS Command Injection
漏洞标题 CVE-2023-47218: QNAP QTS and QuTS Hero - OS Command Injection 漏洞描述 An OS command injection vulnerability has been reported to affect several QNAP operating system vers...
CVE-2023-37679: NextGen Mirth Connect – Remote Code Execution
漏洞标题 CVE-2023-37679: NextGen Mirth Connect - Remote Code Execution 漏洞描述 Mirth Connect, by NextGen HealthCare, is an open source data integration platform widely used by hea...
CVE-2019-17662: ThinVNC 1.0b1 – Authentication Bypass
漏洞标题 CVE-2019-17662: ThinVNC 1.0b1 - Authentication Bypass 漏洞描述 ThinVNC 1.0b1 is vulnerable to arbitrary file read, which leads to a compromise of the VNC server. The vulne...
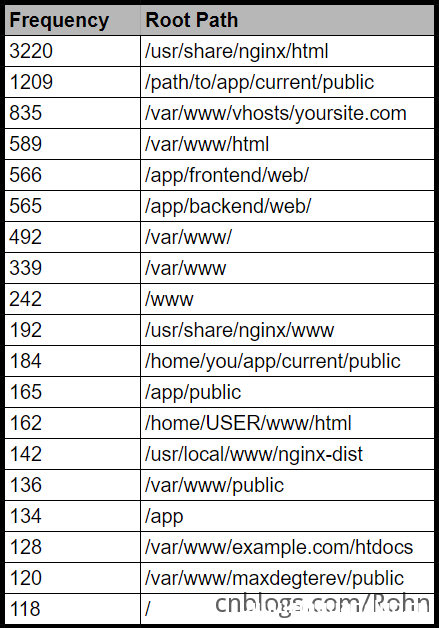
Nginx常见的错误配置举例_nginx
这篇文章主要介绍了Nginx常见的错误配置举例,帮助大家更好的理解和学习使用Nginx,感兴趣的朋友可以了解下 目录Missing root locationOff-By-SlashUnsafe variable useSCRIPT_NAMEUsage of $ur...
CVE-2020-8771: WordPress Time Capsule < 1.21.16 - Authentication Bypass
漏洞标题 CVE-2020-8771: WordPress Time Capsule < 1.21.16 - Authentication Bypass 漏洞描述 WordPress Time Capsule plugin before 1.21.16 for WordPress has an authentication bypass...
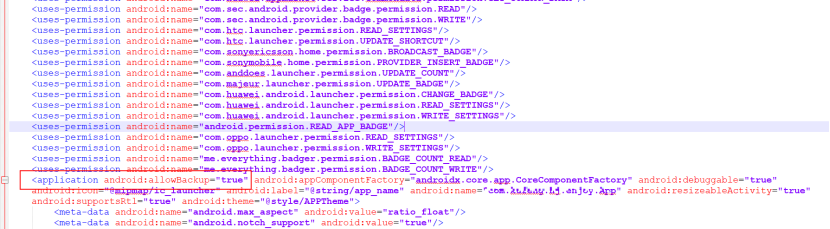
一个简单的Android-allowBackup漏洞记录
前言: 最近遇到个allowbackup-true的漏洞。在此做一个详细的记录,以下以某app为例,详细描述该漏洞的定义,复现过程及利用方式。 一、定义: Android官方对于这个属性的定义是,Android API L...
CVE-2025-41646: RevPi Webstatus <= v2.4.5 - Authentication Bypass
漏洞标题 CVE-2025-41646: RevPi Webstatus <= v2.4.5 - Authentication Bypass 漏洞描述 An unauthorized remote attacker can bypass the authentication of the affected software packag...
CVE-2021-24681: Duplicate Page WordPress – Stored Cross-Site Scripting
漏洞标题 CVE-2021-24681: Duplicate Page WordPress - Stored Cross-Site Scripting 漏洞描述 Duplicate Page WordPress plugin <= 4.4.2 contains a stored cross-site scripting caused b...
CVE-2025-51501: Microweber CMS2.0 – Cross-Site Scripting
漏洞标题 CVE-2025-51501: Microweber CMS2.0 - Cross-Site Scripting 漏洞描述 Reflected Cross-Site Scripting (XSS) in the `id` parameter of the `live_edit.module_settings` API endpoin...
CVE-2022-4260: WordPress WP-Ban <1.69.1 - Stored Cross-Site Scripting
漏洞标题 CVE-2022-4260: WordPress WP-Ban <1.69.1 - Stored Cross-Site Scripting 漏洞描述 WordPress WP-Ban plugin before 1.69.1 contains a stored cross-site scripting vulnerabilit...
Altenergy Power Control Software management_model.php存在命令注入漏洞(CVE-2023-28343)
漏洞标题 Altenergy Power Control Software management_model.php存在命令注入漏洞(CVE-2023-28343) 漏洞描述 Altenergy Power System Control Software是Altenergy PowerSystem公司的微型逆变...

