





CVE-2022-32195: Open edX <2022-06-06 - Cross-Site Scripting
漏洞标题 CVE-2022-32195: Open edX <2022-06-06 - Cross-Site Scripting 漏洞描述 Open edX before 2022-06-06 contains a reflected cross-site scripting vulnerability via the 'ne...
CVE-2019-8086: Adobe Experience Manager – XML External Entity Injection
漏洞标题 CVE-2019-8086: Adobe Experience Manager - XML External Entity Injection 漏洞描述 Adobe Experience Manager 6.5, 6.4, 6.3 and 6.2 are susceptible to XML external entity inje...
CVE-2024-47073: DataEase v2.10.2 – JWT Signature Verification Bypass
漏洞标题 CVE-2024-47073: DataEase v2.10.2 - JWT Signature Verification Bypass 漏洞描述 DataEase is an open source data visualization analysis tool that helps users quickly analyze ...
CVE-2022-27924: Zimbra Collaboration Suite – Memcached Command Injection
漏洞标题 CVE-2022-27924: Zimbra Collaboration Suite - Memcached Command Injection 漏洞描述 Zimbra Collaboration Suite versions 8.8.15 and 9.0 contain a memcached command injection ...
CVE-2022-34047: WAVLINK WN530HG4 – Improper Access Control
漏洞标题 CVE-2022-34047: WAVLINK WN530HG4 - Improper Access Control 漏洞描述 WAVLINK WN530HG4 M30HG4.V5030.191116 is susceptible to improper access control. An attacker can obtain ...
CVE-2025-47539: Eventin <= 4.0.26 - Privilege Escalation
漏洞标题 CVE-2025-47539: Eventin <= 4.0.26 - Privilege Escalation 漏洞描述 The Eventin WordPress plugin before 4.0.27 suffers from an unauthenticated privilege escalation vulner...
CVE-2023-35844: Lightdash Arbitrary File Read
漏洞标题 CVE-2023-35844: Lightdash Arbitrary File Read 漏洞描述 Lightdash是一款数据分析平台,它可以让数据团队和其他业务部门聚集在一起以做出更好的数据驱动决策 Lightdash 0.510.3之前...

docker volumes 文件映射方式_docker
这篇文章主要介绍了docker volumes 文件映射的实例讲解,具有很好的参考价值,希望对大家有所帮助。一起跟随小编过来看看吧 背景 在做区块链日志模块时,如果容器运行,需要把日志文件映射到宿...
CVE-2020-14864: Oracle Fusion – Directory Traversal/Local File Inclusion
漏洞标题 CVE-2020-14864: Oracle Fusion - Directory Traversal/Local File Inclusion 漏洞描述 Oracle Business Intelligence Enterprise Edition 5.5.0.0.0, 12.2.1.3.0, and 12.2.1.4.0 are...
Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759)
漏洞标题 Apache Tomcat JK (mod_jk) 连接器-目录遍历(CVE-2018-11759) 漏洞描述 【漏洞描述】 Apache Tomcat JK(mod_jk) 【涉及版本】1.2.0,1.2.4 【漏洞描述】 由于Apache TomcatWeb服务器(...
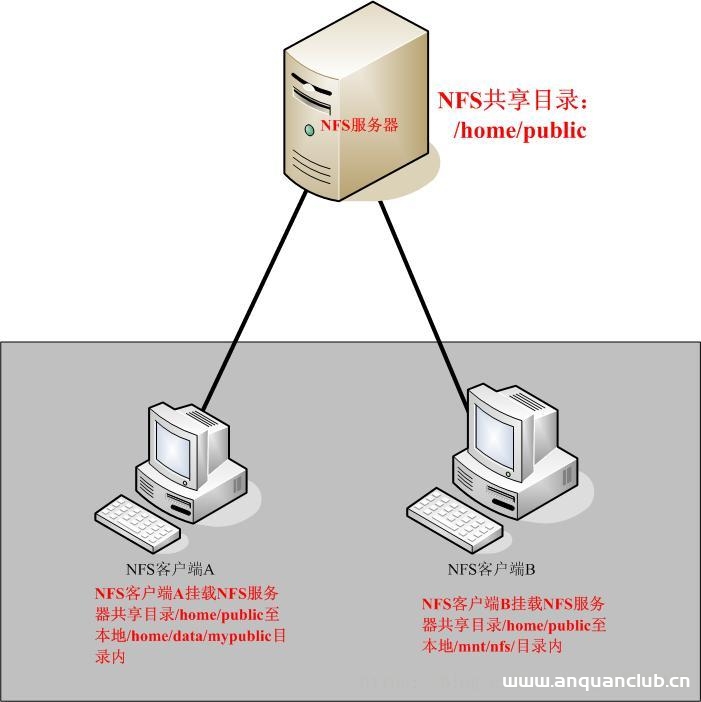
浅析NFS服务器原理以及搭建配置部署步骤_服务器其它
本文对NFS服务器原理作了简要的分析,对NFS服务器的搭建配置步骤作了详细的图文描述,有需要的朋友可以借鉴参考下,希望可以对你有所帮助 目录NFS服务简介什么是NFS?NFS挂载原理NFS服务器到底...
CVE-2023-30869: Easy Digital Downloads – Privilege Escalation
漏洞标题 CVE-2023-30869: Easy Digital Downloads - Privilege Escalation 漏洞描述 Improper Authentication vulnerability in Easy Digital Downloads plugin allows unauth. Privilege Esca...
CVE-2020-9484: Apache Tomcat Remote Command Execution
漏洞标题 CVE-2020-9484: Apache Tomcat Remote Command Execution 漏洞描述 When using Apache Tomcat versions 10.0.0-M1 to 10.0.0-M4, 9.0.0.M1 to 9.0.34, 8.5.0 to 8.5.54 and 7.0.0 to 7...
CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 – Improper Access Control
漏洞标题 CVE-2022-38817: Dapr Dashboard 0.1.0-0.10.0 - Improper Access Control 漏洞描述 Dapr Dashboard 0.1.0 through 0.10.0 is susceptible to improper access control. An attacker c...
CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server – Authentication Bypass
漏洞标题 CVE-2021-31602: Hitachi Vantara Pentaho/Business Intelligence Server - Authentication Bypass 漏洞描述 Hitachi Vantara Pentaho through 9.1 and Pentaho Business Intelligence...
CVE-2022-2414: FreeIPA – XML Entity Injection
漏洞标题 CVE-2022-2414: FreeIPA - XML Entity Injection 漏洞描述 Access to external entities when parsing XML documents can lead to XML external entity (XXE) attacks. This flaw allo...

