






CVE-2022-22963: Spring Cloud – Remote Code Execution
漏洞标题 CVE-2022-22963: Spring Cloud - Remote Code Execution 漏洞描述 Spring Cloud Function versions 3.1.6, 3.2.2 and older unsupported versions are susceptible to remote code exe...
CVE-2019-16469: Adobe Experience Manager – Expression Language Injection
漏洞标题 CVE-2019-16469: Adobe Experience Manager - Expression Language Injection 漏洞描述 Adobe Experience Manager versions 6.5, 6.4, 6.3, 6.2, 6.1, and 6.0 has an expression lang...
CVE-2025-54249: Adobe Experience Manager ≤ 6.5.23.0 – SSRF
漏洞标题 CVE-2025-54249: Adobe Experience Manager ≤ 6.5.23.0 – SSRF 漏洞描述 Adobe Experience Manager versions 6.5.23.0 and earlier are affected by a Server-Side Request Forgery ...
CVE-2022-4320: WordPress Events Calendar <1.4.5 - Cross-Site Scripting
漏洞标题 CVE-2022-4320: WordPress Events Calendar <1.4.5 - Cross-Site Scripting 漏洞描述 WordPress Events Calendar plugin before 1.4.5 contains multiple cross-site scripting vul...
CVE-2018-6961: VMware NSX SD-WAN Edge – Command Injection
漏洞标题 CVE-2018-6961: VMware NSX SD-WAN Edge - Command Injection 漏洞描述 VMware NSX SD-WAN Edge (formerly VeloCloud Edge) before 3.1.2 contains an unauthenticated command inject...
(CVE-2024-32737) CyberPower PowerPanel Enterprise SQL注入漏洞 注入漏洞
漏洞标题 (CVE-2024-32737) CyberPower PowerPanel Enterprise SQL注入漏洞 注入漏洞 漏洞描述 (CVE-2024-32737) CyberPower PowerPanel Enterprise SQL注入漏洞 注入漏洞 PoC代码 暂无
CVE-2021-27358: Grafana Unauthenticated Snapshot Creation
漏洞标题 CVE-2021-27358: Grafana Unauthenticated Snapshot Creation 漏洞描述 Grafana 6.7.3 through 7.4.1 snapshot functionality can allow an unauthenticated remote attacker to trigg...
CVE-2022-1388: F5 BIG-IP iControl – REST Auth Bypass RCE
漏洞标题 CVE-2022-1388: F5 BIG-IP iControl - REST Auth Bypass RCE 漏洞描述 F5 BIG-IP 16.1.x versions prior to 16.1.2.2, 15.1.x versions prior to 15.1.5.1, 14.1.x versions prior to ...
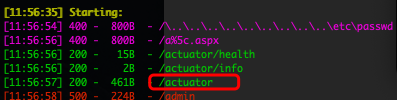
dirsearch+ fuzzDicts 目录fuzz大法
最近在研究目录fuzz,有时候我们在扫描网站目录的时候常常只是对网站根目录进行了扫描,从而所发现的问题点不太全面,这里就跟大家分享下我的目录fuzz大法~~ 工具 1)dirsearch 常用的参数有 ...

ubuntu环境下的php相关路径与修改方法_Linux
这篇文章主要介绍了ubuntu环境下的php相关的路径,需要的朋友可以参考下 ubuntu环境下的php相关的路径 php路径 /usr/bin/php phpize5 /usr/bin/phpize5 php5-fpm /usr/sbin/php5-fpm php所有的配...
大壮的信息源
自学成才的黑客(安全研究员)是从哪学到那些知识的? http://www.zhihu.com/question/23073812/answer/23563575 正如上面的乎友所说:现在获取信息的渠道越来越多,每天新增的技术文章早已超出...
CVE-2023-47246: SysAid-On-premise远程代码执行漏洞
漏洞标题 CVE-2023-47246: SysAid-On-premise远程代码执行漏洞 漏洞描述 Sysaid Technologies SysAid是以色列Sysaid Technologies公司的一套IT服务管理解决方案。SysAid On-Premise是SysAid的本...
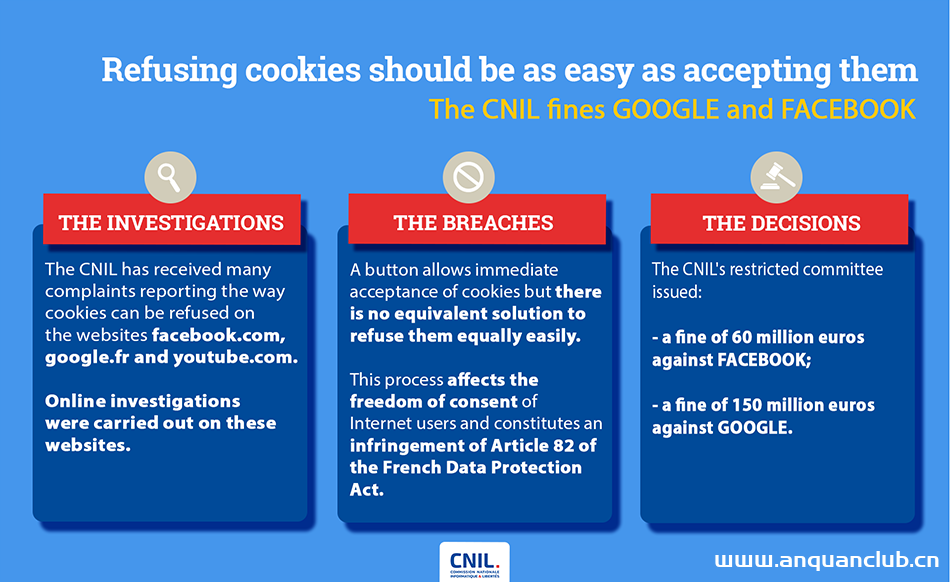
法国罚谷歌脸书共2.1亿欧元,因用户无法简单拒绝Cookie
上周,法国数据保护监管机构国家信息自由委员会(CNIL)对Facebook和谷歌分别处以了1.5亿欧元和6000万欧元的罚款,因为它们违反了《法国数据保护法》,未能为用户提供拒绝Cookie的简单方式。CNI...
CVE-2025-13486: Advanced Custom Fields Extended < 0.9.2 - Remote Code Execution
漏洞标题 CVE-2025-13486: Advanced Custom Fields Extended < 0.9.2 - Remote Code Execution 漏洞描述 Advanced Custom Fields: Extended WordPress plugin 0.9.0.5 through 0.9.1.1 conta...
CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop
漏洞标题 CVE-2005-0851: FileZilla Server < 0.9.6 - DoS via MODE Z Infinite Loop 漏洞描述 FileZilla Server versions prior to 0.9.6 are vulnerable to denial of service when using ...
CVE-2022-4325: WordPress Post Status Notifier Lite <1.10.1 - Cross-Site Scripting
漏洞标题 CVE-2022-4325: WordPress Post Status Notifier Lite <1.10.1 - Cross-Site Scripting 漏洞描述 WordPress Post Status Notifier Lite plugin before 1.10.1 contains a cross-sit...

