





CVE-2022-34267: RWS WorldServer – Authentication Bypass
漏洞标题 CVE-2022-34267: RWS WorldServer - Authentication Bypass 漏洞描述 An issue was discovered in RWS WorldServer before 11.7.3. Adding a token parameter with the value of 02 by...
CVE-2014-4558: WooCommerce Swipe <= 2.7.1 - Cross-Site Scripting
漏洞标题 CVE-2014-4558: WooCommerce Swipe <= 2.7.1 - Cross-Site Scripting 漏洞描述 A cross-site scripting vulnerability in test-plugin.php in the Swipe Checkout for WooCommerce ...
CVE-2015-1503: IceWarp Mail Server <11.1.1 - Directory Traversal
漏洞标题 CVE-2015-1503: IceWarp Mail Server <11.1.1 - Directory Traversal 漏洞描述 IceWarp Mail Server versions prior to 11.1.1 suffer from a directory traversal vulnerability. ...
CVE-2023-27032: PrestaShop AdvancedPopupCreator – SQL Injection
漏洞标题 CVE-2023-27032: PrestaShop AdvancedPopupCreator - SQL Injection 漏洞描述 In the module “Advanced Popup Creator” (advancedpopupcreator) from Idnovate for PrestaShop, a gu...
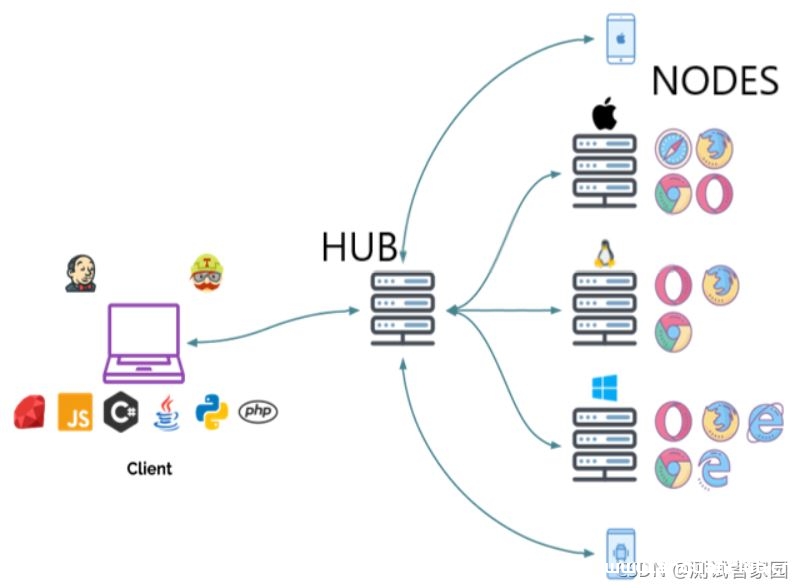
基于Docker+Selenium Grid的测试技术应用示例代码_docker
Selenium Grid允许我们在多台计算机上并行运行测试,并集中管理不同的浏览器版本和浏览器配置。这篇文章给大家介绍基于Docker+Selenium Grid的测试技术应用示例代码,需要的朋友参考下吧 Seleni...
CVE-2024-6746: EasySpider 0.6.2 – Arbitrary File Read
漏洞标题 CVE-2024-6746: EasySpider 0.6.2 - Arbitrary File Read 漏洞描述 A vulnerability classified as problematic was found in NaiboWang EasySpider 0.6.2 on Windows. Affected by th...
CirCarLifeScada停车场自动化管理系统log-信息泄漏(CVE-2018-12634)
漏洞标题 CirCarLifeScada停车场自动化管理系统log-信息泄漏(CVE-2018-12634) 漏洞描述 【漏洞对象】Circontrol CirCarLife Scada 【漏洞描述】 Circontrol CirCarLifeScada是西班牙Circontrol...
CVE-2010-1475: Joomla! Component Preventive And Reservation 1.0.5 – Local File Inclusion
漏洞标题 CVE-2010-1475: Joomla! Component Preventive And Reservation 1.0.5 - Local File Inclusion 漏洞描述 A directory traversal vulnerability in the Preventive & Reservation (...
CVE-2024-28995: SolarWinds Serv-U – Directory Traversal
漏洞标题 CVE-2024-28995: SolarWinds Serv-U - Directory Traversal 漏洞描述 SolarWinds Serv-U was susceptible to a directory transversal vulnerability that would allow access to read...
CVE-2025-27892: Shopware < 6.5.8.13 - SQL Injection
漏洞标题 CVE-2025-27892: Shopware < 6.5.8.13 - SQL Injection 漏洞描述 The Shopware application API contains a search functionality which enables users to search through informat...
CVE-2021-35250: SolarWinds Serv-U 15.3 – Directory Traversal
漏洞标题 CVE-2021-35250: SolarWinds Serv-U 15.3 - Directory Traversal 漏洞描述 SolarWinds Serv-U 15.3 is susceptible to local file inclusion, which may allow an attacker access to ...
CVE-2024-13726: Themes Coder Ecommerce <= 1.3.4 - SQL Injection
漏洞标题 CVE-2024-13726: Themes Coder Ecommerce <= 1.3.4 - SQL Injection 漏洞描述 The Themes Coder Ecommerce WordPress plugin through 1.3.4 does not properly sanitise and escape...
CVE-2023-27640: PrestaShop tshirtecommerce – Directory Traversal
漏洞标题 CVE-2023-27640: PrestaShop tshirtecommerce - Directory Traversal 漏洞描述 The Custom Product Designer (tshirtecommerce) module for PrestaShop allows HTTP requests to be fo...
CVE-2024-45440: Drupal 11.x-dev – Full Path Disclosure
漏洞标题 CVE-2024-45440: Drupal 11.x-dev - Full Path Disclosure 漏洞描述 core/authorize.php in Drupal 11.x-dev allows Full Path Disclosure (even when error logging is None) if the ...
CVE-2022-21371: Oracle WebLogic Server Local File Inclusion
漏洞标题 CVE-2022-21371: Oracle WebLogic Server Local File Inclusion 漏洞描述 An easily exploitable local file inclusion vulnerability allows unauthenticated attackers with network...
CVE-2021-41691: openSIS Student Information System 8.0 SQL Injection
漏洞标题 CVE-2021-41691: openSIS Student Information System 8.0 SQL Injection 漏洞描述 openSIS Student Information System version 8.0 is susceptible to SQL injection via the studen...

