





CVE-2020-12832: WordPress Simple File List – Path Traversal
漏洞标题 CVE-2020-12832: WordPress Simple File List - Path Traversal 漏洞描述 Simple File List plugin allows path traversal via file upload, enabling files to be written outside th...
CVE-2025-47204: Bootstrap Multiselect <= 1.1.2 - Cross-Site Scripting
漏洞标题 CVE-2025-47204: Bootstrap Multiselect <= 1.1.2 - Cross-Site Scripting 漏洞描述 A PHP script in the source code release echoes arbitrary POST data. If a developer adopts...
CVE-2017-12149: Java/Jboss Deserialization [RCE]
漏洞标题 CVE-2017-12149: Java/Jboss Deserialization [RCE] 漏洞描述 In Jboss Application Server as shipped with Red Hat Enterprise Application Platform 5.2, it was found that the do...
CVE-2024-25608: Liferay Portal – Open Redirect
漏洞标题 CVE-2024-25608: Liferay Portal - Open Redirect 漏洞描述 HtmlUtil.escapeRedirect in Liferay Portal 7.2.0 through 7.4.3.18, and older unsupported versions, and Liferay DXP 7...
Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518)
漏洞标题 Atlassian Confluence /json/setup-restore.action 文件上传漏洞(CVE-2023-22518) 漏洞描述 Atlassian Confluence是一款企业知识管理与协作软件。该漏洞存在于Atlassian Confluence...
CVE-2022-0422: WordPress White Label CMS <2.2.9 - Cross-Site Scripting
漏洞标题 CVE-2022-0422: WordPress White Label CMS <2.2.9 - Cross-Site Scripting 漏洞描述 WordPress White Label CMS plugin before 2.2.9 contains a reflected cross-site scripting ...
CVE-2017-12611: Apache Struts2 S2-053 – Remote Code Execution
漏洞标题 CVE-2017-12611: Apache Struts2 S2-053 - Remote Code Execution 漏洞描述 Apache Struts 2.0.0 through 2.3.33 and 2.5 through 2.5.10.1 uses an unintentional expression in a Fr...
CVE-2023-4169: 锐捷(ruijie)RG-EW1200G路由器 未授权后台登录密码修改(谨慎使用)
漏洞标题 CVE-2023-4169: 锐捷(ruijie)RG-EW1200G路由器 未授权后台登录密码修改(谨慎使用) 漏洞描述 Ruijie Networks RG-EW1200G是中国锐捷网络(Ruijie Networks)公司的一款无线路由器。 ...
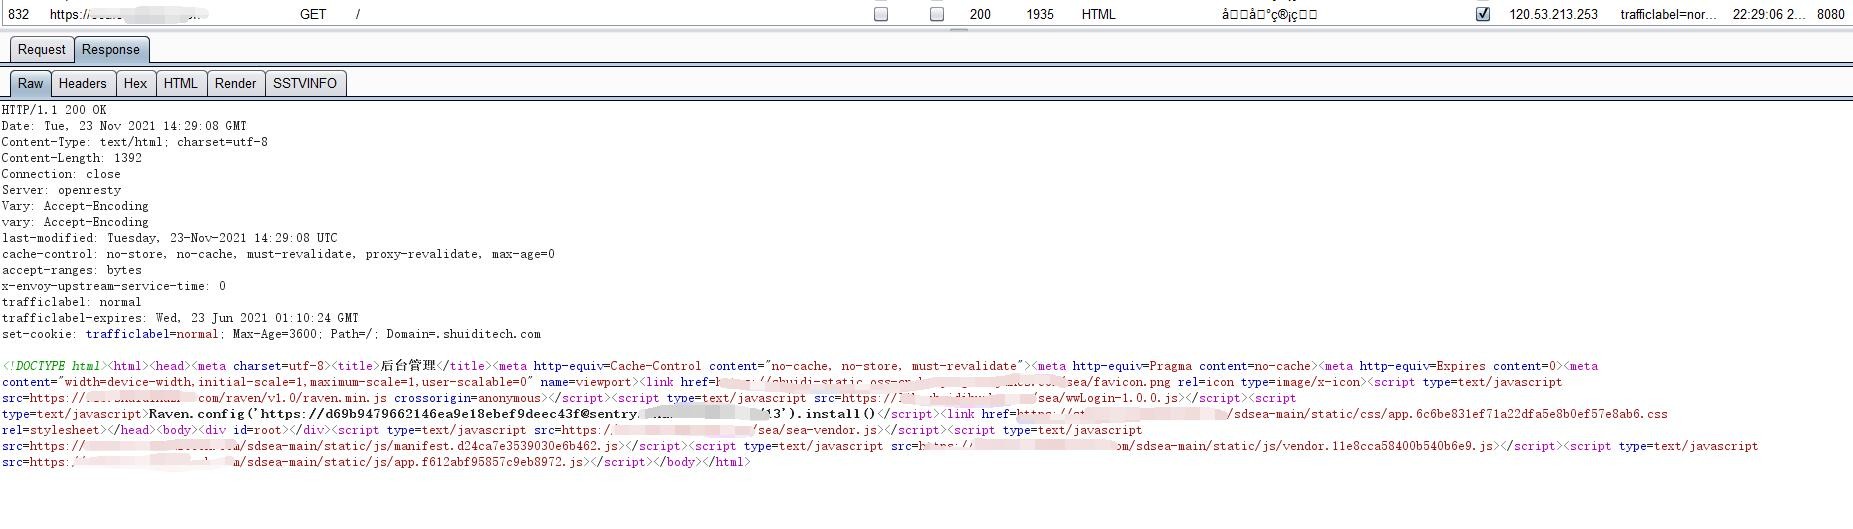
挖掘后台api的未授权访问漏洞
现在越来越多的网站前后端分离,javascript代码基本都会使用webpack这样的工具进行打包,打包过后的javascript代码会被混淆压缩,一个js文件就上万行代码,增加了读取javascript源码业务逻辑的...
Apache RocketMQ CVE-2023-37582 远程代码执行漏洞
漏洞标题 Apache RocketMQ CVE-2023-37582 远程代码执行漏洞 漏洞描述 Apache RocketMQ CVE-2023-37582 远程 PoC代码 暂无
CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass
漏洞标题 CVE-2018-18264: Kubernetes Dashboard <1.10.1 - Authentication Bypass 漏洞描述 Kubernetes Dashboard before 1.10.1 allows attackers to bypass authentication and use Dashb...
CVE-2025-34045: WeiPHP 5.0 – Path Traversal
漏洞标题 CVE-2025-34045: WeiPHP 5.0 - Path Traversal 漏洞描述 WeiPHP 5.0 contains a path traversal caused by insufficient input validation of the picUrl parameter in /public/index....
CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 – Unauthenticated Remote Command Execution
漏洞标题 CVE-2021-40539: Zoho ManageEngine ADSelfService Plus v6113 - Unauthenticated Remote Command Execution 漏洞描述 Zoho ManageEngine ADSelfService Plus version 6113 and prior ...
CVE-2018-8719: WordPress WP Security Audit Log 3.1.1 – Information Disclosure
漏洞标题 CVE-2018-8719: WordPress WP Security Audit Log 3.1.1 - Information Disclosure 漏洞描述 WordPress WP Security Audit Log 3.1.1 plugin is susceptible to information disclosur...
CVE-2017-9805: Apache Struts2 S2-052 – Remote Code Execution
漏洞标题 CVE-2017-9805: Apache Struts2 S2-052 - Remote Code Execution 漏洞描述 The REST Plugin in Apache Struts 2.1.1 through 2.3.x before 2.3.34 and 2.5.x before 2.5.13 uses an XS...
CVE-2023-39676: PrestaShop fieldpopupnewsletter Module – Cross Site Scripting
漏洞标题 CVE-2023-39676: PrestaShop fieldpopupnewsletter Module - Cross Site Scripting 漏洞描述 Fieldpopupnewsletter Prestashop Module v1.0.0 was discovered to contain a reflected ...

