





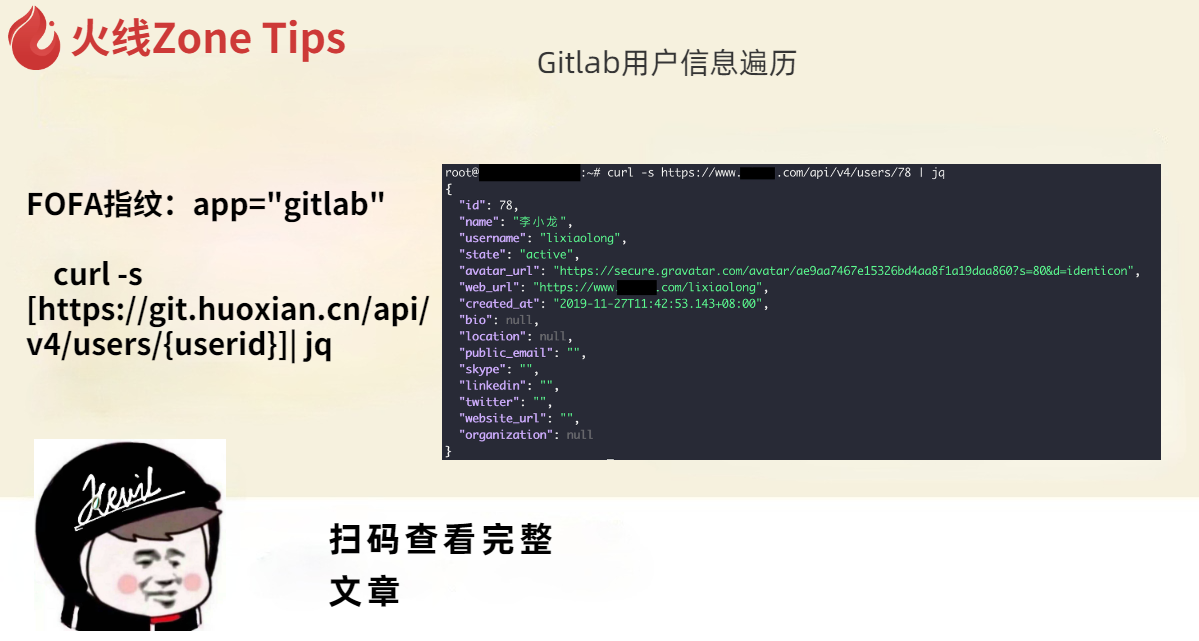
Gitlab用户信息遍历
FOFA指纹:app='gitlab' curl -s http://git.huoxian.cn/api/v4/users/{userid} | jq 文字来源于- 火线 Zone-云安全社区,安全小天地只做文章分享,如有侵权,请联系站长删除

CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution
漏洞标题 CVE-2021-3287: Zoho ManageEngine OpManager < 12.5.329 - Remote Code Execution 漏洞描述 Zoho ManageEngine OpManager before 12.5.329 contains a remote code execution caus...
CVE-2017-18493: Custom Admin Page by BestWebSoft < 0.1.2 - Cross-Site Scripting
漏洞标题 CVE-2017-18493: Custom Admin Page by BestWebSoft < 0.1.2 - Cross-Site Scripting 漏洞描述 The custom-admin-page plugin before 0.1.2 for WordPress has multiple XSS issues...
CVE-2023-43261: Milesight Routers – Information Disclosure
漏洞标题 CVE-2023-43261: Milesight Routers - Information Disclosure 漏洞描述 A critical security vulnerability has been identified in Milesight Industrial Cellular Routers, comprom...
CVE-2012-0394: Apache Struts <2.3.1.1 - Remote Code Execution
漏洞标题 CVE-2012-0394: Apache Struts <2.3.1.1 - Remote Code Execution 漏洞描述 Apache Struts before 2.3.1.1 is susceptible to remote code execution. When developer mode is used...
CVE-2021-28854: VICIdial Sensitive Information Disclosure
漏洞标题 CVE-2021-28854: VICIdial Sensitive Information Disclosure 漏洞描述 VICIdial's Web Client is susceptible to information disclosure because it contains many sensitive f...
CVE-2024-48766: NetAlert X – Arbitary File Read
漏洞标题 CVE-2024-48766: NetAlert X - Arbitary File Read 漏洞描述 A directory traversal vulnerability has been identified in NetAlertX versions v24.7.18 - v24.9.12. PoC代码
CVE-2025-61757: Oracle Identity Manager REST WebServices – Authentication Bypass
漏洞标题 CVE-2025-61757: Oracle Identity Manager REST WebServices - Authentication Bypass 漏洞描述 Vulnerability in the Identity Manager product of Oracle Fusion Middleware (compon...
Check Point Security Gateways CVE-2024-24919 任意文件读取漏洞
漏洞标题 Check Point Security Gateways CVE-2024-24919 任意文件读取漏洞 漏洞描述 Check Point Security Gateways中存在任意文件读取漏洞,此漏洞是由于MyCRL接口未充分验证用户输入的数据所...
CVE-2023-3849: mooDating 1.2 – Cross-site scripting
漏洞标题 CVE-2023-3849: mooDating 1.2 - Cross-site scripting 漏洞描述 A vulnerability, which was classified as problematic, was found in mooSocial mooDating 1.2. Affected is an unk...
CVE-2022-2488: Wavlink WN535K2/WN535K3 – OS Command Injection
漏洞标题 CVE-2022-2488: Wavlink WN535K2/WN535K3 - OS Command Injection 漏洞描述 Wavlink WN535K2 and WN535K3 routers are susceptible to OS command injection in /cgi-bin/touchlist_sy...
CVE-2020-23972: Joomla! Component GMapFP 3.5 – Arbitrary File Upload
漏洞标题 CVE-2020-23972: Joomla! Component GMapFP 3.5 - Arbitrary File Upload 漏洞描述 Joomla! Component GMapFP 3.5 is vulnerable to arbitrary file upload vulnerabilities. An attac...
CVE-2025-6970: WordPress Events Manager <= 7.0.3 - SQL Injection
漏洞标题 CVE-2025-6970: WordPress Events Manager <= 7.0.3 - SQL Injection 漏洞描述 The Events Manager - Calendar, Bookings, Tickets, and more! plugin for WordPress is vulnerable...
CVE-2019-9922: Joomla! Harmis Messenger 1.2.2 – Local File Inclusion
漏洞标题 CVE-2019-9922: Joomla! Harmis Messenger 1.2.2 - Local File Inclusion 漏洞描述 Joomla! Harmis Messenger 1.2.2 is vulnerable to local file inclusion which could give an atta...
CVE-2019-10758: mongo-express Remote Code Execution
漏洞标题 CVE-2019-10758: mongo-express Remote Code Execution 漏洞描述 mongo-express before 0.54.0 is vulnerable to remote code execution via endpoints that uses the `toBSON` method...

Docker 动态修改容器端口映射的方法_docker
这篇文章主要介绍了Docker 动态修改容器端口映射的方法,本文给大家介绍的非常详细,对大家的学习或工作具有一定的参考借鉴价值,需要的朋友可以参考下 前言:Docker端口映射往往是Docker Run命...

